CWE-754
Allowed-with-ReviewImproper Check for Unusual or Exceptional Conditions
Abstraction: Class · Status: Incomplete
The product does not check or incorrectly checks for unusual or exceptional conditions that are not expected to occur frequently during day to day operation of the product.
974 vulnerabilities reference this CWE, most recent first.
GHSA-CMH9-RX85-XJ38
Vulnerability from github – Published: 2024-02-13 18:34 – Updated: 2024-02-20 16:40Summary
Cross site scripting (XSS) potentially exposing cookies / sessions / localStorage, fixed by sidekiq-unique-jobs v8.0.7.
Specifically, this is a Reflected (Server-Side), Non-Self, Cross Site Scripting vulnerability, considered a P3 on the BugCrowd taxonomy with the following categorization: Cross-Site Scripting (XSS) > Reflected > Non-Self
It was initially thought there was a second vulnerability (RCE), but it was a false alarm. Injection is impossible with Redis:
String escaping and NoSQL injection The Redis protocol has no concept of string escaping, so injection is impossible under normal circumstances using a normal client library. The protocol uses prefixed-length strings and is completely binary safe.
Ref: https://redis.io/docs/management/security/
XSS Vulnerability
Specially crafted GET request parameters handled by any of the following endpoints of sidekiq-unique-jobs' "admin" web UI, allow a super-user attacker, or an unwitting, but authorized, victim, who has received a disguised / crafted link, to successfully execute malicious code, which could potentially steal cookies, session data, or local storage data from the app the sidekiq-unique-jobs web UI is mounted in.
/changelogs/locks/expiring_locks
This means if your sidekiq-unique-jobs web UI is mounted at /sidekiq, the vulnerable paths are:
/sidekiq/changelogs/sidekiq/locks/sidekiq/expiring_locks
XSS vulnerability is an instance of CAPEC-32: XSS Through HTTP Query Strings, which is related to CWE-80. In certain cases where it results in a server error with status 500, it could be considered a vector for uncontrolled resource consumption, given that errors can be much more resource intensive that normal requests, and thus CWE-400 & CWE-754 may also be relevant.
Details
Fix for the XSS vulnerability was released in sidekiq-unique-jobs v8.0.7.
This is an analogous attack vector to that which affected sidekiq gem from version v7.0.4 to v7.0.7, and was given identifiers GHSA-h3r8-h5qw-4r35 & CVE-2023-1892.
The vulnerability in sidekiq-unique-jobs' was not fixed by sidekiq v7.0.8, nor the more recent sidekiq v7.2.0 releases; they are similar but unrelated, distinct vulnerabilities in adjacent projects.
Note #1: The admin web UI for sidekiq-unique-jobs is not protected by any authorization constraint in the default configuration. Auth constraints must be configured by the programmer. It is recommended and expected that users will configure authorization constrains on the "admin" UI. This is not specifically related to the vulnerability but may make users who fail to constrain their "admin" UI even more vulnerable.
Note #2: Most users of the library will not have configured the UI on a sandboxed subdomain, making all their cookies, localStorage data and session secrets vulnerable to exposure. The purpose of a sandboxed subdomain is expressly to prevent leaking sensitive data through XSS attacks.
XSS Fix PR: https://github.com/mhenrixon/sidekiq-unique-jobs/pull/829
PoC
XSS
Use a string like:
%22%3E%3Cimg/src/onerror=alert(document.domain)%3E
as the value for one of the parameters that are handled without escaping. Reference: https://liveoverflow.com/do-not-use-alert-1-in-xss/
- Visit /sidekiq/changelogs - with a crafted query string like one of the following:
a. Screenshot:
b.
filteris XSS vulnerable:?filter=%22%3E%3Cimg/src/onerror=alert(document.domain)%3Ec.countis vulnerable to triggering an application error (status 500), potentially allowing resource exhaustion?count=%22%3E%3Cimg/src/onerror=alert(document.domain)%3E- Screenshot:
- Screenshot:
- Visit /sidekiq/locks - with a crafted query string like one of the following:
a. Screenshot:
b.
filteris XSS vulnerable:?filter=%22%3E%3Cimg/src/onerror=alert(document.domain)%3Ec.countis vulnerable to triggering an application error (status 500), potentially allowing resource exhaustion?count=%22%3E%3Cimg/src/onerror=alert(document.domain)%3E- Screenshot:
- Screenshot:
- Visit /sidekiq/expiring_locks - with a crafted query string like one of the following:
a. Screenshot:
b.
filteris XSS vulnerable:?filter=%22%3E%3Cimg/src/onerror=alert(document.domain)%3E
Impact
This is a vulnerability of critical severity, which impacts many thousands of sites, since sidekiq-unique-jobs is widely deployed across the industry, with multiple attack vectors.
{
"affected": [
{
"package": {
"ecosystem": "RubyGems",
"name": "sidekiq-unique-jobs"
},
"ranges": [
{
"events": [
{
"introduced": "8.0.0"
},
{
"fixed": "8.0.7"
}
],
"type": "ECOSYSTEM"
}
]
},
{
"package": {
"ecosystem": "RubyGems",
"name": "sidekiq-unique-jobs"
},
"ranges": [
{
"events": [
{
"introduced": "6.0.0.rc7"
},
{
"fixed": "7.1.33"
}
],
"type": "ECOSYSTEM"
}
]
}
],
"aliases": [
"CVE-2024-25122"
],
"database_specific": {
"cwe_ids": [
"CWE-400",
"CWE-754",
"CWE-79",
"CWE-80"
],
"github_reviewed": true,
"github_reviewed_at": "2024-02-13T18:34:16Z",
"nvd_published_at": "2024-02-13T19:15:11Z",
"severity": "HIGH"
},
"details": "### Summary\n\nCross site scripting (XSS) potentially exposing cookies / sessions / localStorage, fixed by `sidekiq-unique-jobs` v8.0.7.\n\nSpecifically, this is a Reflected (Server-Side), Non-Self, Cross Site Scripting vulnerability, considered a **_P3_** on the BugCrowd [taxonomy](https://bugcrowd.com/vulnerability-rating-taxonomy) with the following categorization:\nCross-Site Scripting (XSS) \u003e Reflected \u003e Non-Self\n\nIt was initially thought there was a second vulnerability (RCE), but it was a false alarm. Injection is impossible with Redis:\n\n\u003e String escaping and NoSQL injection\n\u003e The Redis protocol has no concept of string escaping, so injection is impossible under normal circumstances using a normal client library. The protocol uses prefixed-length strings and is completely binary safe.\n\nRef: https://redis.io/docs/management/security/\n\n**XSS Vulnerability**\n\nSpecially crafted `GET` request parameters handled by any of the following endpoints of `sidekiq-unique-jobs`\u0027 \"admin\" web UI, allow a super-user attacker, or an unwitting, but authorized, victim, who has received a disguised / crafted link, to successfully execute malicious code, which could potentially steal cookies, session data, or local storage data from the app the `sidekiq-unique-jobs` web UI is mounted in.\n\n1. `/changelogs`\n2. `/locks`\n3. `/expiring_locks`\n\nThis means if your `sidekiq-unique-jobs` web UI is mounted at `/sidekiq`, the vulnerable paths are:\n\n1. `/sidekiq/changelogs`\n2. `/sidekiq/locks`\n3. `/sidekiq/expiring_locks`\n\nXSS vulnerability is an instance of [CAPEC-32: XSS Through HTTP Query Strings](https://capec.mitre.org/data/definitions/32.html), which is related to [CWE-80](https://cwe.mitre.org/data/definitions/80.html). In certain cases where it results in a server error with status 500, it could be considered a vector for uncontrolled resource consumption, given that errors can be much more resource intensive that normal requests, and thus [CWE-400](https://cwe.mitre.org/data/definitions/400.html) \u0026 [CWE-754](https://cwe.mitre.org/data/definitions/754.html) may also be relevant.\n\n### Details\n\nFix for the XSS vulnerability was released in `sidekiq-unique-jobs` [v8.0.7](https://github.com/mhenrixon/sidekiq-unique-jobs/releases/tag/v8.0.7).\n\nThis is an analogous attack vector to that which affected `sidekiq` gem from version v7.0.4 to v7.0.7, and was given identifiers [GHSA-h3r8-h5qw-4r35](https://github.com/advisories/GHSA-h3r8-h5qw-4r35) \u0026 [CVE-2023-1892](https://github.com/advisories/GHSA-h3r8-h5qw-4r35).\n\nThe vulnerability in `sidekiq-unique-jobs`\u0027 was *not* fixed by `sidekiq` [v7.0.8](https://github.com/sidekiq/sidekiq/blob/main/Changes.md#708), nor the more recent `sidekiq` [v7.2.0](https://github.com/sidekiq/sidekiq/blob/main/Changes.md#720) releases; they are similar but unrelated, distinct vulnerabilities in adjacent projects.\n\nNote #1: The admin web UI for `sidekiq-unique-jobs` is not protected by any authorization constraint in the default configuration. Auth constraints must be configured by the programmer. It is recommended and expected that users will configure authorization constrains on the \"admin\" UI. This is not specifically related to the vulnerability but may make users who fail to constrain their \"admin\" UI even more vulnerable.\n\nNote #2: Most users of the library will not have configured the UI on a sandboxed subdomain, making all their cookies, localStorage data and session secrets [vulnerable to exposure](https://liveoverflow.com/do-not-use-alert-1-in-xss/). The purpose of a sandboxed subdomain is expressly to prevent leaking sensitive data through XSS attacks.\n\nXSS Fix PR: https://github.com/mhenrixon/sidekiq-unique-jobs/pull/829\n\n### PoC\n\n**XSS**\n\nUse a string like:\n```\n%22%3E%3Cimg/src/onerror=alert(document.domain)%3E\n```\nas the value for one of the parameters that are handled without escaping.\nReference: https://liveoverflow.com/do-not-use-alert-1-in-xss/\n\n1. Visit [/sidekiq/changelogs](http://localhost:3000/sidekiq/changelogs) - with a crafted query string like one of the following:\n a. Screenshot: 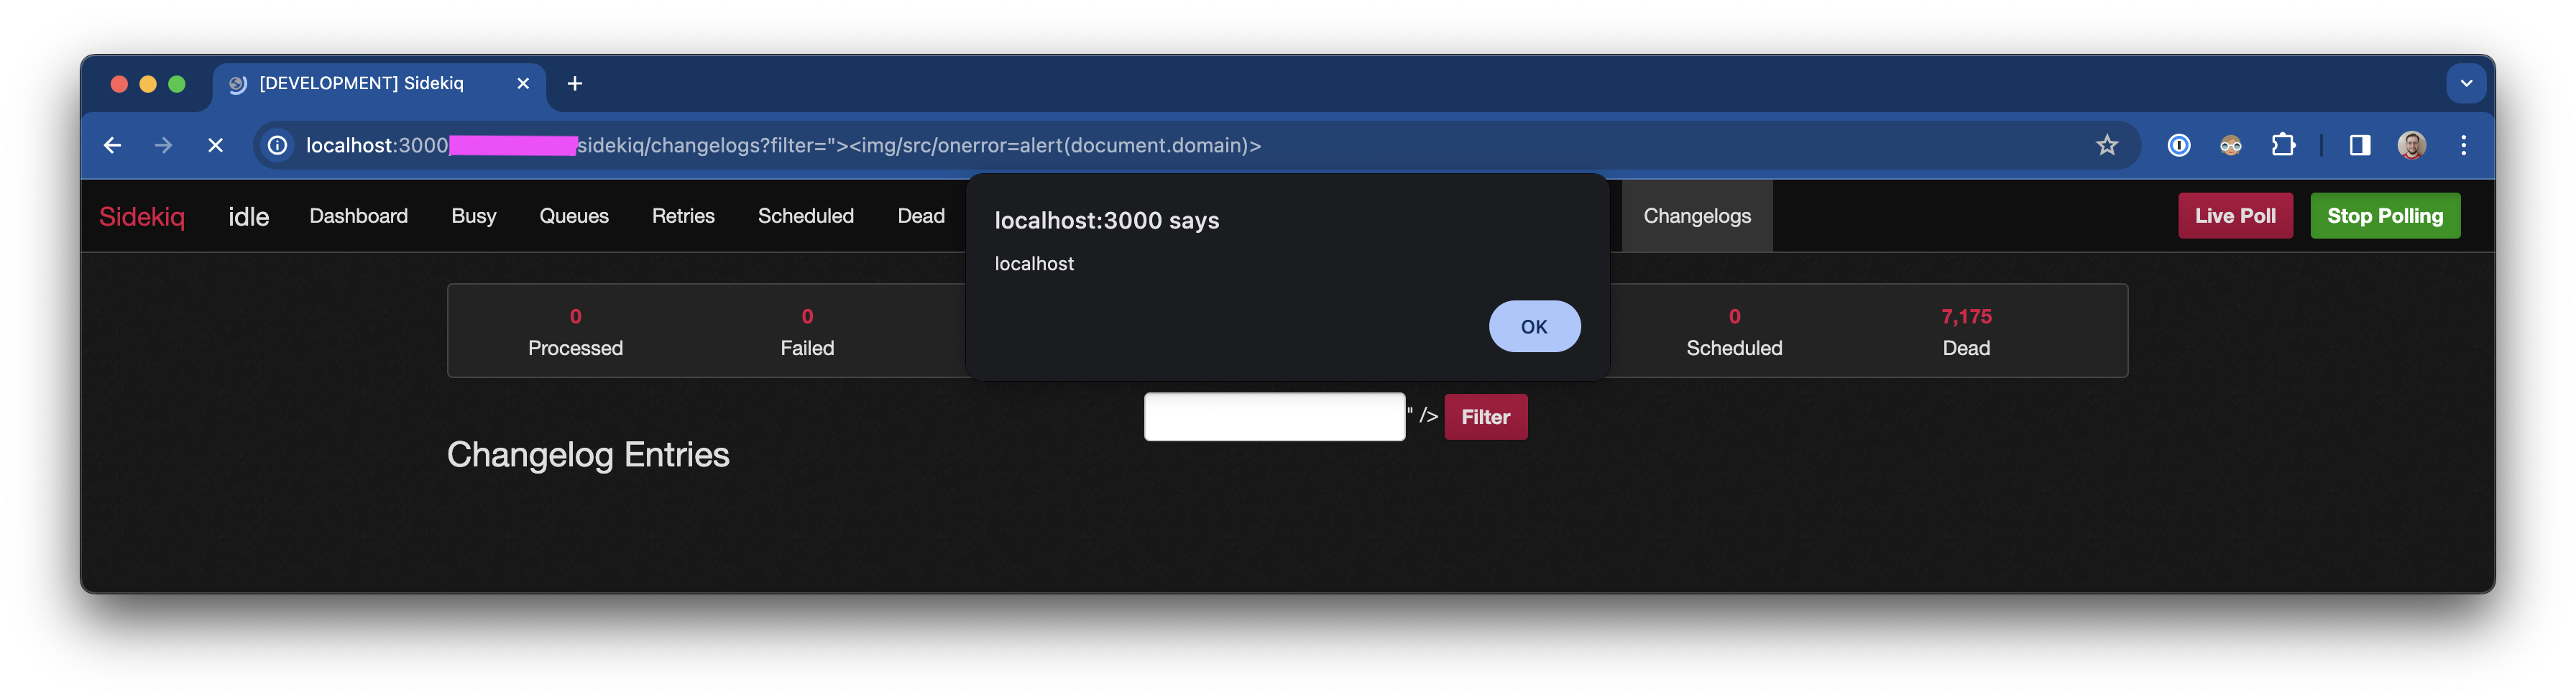\n b. `filter` is XSS vulnerable: `?filter=%22%3E%3Cimg/src/onerror=alert(document.domain)%3E`\n c. `count` is vulnerable to triggering an application error (status 500), potentially allowing resource exhaustion `?count=%22%3E%3Cimg/src/onerror=alert(document.domain)%3E`\n 1. Screenshot: 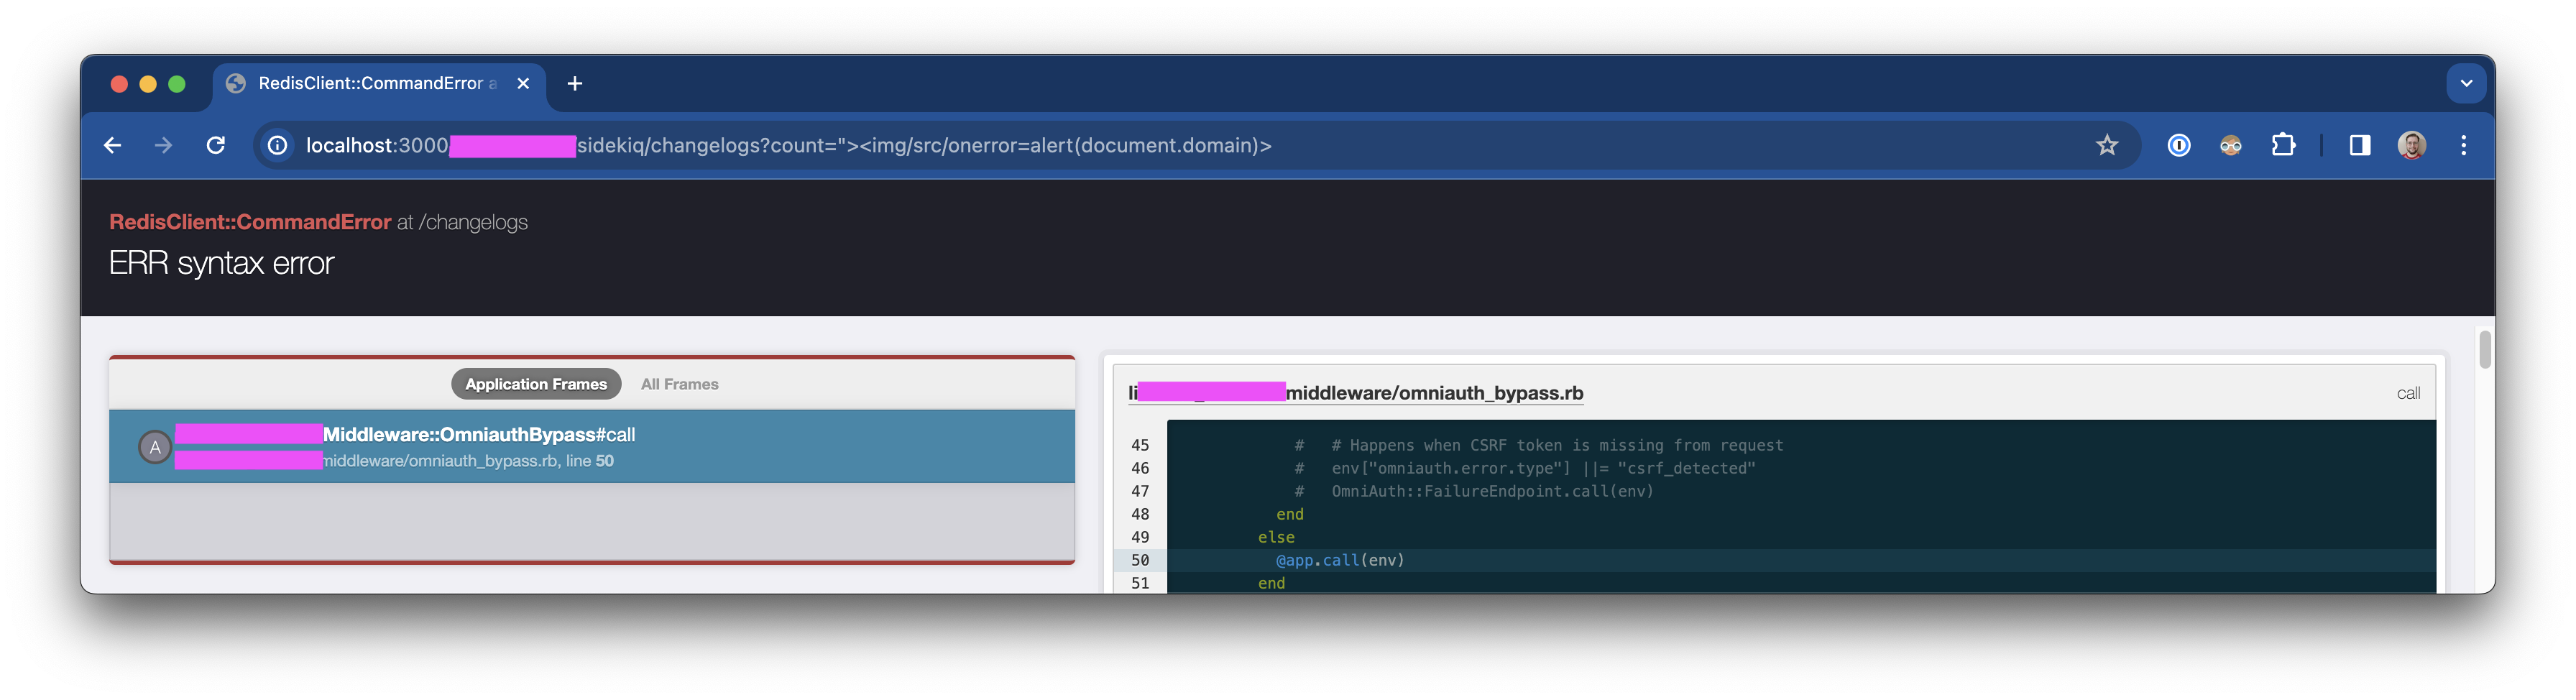\n2. Visit [/sidekiq/locks](http://localhost:3000/sidekiq/locks) - with a crafted query string like one of the following:\n a. Screenshot: 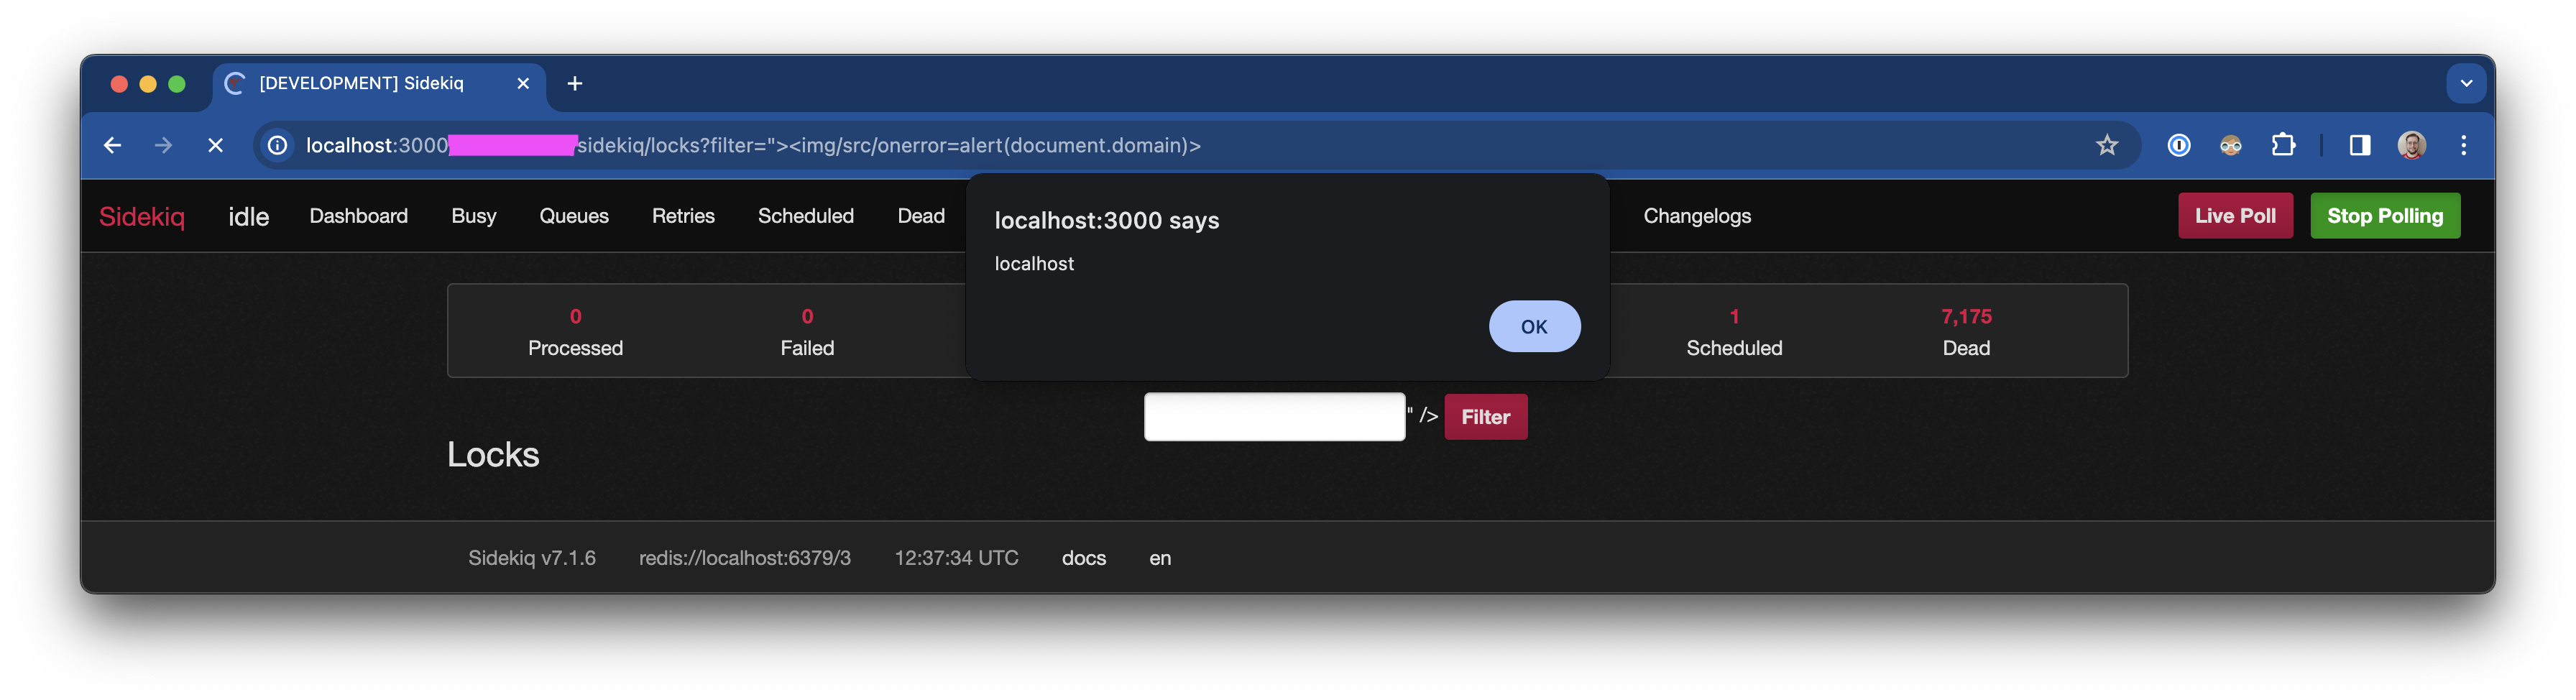\n b. `filter` is XSS vulnerable: `?filter=%22%3E%3Cimg/src/onerror=alert(document.domain)%3E`\n c. `count` is vulnerable to triggering an application error (status 500), potentially allowing resource exhaustion `?count=%22%3E%3Cimg/src/onerror=alert(document.domain)%3E`\n 1. Screenshot: 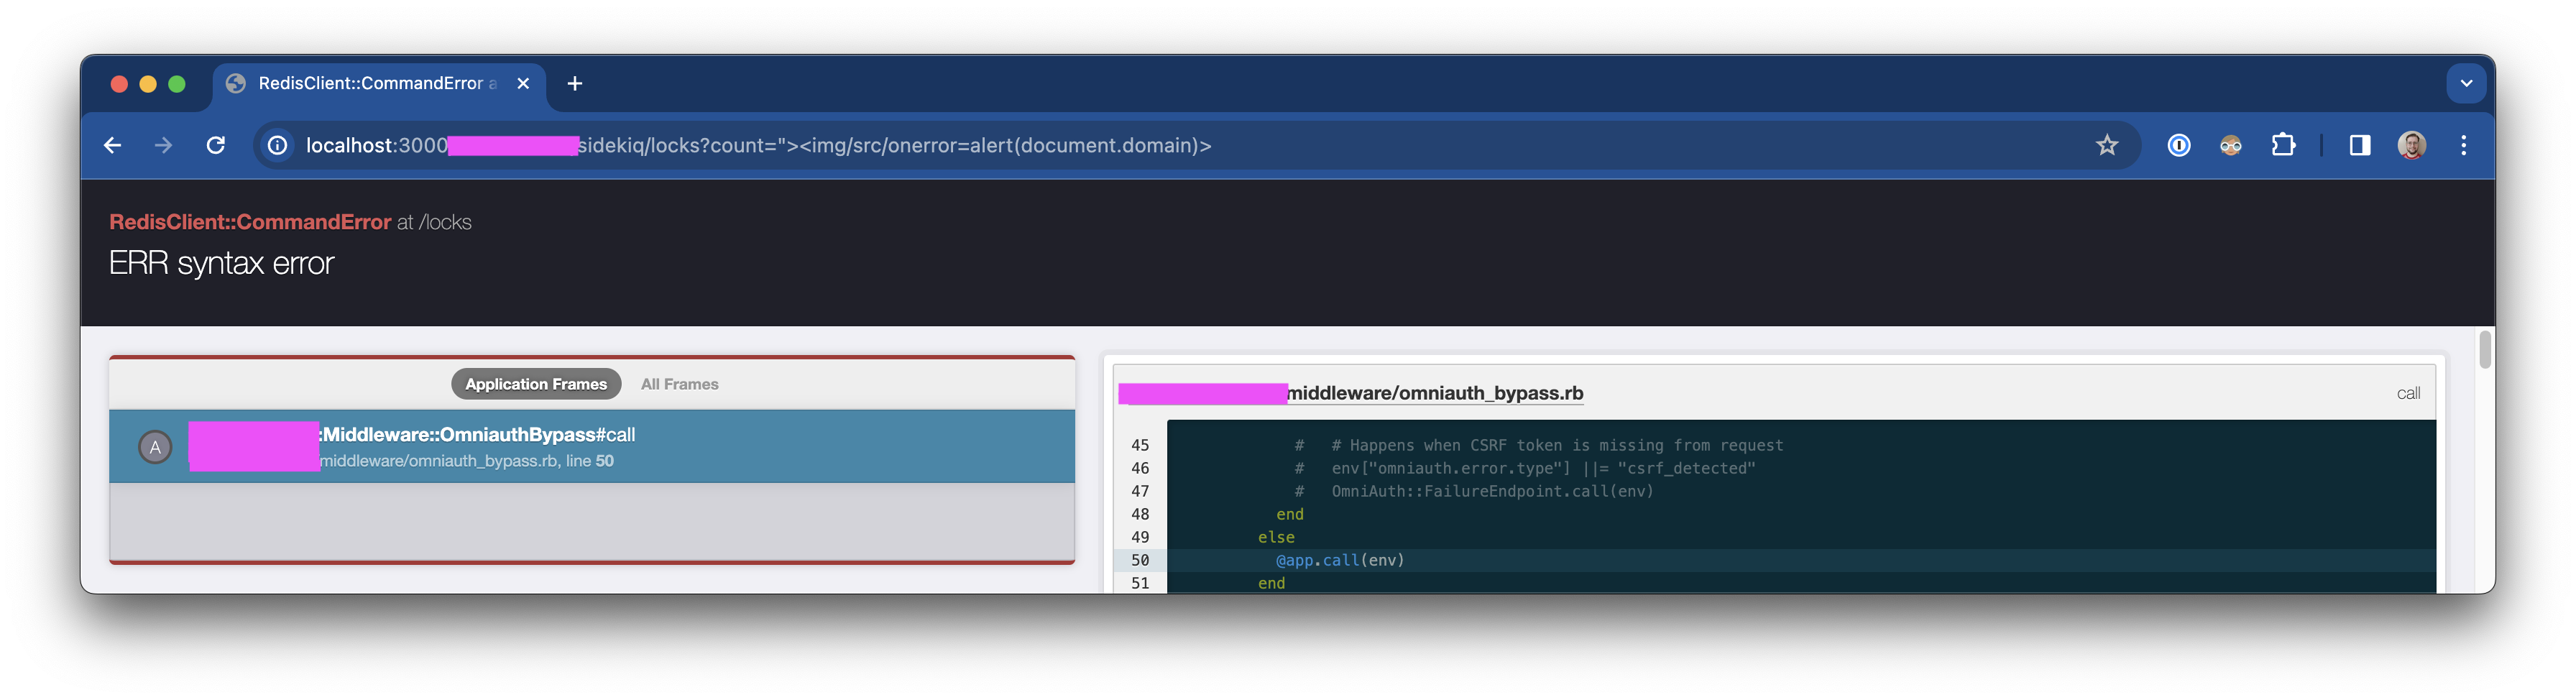\n3. Visit [/sidekiq/expiring_locks](http://localhost:3000/sidekiq/expiring_locks) - with a crafted query string like one of the following: \n a. Screenshot: 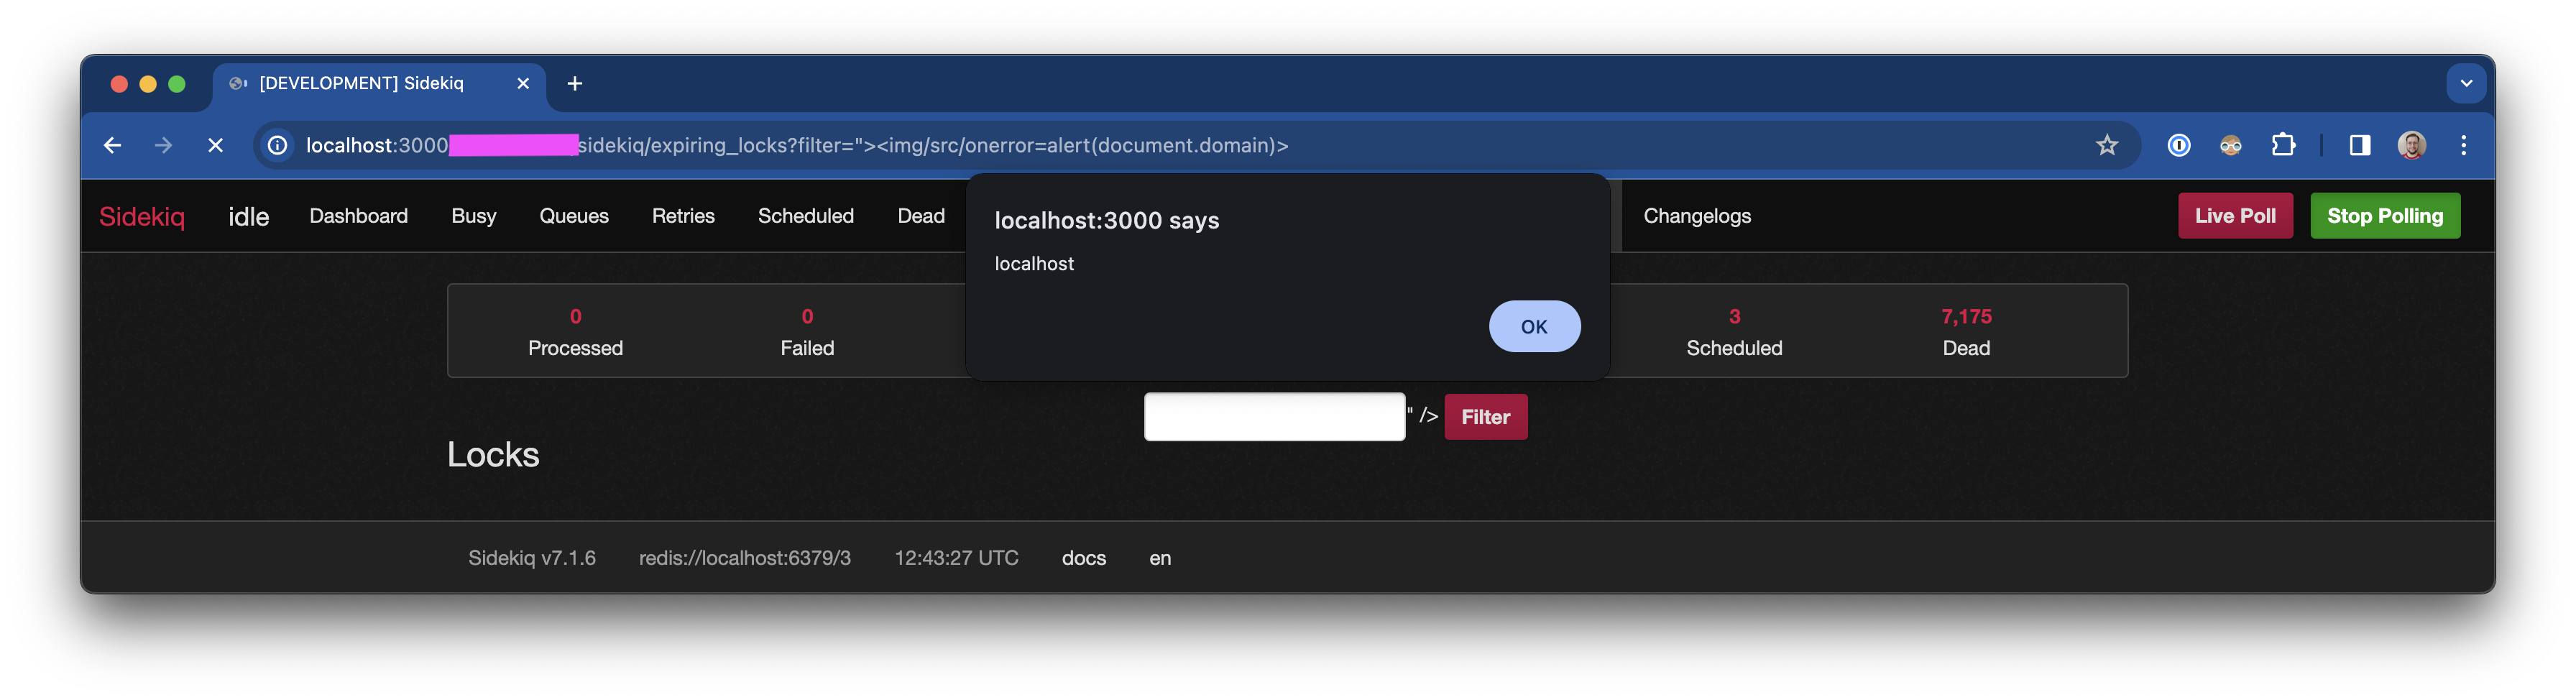\n b. `filter` is XSS vulnerable: `?filter=%22%3E%3Cimg/src/onerror=alert(document.domain)%3E`\n\n### Impact\n\nThis is a vulnerability of critical severity, which impacts many thousands of sites, since `sidekiq-unique-jobs` is widely deployed across the industry, with multiple attack vectors.",
"id": "GHSA-cmh9-rx85-xj38",
"modified": "2024-02-20T16:40:10Z",
"published": "2024-02-13T18:34:16Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/mhenrixon/sidekiq-unique-jobs/security/advisories/GHSA-cmh9-rx85-xj38"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-25122"
},
{
"type": "WEB",
"url": "https://github.com/mhenrixon/sidekiq-unique-jobs/commit/cd09ba6108f98973b6649a6149790c3d4502b4cc"
},
{
"type": "WEB",
"url": "https://github.com/mhenrixon/sidekiq-unique-jobs/commit/ec3afd920c1b55843c72f748a87baac7f8be82ed"
},
{
"type": "PACKAGE",
"url": "https://github.com/mhenrixon/sidekiq-unique-jobs"
},
{
"type": "WEB",
"url": "https://github.com/rubysec/ruby-advisory-db/blob/master/gems/sidekiq-unique-jobs/CVE-2024-25122.yml"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:L",
"type": "CVSS_V3"
}
],
"summary": "XSS sidekiq-unique-jobs UI server vulnerability"
}
GHSA-CP9M-FGRV-J66X
Vulnerability from github – Published: 2025-05-07 18:30 – Updated: 2025-07-11 15:31A vulnerability in the CLI of Cisco IOS XE Software could allow an authenticated, local attacker with privilege level 15 to elevate privileges to root on the underlying operating system of an affected device.
This vulnerability is due to insufficient input validation when processing specific configuration commands. An attacker could exploit this vulnerability by including crafted input in specific configuration commands. A successful exploit could allow the attacker to elevate privileges to root on the underlying operating system of an affected device. The security impact rating (SIR) of this advisory has been raised to High because an attacker could gain access to the underlying operating system of the affected device and perform potentially undetected actions.
Note: The attacker must have privileges to enter configuration mode on the affected device. This is usually referred to as privilege level 15.
{
  "affected": [],
  "aliases": [
    "CVE-2025-20200"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-754"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2025-05-07T18:15:40Z",
    "severity": "MODERATE"
  },
  "details": "A vulnerability\u00a0in the CLI of Cisco IOS XE Software could allow an authenticated, local attacker with privilege level 15 to elevate privileges to root on the underlying operating system of an affected device.\n\n This vulnerability is due to insufficient input validation when processing specific configuration commands. An attacker could exploit this vulnerability by including crafted input in specific configuration commands. A successful exploit could allow the attacker to elevate privileges to root on the underlying operating system of an affected device. The security impact rating (SIR) of this advisory has been raised to High because an attacker could gain access to the underlying operating system of the affected device and perform potentially undetected actions.\n\n Note: The attacker must have privileges to enter configuration mode on the affected device. This is usually referred to as privilege level 15.",
  "id": "GHSA-cp9m-fgrv-j66x",
  "modified": "2025-07-11T15:31:31Z",
  "published": "2025-05-07T18:30:49Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2025-20200"
    },
    {
      "type": "WEB",
      "url": "https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-iosxe-privesc-su7scvdp"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:L/AC:L/PR:H/UI:N/S:C/C:L/I:H/A:N",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-CPFH-Q3V8-WJ73
Vulnerability from github – Published: 2026-02-11 18:31 – Updated: 2026-02-11 18:31A denial-of-service (DoS) vulnerability in the Advanced DNS Security (ADNS) feature of Palo Alto Networks PAN-OS® software enables an unauthenticated attacker to initiate system reboots using a maliciously crafted packet. Repeated attempts to initiate a reboot causes the firewall to enter maintenance mode.
Cloud NGFW and Prisma Access® are not impacted by this vulnerability.
{
  "affected": [],
  "aliases": [
    "CVE-2026-0229"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-754"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-02-11T18:16:07Z",
    "severity": "MODERATE"
  },
  "details": "A denial-of-service (DoS) vulnerability in the Advanced DNS Security (ADNS) feature of Palo Alto Networks PAN-OS\u00ae software enables an unauthenticated attacker to initiate system reboots using a maliciously crafted packet. Repeated attempts to initiate a reboot causes the firewall to enter maintenance mode.\n\nCloud NGFW and Prisma Access\u00ae are not impacted by this vulnerability.",
  "id": "GHSA-cpfh-q3v8-wj73",
  "modified": "2026-02-11T18:31:31Z",
  "published": "2026-02-11T18:31:31Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-0229"
    },
    {
      "type": "WEB",
      "url": "https://security.paloaltonetworks.com/CVE-2026-0229"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:N/VI:N/VA:H/SC:N/SI:N/SA:N/E:U/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:Y/R:U/V:D/RE:M/U:Amber",
      "type": "CVSS_V4"
    }
  ]
}
GHSA-CQ54-MJWX-5PJW
Vulnerability from github – Published: 2022-05-24 22:01 – Updated: 2022-05-24 22:01Sylabs Singularity 3.5.x and 3.6.x, and SingularityPRO before 3.5-8, has an Incorrect Check of a Function's Return Value.
{
  "affected": [],
  "aliases": [
    "CVE-2021-33622"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-754"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2021-06-15T20:15:00Z",
    "severity": "CRITICAL"
  },
  "details": "Sylabs Singularity 3.5.x and 3.6.x, and SingularityPRO before 3.5-8, has an Incorrect Check of a Function\u0027s Return Value.",
  "id": "GHSA-cq54-mjwx-5pjw",
  "modified": "2022-05-24T22:01:39Z",
  "published": "2022-05-24T22:01:39Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2021-33622"
    },
    {
      "type": "WEB",
      "url": "https://medium.com/sylabs"
    },
    {
      "type": "WEB",
      "url": "https://support.sylabs.io/support/solutions/articles/42000087130-3-5-8-security-release-cve-2021-33622-"
    }
  ],
  "schema_version": "1.4.0",
  "severity": []
}
GHSA-CQMJ-92XF-R6R9
Vulnerability from github – Published: 2023-05-23 19:55 – Updated: 2024-11-18 16:26Impact
A specially crafted Socket.IO packet can trigger an uncaught exception on the Socket.IO server, thus killing the Node.js process.
TypeError: Cannot convert object to primitive value
       at Socket.emit (node:events:507:25)
       at .../node_modules/socket.io/lib/socket.js:531:14
Patches
A fix has been released today (2023/05/22):
- https://github.com/socketio/socket.io-parser/commit/3b78117bf6ba7e99d7a5cfc1ba54d0477554a7f3, included in
socket.io-parser@4.2.3 - https://github.com/socketio/socket.io-parser/commit/2dc3c92622dad113b8676be06f23b1ed46b02ced, included in
socket.io-parser@3.4.3
Another fix has been released for the 3.3.x branch:
- https://github.com/socketio/socket.io-parser/commit/ee006607495eca4ec7262ad080dd3a91439a5ba4, included in `socket.io-parser@3.3.4
socket.io version |
socket.io-parser version |
Needs minor update? |
|---|---|---|
4.5.2...latest |
~4.2.0 (ref) |
npm audit fix should be sufficient |
4.1.3...4.5.1 |
~4.1.1 (ref) |
Please upgrade to socket.io@4.6.x |
3.0.5...4.1.2 |
~4.0.3 (ref) |
Please upgrade to socket.io@4.6.x |
3.0.0...3.0.4 |
~4.0.1 (ref) |
Please upgrade to socket.io@4.6.x |
2.3.0...2.5.0 |
~3.4.0 (ref) |
npm audit fix should be sufficient |
Workarounds
There is no known workaround except upgrading to a safe version.
For more information
If you have any questions or comments about this advisory:
- Open a discussion here
Thanks to @rafax00 for the responsible disclosure.
{
  "affected": [
    {
      "package": {
        "ecosystem": "npm",
        "name": "socket.io-parser"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "4.0.4"
            },
            {
              "fixed": "4.2.3"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    },
    {
      "package": {
        "ecosystem": "npm",
        "name": "socket.io-parser"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "3.4.0"
            },
            {
              "fixed": "3.4.3"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    },
    {
      "package": {
        "ecosystem": "npm",
        "name": "socket.io-parser"
      },
      "ranges": [
        {
          "events": [
            {
              "introduced": "0"
            },
            {
              "fixed": "3.3.4"
            }
          ],
          "type": "ECOSYSTEM"
        }
      ]
    }
  ],
  "aliases": [
    "CVE-2023-32695"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-20",
      "CWE-754"
    ],
    "github_reviewed": true,
    "github_reviewed_at": "2023-05-23T19:55:13Z",
    "nvd_published_at": "2023-05-27T16:15:09Z",
    "severity": "MODERATE"
  },
  "details": "### Impact\n\nA specially crafted Socket.IO packet can trigger an uncaught exception on the Socket.IO server, thus killing the Node.js process.\n\n```\nTypeError: Cannot convert object to primitive value\n       at Socket.emit (node:events:507:25)\n       at .../node_modules/socket.io/lib/socket.js:531:14\n```\n\n### Patches\n\nA fix has been released today (2023/05/22):\n\n- https://github.com/socketio/socket.io-parser/commit/3b78117bf6ba7e99d7a5cfc1ba54d0477554a7f3, included in `socket.io-parser@4.2.3`\n- https://github.com/socketio/socket.io-parser/commit/2dc3c92622dad113b8676be06f23b1ed46b02ced, included in `socket.io-parser@3.4.3`\n\n\nAnother fix has been released for the `3.3.x` branch:\n\n- https://github.com/socketio/socket.io-parser/commit/ee006607495eca4ec7262ad080dd3a91439a5ba4, included in `socket.io-parser@3.3.4\n\n| `socket.io` version | `socket.io-parser` version                                                                              | Needs minor update?                  |\n|---------------------|---------------------------------------------------------------------------------------------------------|--------------------------------------|\n| `4.5.2...latest`    | `~4.2.0` ([ref](https://github.com/socketio/socket.io/commit/9890b036cf942f6b6ad2afeb6a8361c32cd5d528)) | `npm audit fix` should be sufficient |\n| `4.1.3...4.5.1`     | `~4.1.1` ([ref](https://github.com/socketio/socket.io/commit/7c44893d7878cd5bba1eff43150c3e664f88fb57)) | Please upgrade to `socket.io@4.6.x`  |\n| `3.0.5...4.1.2`     | `~4.0.3` ([ref](https://github.com/socketio/socket.io/commit/752dfe3b1e5fecda53dae899b4a39e6fed5a1a17)) | Please upgrade to `socket.io@4.6.x`  |\n| `3.0.0...3.0.4`     | `~4.0.1` ([ref](https://github.com/socketio/socket.io/commit/1af3267e3f5f7884214cf2ca4d5282d620092fb0)) | Please upgrade to `socket.io@4.6.x`  |\n| `2.3.0...2.5.0`     | `~3.4.0` ([ref](https://github.com/socketio/socket.io/commit/cf39362014f5ff13a17168b74772c43920d6e4fd)) | `npm audit fix` should be sufficient |\n\n\n### Workarounds\n\nThere is no known workaround except upgrading to a safe version.\n\n### For more information\n\nIf you have any questions or comments about this advisory:\n\n- Open a discussion [here](https://github.com/socketio/socket.io/discussions)\n\nThanks to [@rafax00](https://github.com/rafax00) for the responsible disclosure.\n",
  "id": "GHSA-cqmj-92xf-r6r9",
  "modified": "2024-11-18T16:26:29Z",
  "published": "2023-05-23T19:55:13Z",
  "references": [
    {
      "type": "WEB",
      "url": "https://github.com/socketio/socket.io-parser/security/advisories/GHSA-cqmj-92xf-r6r9"
    },
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2023-32695"
    },
    {
      "type": "WEB",
      "url": "https://github.com/socketio/socket.io-parser/commit/1c220ddbf45ea4b44bc8dbf6f9ae245f672ba1b9"
    },
    {
      "type": "WEB",
      "url": "https://github.com/socketio/socket.io-parser/commit/2dc3c92622dad113b8676be06f23b1ed46b02ced"
    },
    {
      "type": "WEB",
      "url": "https://github.com/socketio/socket.io-parser/commit/3b78117bf6ba7e99d7a5cfc1ba54d0477554a7f3"
    },
    {
      "type": "WEB",
      "url": "https://github.com/socketio/socket.io-parser/commit/ee006607495eca4ec7262ad080dd3a91439a5ba4"
    },
    {
      "type": "PACKAGE",
      "url": "https://github.com/socketio/socket.io-parser"
    },
    {
      "type": "WEB",
      "url": "https://github.com/socketio/socket.io-parser/releases/tag/4.2.3"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:L",
      "type": "CVSS_V3"
    },
    {
      "score": "CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:L/VA:L/SC:N/SI:N/SA:N",
      "type": "CVSS_V4"
    }
  ],
  "summary": "Insufficient validation when decoding a Socket.IO packet"
}
GHSA-CR5G-9FRG-Q8M8
Vulnerability from github – Published: 2026-03-24 15:30 – Updated: 2026-03-24 21:31Incorrect boundary conditions in the Audio/Video component. This vulnerability affects Firefox < 149 and Firefox ESR < 140.9.
{
  "affected": [],
  "aliases": [
    "CVE-2026-4714"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-754"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-03-24T13:16:07Z",
    "severity": "HIGH"
  },
  "details": "Incorrect boundary conditions in the Audio/Video component. This vulnerability affects Firefox \u003c 149 and Firefox ESR \u003c 140.9.",
  "id": "GHSA-cr5g-9frg-q8m8",
  "modified": "2026-03-24T21:31:22Z",
  "published": "2026-03-24T15:30:28Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-4714"
    },
    {
      "type": "WEB",
      "url": "https://bugzilla.mozilla.org/show_bug.cgi?id=2018126"
    },
    {
      "type": "WEB",
      "url": "https://www.mozilla.org/security/advisories/mfsa2026-20"
    },
    {
      "type": "WEB",
      "url": "https://www.mozilla.org/security/advisories/mfsa2026-22"
    },
    {
      "type": "WEB",
      "url": "https://www.mozilla.org/security/advisories/mfsa2026-23"
    },
    {
      "type": "WEB",
      "url": "https://www.mozilla.org/security/advisories/mfsa2026-24"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-CR76-625X-Q34W
Vulnerability from github – Published: 2024-07-11 18:31 – Updated: 2024-09-23 15:30An Improper Check for Unusual or Exceptional Conditions vulnerability in the Packet Forwarding Engine (PFE) of Juniper Networks Junos OS Evolved on ACX7000 Series allows an unauthenticated, adjacent attacker to cause a
Denial-of-Service (DoS).
On all ACX 7000 Series platforms running
Junos OS Evolved, and configured with IRBs, if a Customer Edge device (CE) device is dual homed to two Provider Edge devices (PE) a traffic loop will occur when the CE sends multicast packets. This issue can be triggered by IPv4 and IPv6 traffic.
This issue affects Junos OS Evolved:
All versions from 22.2R1-EVO and later versions before 22.4R2-EVO,
This issue does not affect Junos OS Evolved versions before 22.1R1-EVO.
{
  "affected": [],
  "aliases": [
    "CVE-2024-39519"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-754"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2024-07-11T16:15:02Z",
    "severity": "HIGH"
  },
  "details": "An Improper Check for Unusual or Exceptional Conditions vulnerability in the Packet Forwarding Engine (PFE) of Juniper Networks Junos OS Evolved on ACX7000 Series allows an unauthenticated, adjacent attacker to cause a \n\nDenial-of-Service (DoS).\n\nOn all ACX 7000 Series platforms running \n\nJunos OS Evolved, and configured with IRBs, if a Customer Edge device (CE) device is dual homed to two Provider Edge devices (PE) a traffic loop will occur when the CE sends multicast packets. This issue can be triggered by IPv4 and IPv6 traffic.\n\n\nThis issue affects Junos OS Evolved:\u00a0\n\nAll versions from 22.2R1-EVO and later versions before 22.4R2-EVO,\n\nThis issue does not affect Junos OS Evolved versions before 22.1R1-EVO.",
  "id": "GHSA-cr76-625x-q34w",
  "modified": "2024-09-23T15:30:59Z",
  "published": "2024-07-11T18:31:12Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2024-39519"
    },
    {
      "type": "WEB",
      "url": "https://supportportal.juniper.net/JSA82983"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:A/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H",
      "type": "CVSS_V3"
    },
    {
      "score": "CVSS:4.0/AV:A/AC:L/AT:N/PR:N/UI:N/VC:N/VI:N/VA:H/SC:N/SI:N/SA:L/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X",
      "type": "CVSS_V4"
    }
  ]
}
GHSA-CV5V-QFPJ-5PM3
Vulnerability from github – Published: 2022-05-24 19:05 – Updated: 2022-05-24 19:05An improper check for unusual or exceptional conditions issue exists within the parsing DGN files from Drawings SDK (Version 2022.4 and prior) resulting from the lack of proper validation of the user-supplied data. This may result in several of out-of-bounds problems and allow attackers to cause a denial-of-service condition or execute code in the context of the current process.
{
  "affected": [],
  "aliases": [
    "CVE-2021-32946"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-754"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2021-06-17T12:15:00Z",
    "severity": "HIGH"
  },
  "details": "An improper check for unusual or exceptional conditions issue exists within the parsing DGN files from Drawings SDK (Version 2022.4 and prior) resulting from the lack of proper validation of the user-supplied data. This may result in several of out-of-bounds problems and allow attackers to cause a denial-of-service condition or execute code in the context of the current process.",
  "id": "GHSA-cv5v-qfpj-5pm3",
  "modified": "2022-05-24T19:05:36Z",
  "published": "2022-05-24T19:05:36Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2021-32946"
    },
    {
      "type": "WEB",
      "url": "https://cert-portal.siemens.com/productcert/pdf/ssa-155599.pdf"
    },
    {
      "type": "WEB",
      "url": "https://cert-portal.siemens.com/productcert/pdf/ssa-938030.pdf"
    },
    {
      "type": "WEB",
      "url": "https://us-cert.cisa.gov/ics/advisories/icsa-21-159-02"
    },
    {
      "type": "WEB",
      "url": "https://www.zerodayinitiative.com/advisories/ZDI-21-983"
    },
    {
      "type": "WEB",
      "url": "https://www.zerodayinitiative.com/advisories/ZDI-21-985"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:L/AC:L/PR:N/UI:R/S:U/C:H/I:H/A:H",
      "type": "CVSS_V3"
    }
  ]
}
GHSA-CV9F-44GV-7RG6
Vulnerability from github – Published: 2026-07-09 21:31 – Updated: 2026-07-09 21:31An Improper Check for Unusual or Exceptional Conditions vulnerability in the routing protocol daemon (RPD) of Juniper Networks Junos OS and Junos OS Evolved allows an adjacent, unauthenticated attacker sending a specific BGP update over an established BGP session to cause a Denial-of-Service (DoS).
Upon receipt of a specifically malformed non-inet/inet6 unicast BGP update, an RPD crash and restart is triggered, which will cause a complete service outage until routing has reconverged. The rpd crash occurs before the update can be readvertised, so there is no downstream propagation.
This issue affects:
-
Junos OS versions 25.2 before 25.2R2;
-
Junos OS Evolved versions 25.2 before 25.2R2-EVO.
This issue doesn't affect Junos OS versions before 25.2R1 nor Junos OS Evolved versions before 25.2R1-EVO.
{
  "affected": [],
  "aliases": [
    "CVE-2026-33801"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-754"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2026-07-09T21:16:55Z",
    "severity": "HIGH"
  },
  "details": "An Improper Check for Unusual or Exceptional Conditions vulnerability in the routing protocol daemon (RPD) of Juniper Networks Junos OS and Junos OS Evolved allows an adjacent, unauthenticated attacker sending a specific BGP update over an established BGP session to cause a Denial-of-Service (DoS).\n\nUpon receipt of a specifically malformed non-inet/inet6 unicast BGP update, an RPD crash and restart is triggered, which will cause a complete service outage until routing has reconverged. The rpd crash occurs before the update can be readvertised, so there is no downstream propagation.\n\n\nThis issue affects:\n\n\n\n  *  Junos OS versions 25.2 before 25.2R2;\n\n\n  *  Junos OS Evolved versions 25.2 before 25.2R2-EVO.\n\n\n\n\nThis issue doesn\u0027t affect Junos OS versions before 25.2R1 nor Junos OS Evolved versions before 25.2R1-EVO.",
  "id": "GHSA-cv9f-44gv-7rg6",
  "modified": "2026-07-09T21:31:21Z",
  "published": "2026-07-09T21:31:21Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2026-33801"
    },
    {
      "type": "WEB",
      "url": "https://supportportal.juniper.net/JSA110076"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.1/AV:A/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H",
      "type": "CVSS_V3"
    },
    {
      "score": "CVSS:4.0/AV:A/AC:L/AT:N/PR:N/UI:N/VC:N/VI:N/VA:H/SC:N/SI:N/SA:L/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:Y/R:A/V:X/RE:M/U:X",
      "type": "CVSS_V4"
    }
  ]
}
GHSA-CV9P-C62C-7F95
Vulnerability from github – Published: 2022-05-17 02:35 – Updated: 2022-05-17 02:35Improper checks for unusual or exceptional conditions in Brocade NetIron 05.8.00 and later releases up to and including 06.1.00, when the Management Module is continuously scanned on port 22, may allow attackers to cause a denial of service (crash and reload) of the management module.
{
  "affected": [],
  "aliases": [
    "CVE-2016-8209"
  ],
  "database_specific": {
    "cwe_ids": [
      "CWE-754"
    ],
    "github_reviewed": false,
    "github_reviewed_at": null,
    "nvd_published_at": "2017-05-08T18:29:00Z",
    "severity": "HIGH"
  },
  "details": "Improper checks for unusual or exceptional conditions in Brocade NetIron 05.8.00 and later releases up to and including 06.1.00, when the Management Module is continuously scanned on port 22, may allow attackers to cause a denial of service (crash and reload) of the management module.",
  "id": "GHSA-cv9p-c62c-7f95",
  "modified": "2022-05-17T02:35:15Z",
  "published": "2022-05-17T02:35:15Z",
  "references": [
    {
      "type": "ADVISORY",
      "url": "https://nvd.nist.gov/vuln/detail/CVE-2016-8209"
    },
    {
      "type": "WEB",
      "url": "https://www.brocade.com/content/dam/common/documents/content-types/security-bulletin/brocade-security-advisory-2017-315.htm"
    },
    {
      "type": "WEB",
      "url": "http://www.securitytracker.com/id/1038402"
    }
  ],
  "schema_version": "1.4.0",
  "severity": [
    {
      "score": "CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H",
      "type": "CVSS_V3"
    }
  ]
}
Mitigation MIT-3
Strategy: Language Selection
- Use a language that does not allow this weakness to occur or provides constructs that make this weakness easier to avoid.
- Choose languages with features such as exception handling that force the programmer to anticipate unusual conditions that may generate exceptions. Custom exceptions may need to be developed to handle unusual business-logic conditions. Be careful not to pass sensitive exceptions back to the user (CWE-209, CWE-248).
Mitigation
Check the results of all functions that return a value and verify that the value is expected.
Mitigation
If using exception handling, catch and throw specific exceptions instead of overly-general exceptions (CWE-396, CWE-397). Catch and handle exceptions as locally as possible so that exceptions do not propagate too far up the call stack (CWE-705). Avoid unchecked or uncaught exceptions where feasible (CWE-248).
Mitigation MIT-39
- Ensure that error messages only contain minimal details that are useful to the intended audience and no one else. The messages need to strike the balance between being too cryptic (which can confuse users) or being too detailed (which may reveal more than intended). The messages should not reveal the methods that were used to determine the error. Attackers can use detailed information to refine or optimize their original attack, thereby increasing their chances of success.
- If errors must be captured in some detail, record them in log messages, but consider what could occur if the log messages can be viewed by attackers. Highly sensitive information such as passwords should never be saved to log files.
- Avoid inconsistent messaging that might accidentally tip off an attacker about internal state, such as whether a user account exists or not.
- Exposing additional information to a potential attacker in the context of an exceptional condition can help the attacker determine what attack vectors are most likely to succeed beyond DoS.
Mitigation MIT-5
Strategy: Input Validation
- Assume all input is malicious. Use an "accept known good" input validation strategy, i.e., use a list of acceptable inputs that strictly conform to specifications. Reject any input that does not strictly conform to specifications, or transform it into something that does.
- When performing input validation, consider all potentially relevant properties, including length, type of input, the full range of acceptable values, missing or extra inputs, syntax, consistency across related fields, and conformance to business rules. As an example of business rule logic, "boat" may be syntactically valid because it only contains alphanumeric characters, but it is not valid if the input is only expected to contain colors such as "red" or "blue."
- Do not rely exclusively on looking for malicious or malformed inputs. This is likely to miss at least one undesirable input, especially if the code's environment changes. This can give attackers enough room to bypass the intended validation. However, denylists can be useful for detecting potential attacks or determining which inputs are so malformed that they should be rejected outright.
Mitigation MIT-38
If the program must fail, ensure that it fails gracefully (fails closed). There may be a temptation to simply let the program fail poorly in cases such as low memory conditions, but an attacker may be able to assert control before the software has fully exited. Alternately, an uncontrolled failure could cause cascading problems with other downstream components; for example, the program could send a signal to a downstream process so the process immediately knows that a problem has occurred and has a better chance of recovery.
Mitigation
Use system limits, which should help to prevent resource exhaustion. However, the product should still handle low resource conditions since they may still occur.
No CAPEC attack patterns related to this CWE.