GHSA-PWGC-W4X9-GW67
Vulnerability from github – Published: 2024-05-03 17:53 – Updated: 2024-05-03 17:53Summary
Input in parameter notification_urls is not processed resulting in javascript execution in the application
Details
changedetection.io version: v0.45.21
https://github.com/dgtlmoon/changedetection.io/blob/0.45.21/changedetectionio/forms.py#L226
        for server_url in field.data:
            if not apobj.add(server_url):
                message = field.gettext('\'%s\' is not a valid AppRise URL.' % (server_url))
                raise ValidationError(message)
PoC
Setting > ADD Notification URL List
"><img src=x onerror=alert(document.domain)>
Requests
Impact
A reflected XSS vulnerability happens when the user input from a URL or POST data is reflected on the page without being stored, thus allowing the attacker to inject malicious content
{
"affected": [
{
"package": {
"ecosystem": "PyPI",
"name": "changedetection.io"
},
"ranges": [
{
"events": [
{
"introduced": "0"
},
{
"fixed": "0.45.22"
}
],
"type": "ECOSYSTEM"
}
]
}
],
"aliases": [
"CVE-2024-34061"
],
"database_specific": {
"cwe_ids": [
"CWE-79"
],
"github_reviewed": true,
"github_reviewed_at": "2024-05-03T17:53:22Z",
"nvd_published_at": "2024-05-02T14:15:10Z",
"severity": "MODERATE"
},
"details": "### Summary\n\nInput in parameter notification_urls is not processed resulting in javascript execution in the application\n\n### Details\nchangedetection.io version: v0.45.21\n\nhttps://github.com/dgtlmoon/changedetection.io/blob/0.45.21/changedetectionio/forms.py#L226\n\n```\n for server_url in field.data:\n if not apobj.add(server_url):\n message = field.gettext(\u0027\\\u0027%s\\\u0027 is not a valid AppRise URL.\u0027 % (server_url))\n raise ValidationError(message)\n```\n\n### PoC\n\nSetting \u003e ADD Notification URL List\n\n\n\n\n```\n\"\u003e\u003cimg src=x onerror=alert(document.domain)\u003e\n```\n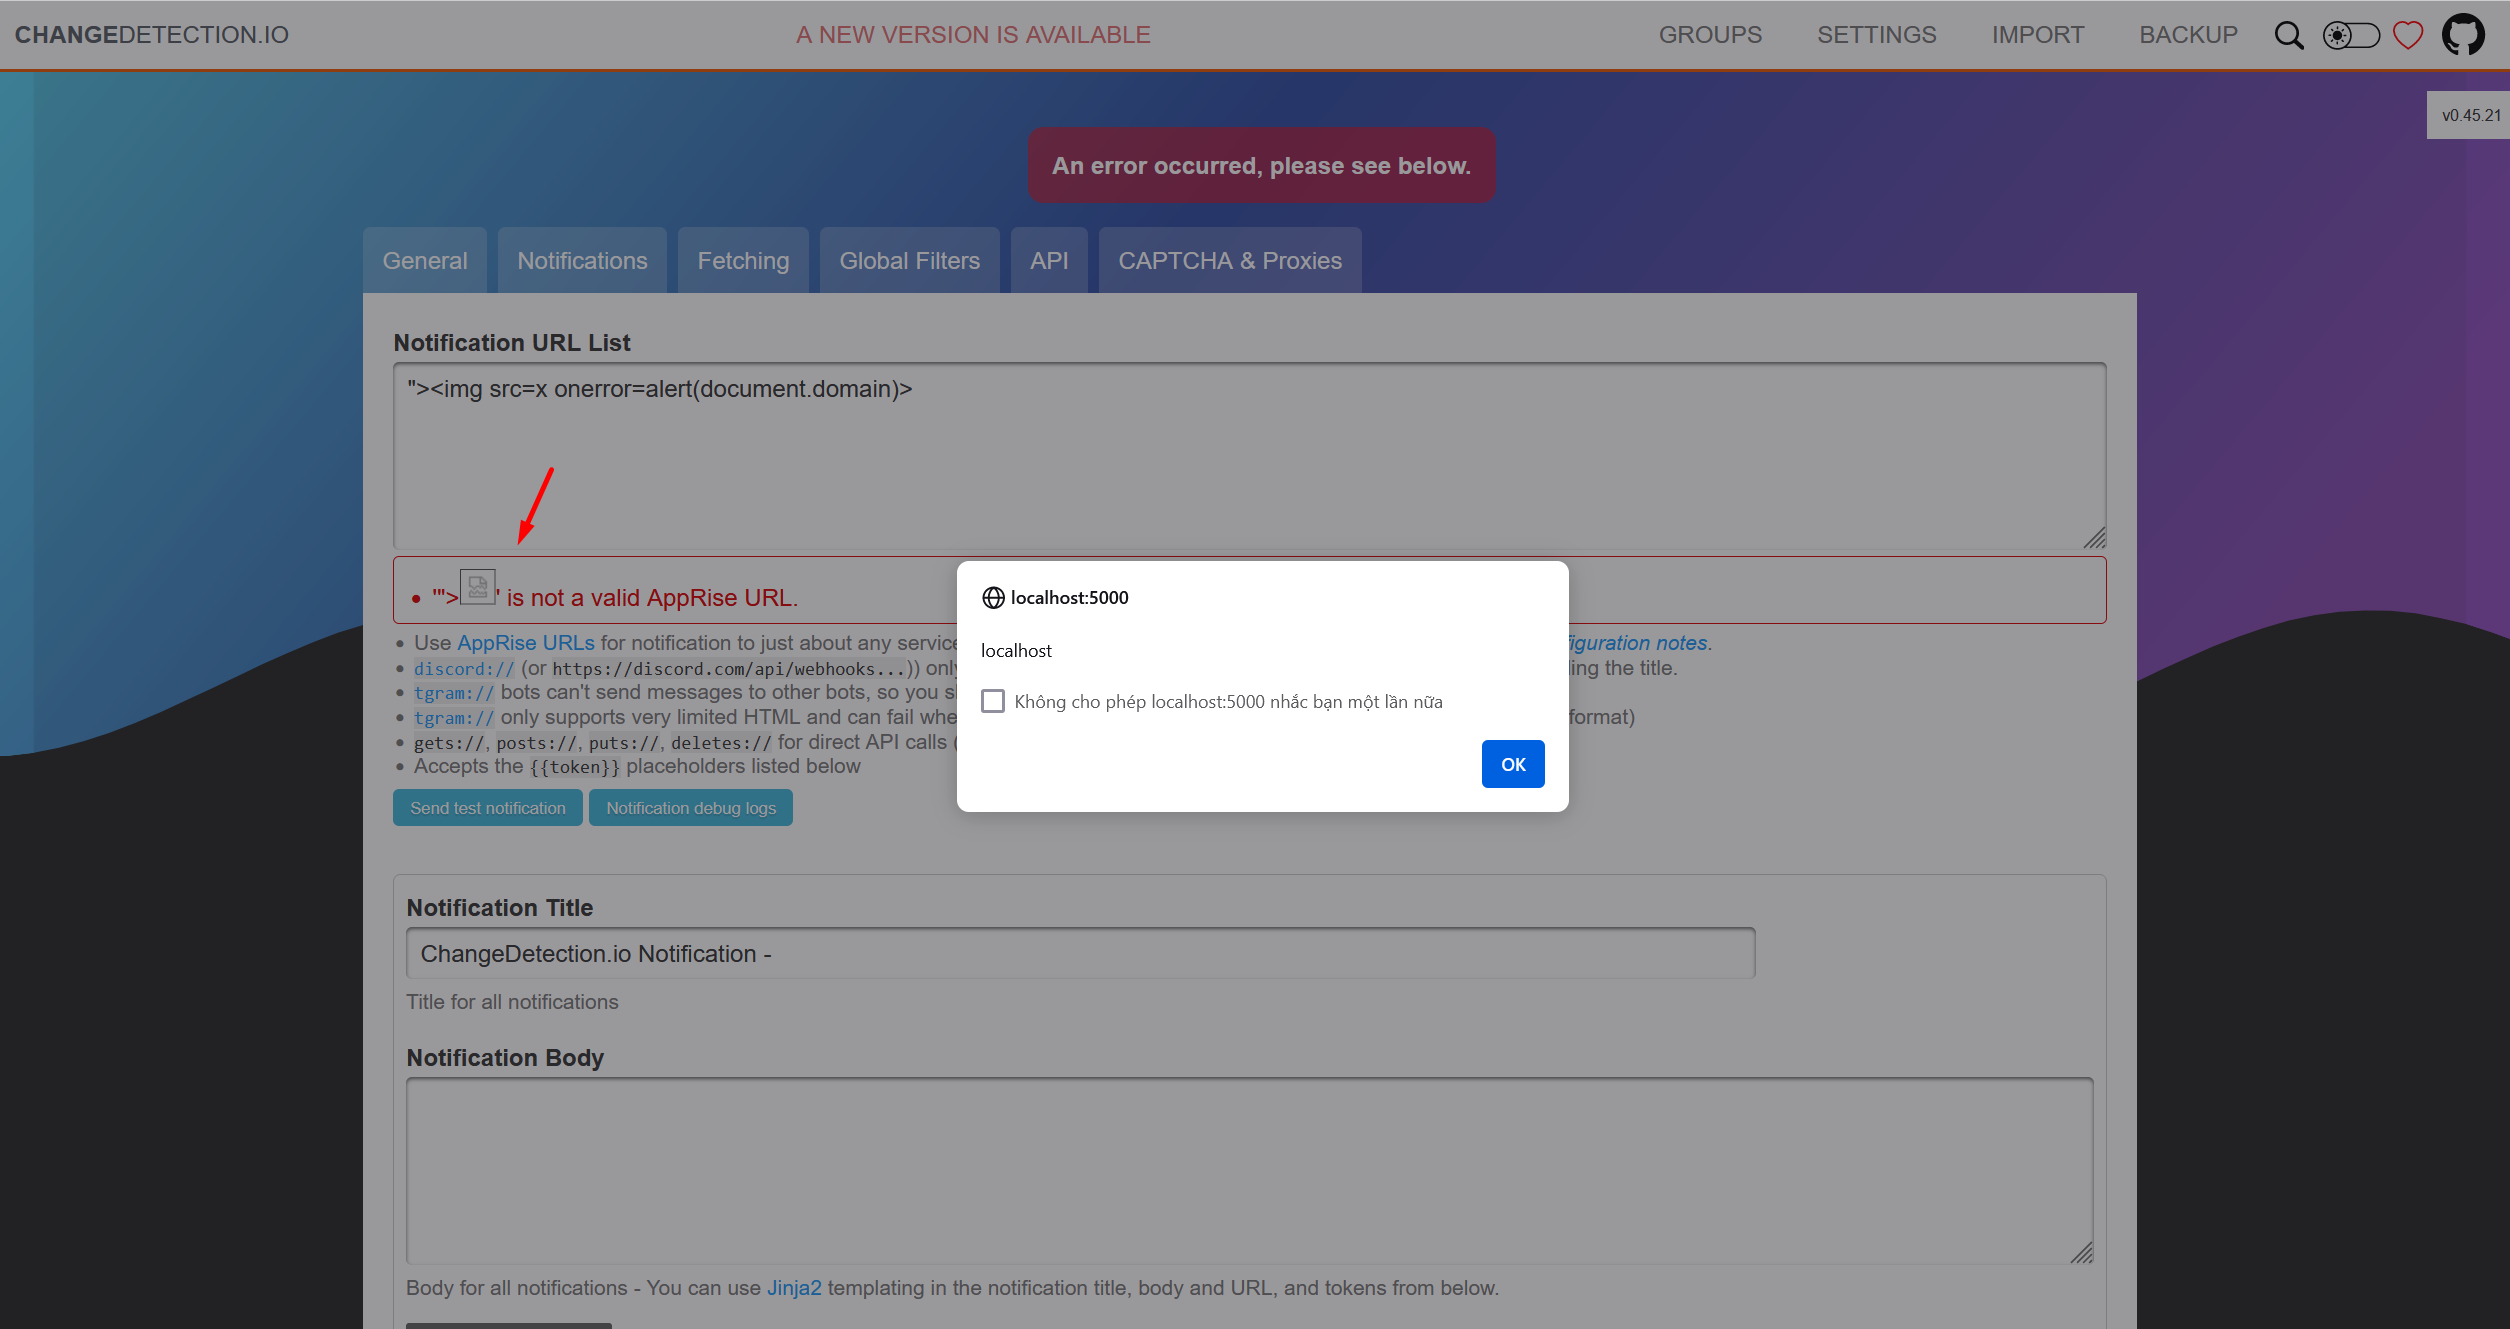\n\nRequests\n\n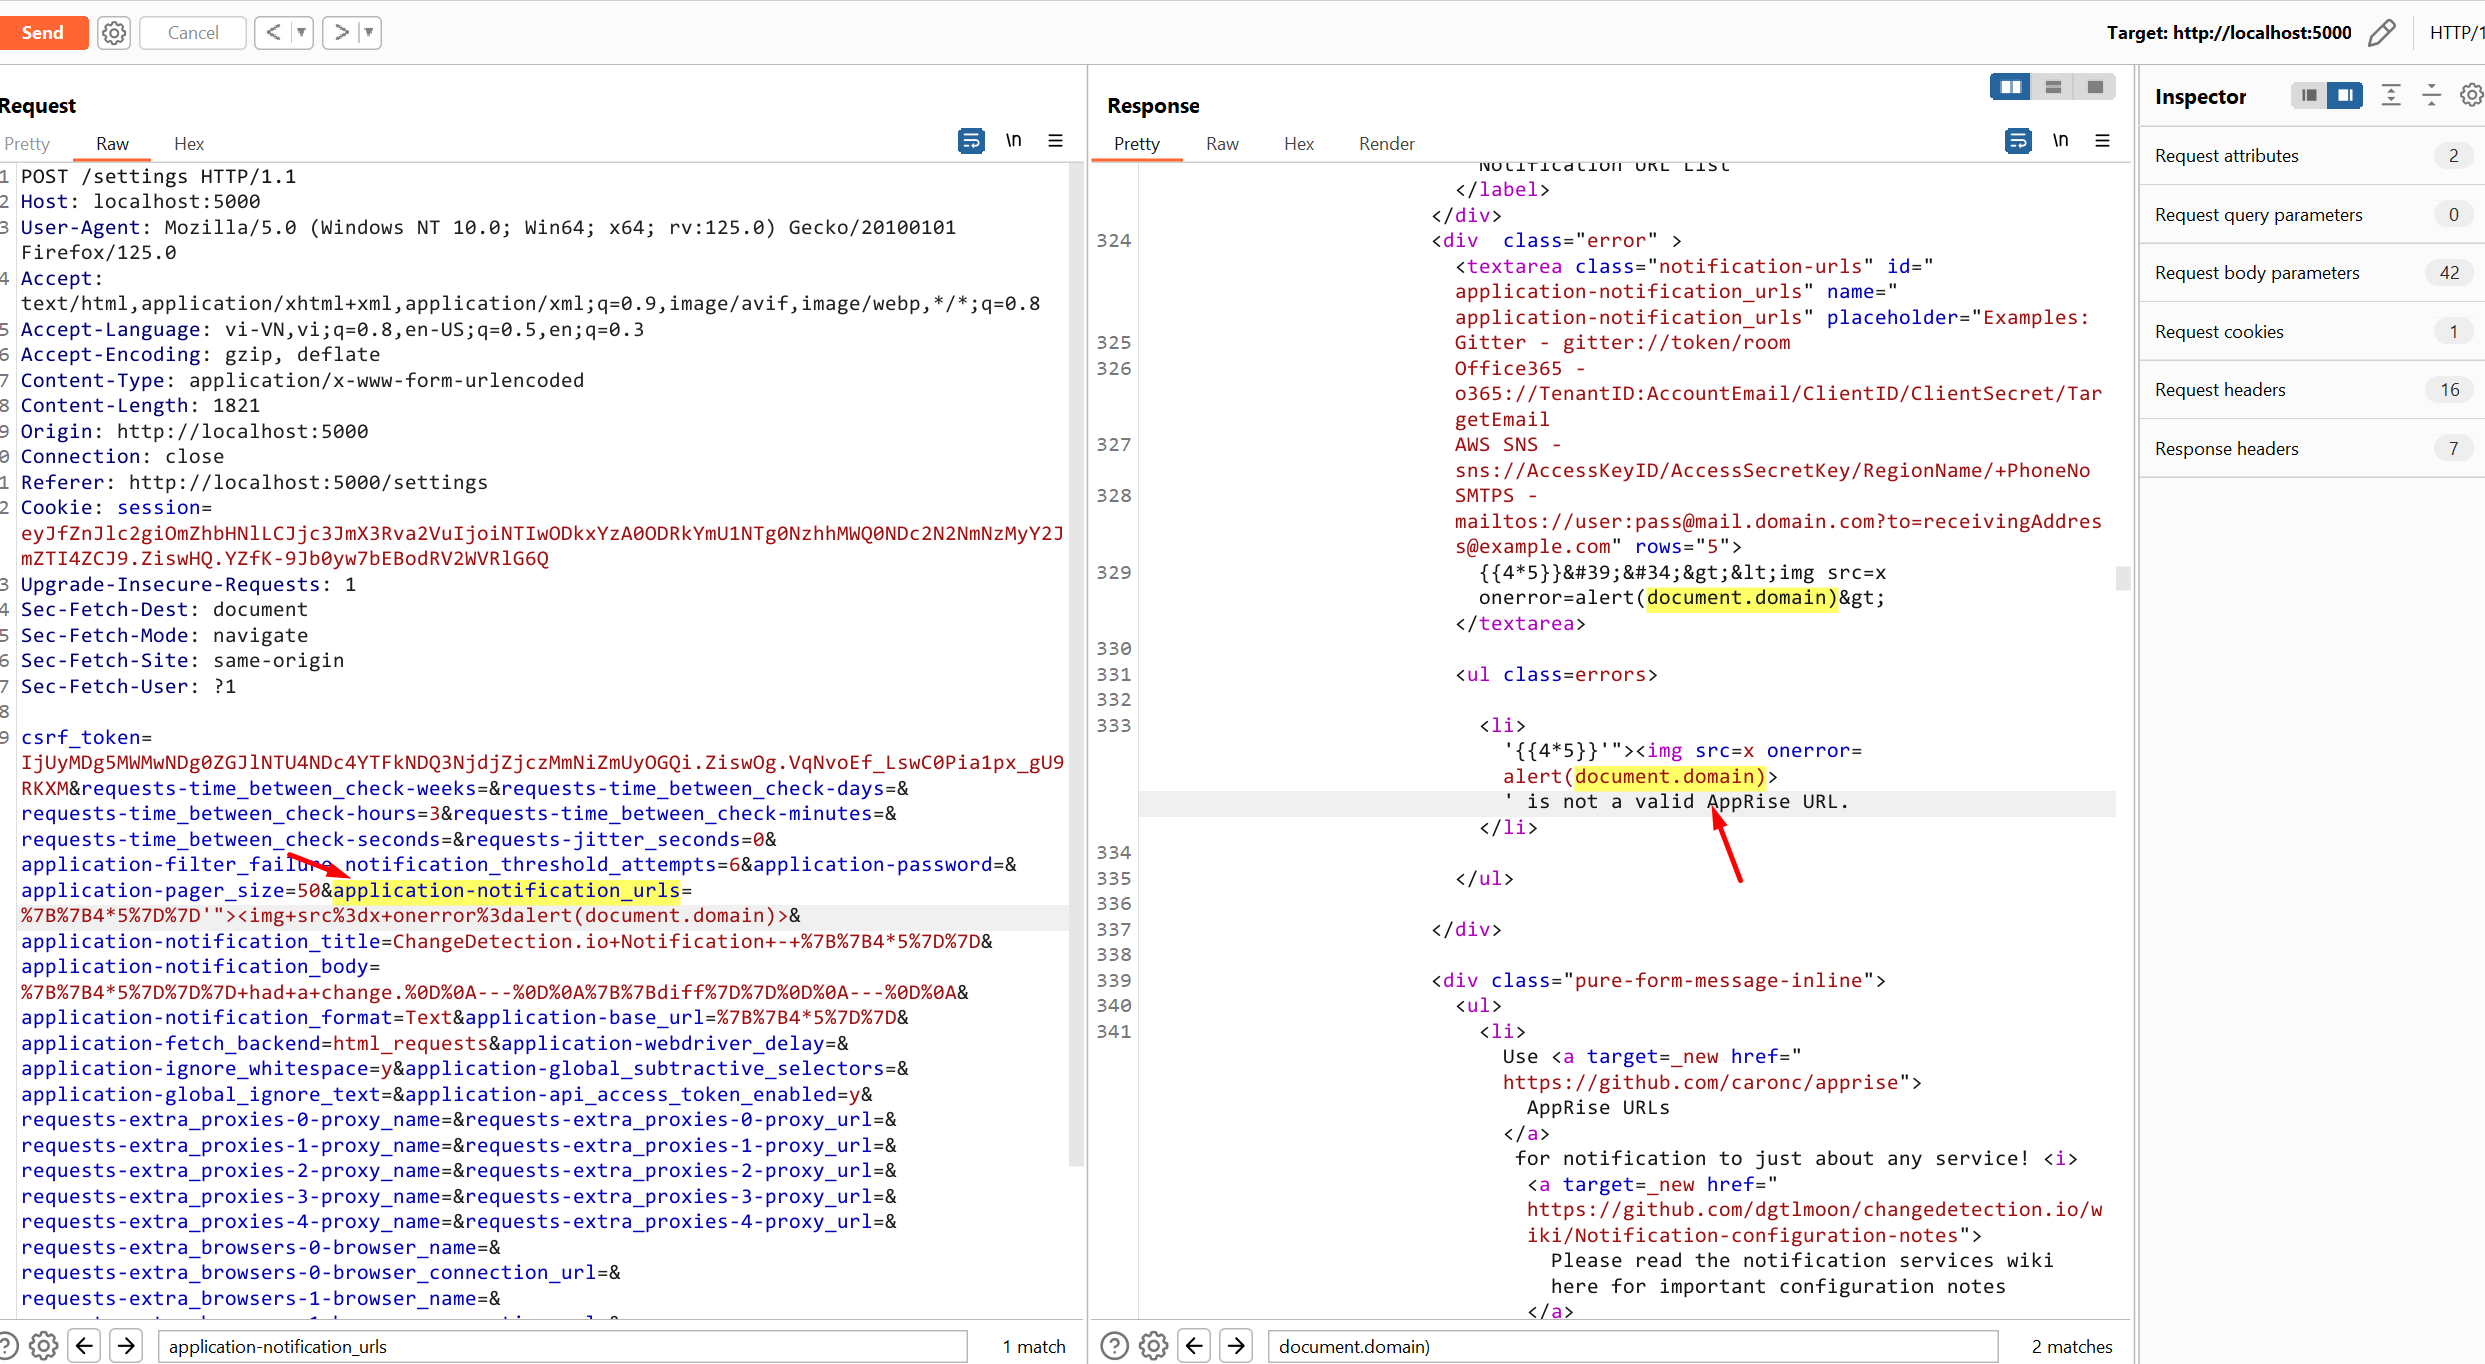\n\n\n### Impact\nA reflected XSS vulnerability happens when the user input from a URL or POST data is reflected on the page without being stored, thus allowing the attacker to inject malicious content\n",
"id": "GHSA-pwgc-w4x9-gw67",
"modified": "2024-05-03T17:53:22Z",
"published": "2024-05-03T17:53:22Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/dgtlmoon/changedetection.io/security/advisories/GHSA-pwgc-w4x9-gw67"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-34061"
},
{
"type": "WEB",
"url": "https://github.com/dgtlmoon/changedetection.io/commit/c0f000b1d1ce03733460805dbbedde445fe2c762"
},
{
"type": "PACKAGE",
"url": "https://github.com/dgtlmoon/changedetection.io"
},
{
"type": "WEB",
"url": "https://github.com/dgtlmoon/changedetection.io/blob/0.45.21/changedetectionio/forms.py#L226"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:N/I:L/A:N",
"type": "CVSS_V3"
}
],
"summary": "changedetection.io Cross-site Scripting vulnerability"
}
CVE-2024-34061 (GCVE-0-2024-34061)
Vulnerability from cvelistv5 – Published: 2024-05-02 13:58 – Updated: 2024-08-02 02:42- CWE-79 - Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')
| URL | Tags |
|---|---|
| https://github.com/dgtlmoon/changedetection.io/se… | x_refsource_CONFIRM |
| https://github.com/dgtlmoon/changedetection.io/co… | x_refsource_MISC |
| Vendor | Product | Version | |
|---|---|---|---|
| dgtlmoon | changedetection.io |
Affected:
< 0.45.22
|
|
| dgtlmoon | changedetection.io |
Affected:
0 , < 0.45.22
(custom)
cpe:2.3:a:dgtlmoon:changedetection.io:*:*:*:*:*:*:*:* |
{
  "containers": {
    "adp": [
      {
        "affected": [
          {
            "cpes": [
              "cpe:2.3:a:dgtlmoon:changedetection.io:*:*:*:*:*:*:*:*"
            ],
            "defaultStatus": "unknown",
            "product": "changedetection.io",
            "vendor": "dgtlmoon",
            "versions": [
              {
                "lessThan": "0.45.22",
                "status": "affected",
                "version": "0",
                "versionType": "custom"
              }
            ]
          }
        ],
        "metrics": [
          {
            "other": {
              "content": {
                "id": "CVE-2024-34061",
                "options": [
                  {
                    "Exploitation": "poc"
                  },
                  {
                    "Automatable": "no"
                  },
                  {
                    "Technical Impact": "partial"
                  }
                ],
                "role": "CISA Coordinator",
                "timestamp": "2024-05-02T15:39:27.438157Z",
                "version": "2.0.3"
              },
              "type": "ssvc"
            }
          }
        ],
        "providerMetadata": {
          "dateUpdated": "2024-06-06T17:59:08.404Z",
          "orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
          "shortName": "CISA-ADP"
        },
        "title": "CISA ADP Vulnrichment"
      },
      {
        "providerMetadata": {
          "dateUpdated": "2024-08-02T02:42:59.927Z",
          "orgId": "af854a3a-2127-422b-91ae-364da2661108",
          "shortName": "CVE"
        },
        "references": [
          {
            "name": "https://github.com/dgtlmoon/changedetection.io/security/advisories/GHSA-pwgc-w4x9-gw67",
            "tags": [
              "x_refsource_CONFIRM",
              "x_transferred"
            ],
            "url": "https://github.com/dgtlmoon/changedetection.io/security/advisories/GHSA-pwgc-w4x9-gw67"
          },
          {
            "name": "https://github.com/dgtlmoon/changedetection.io/commit/c0f000b1d1ce03733460805dbbedde445fe2c762",
            "tags": [
              "x_refsource_MISC",
              "x_transferred"
            ],
            "url": "https://github.com/dgtlmoon/changedetection.io/commit/c0f000b1d1ce03733460805dbbedde445fe2c762"
          }
        ],
        "title": "CVE Program Container"
      }
    ],
    "cna": {
      "affected": [
        {
          "product": "changedetection.io",
          "vendor": "dgtlmoon",
          "versions": [
            {
              "status": "affected",
              "version": "\u003c 0.45.22"
            }
          ]
        }
      ],
      "descriptions": [
        {
          "lang": "en",
          "value": "changedetection.io is a free open source web page change detection, website watcher, restock monitor and notification service. In affected versions Input in parameter notification_urls is not processed resulting in javascript execution in the application. A reflected XSS vulnerability happens when the user input from a URL or POST data is reflected on the page without being stored, thus allowing the attacker to inject malicious content. This issue has been addressed in version 0.45.22. Users are advised to upgrade. There are no known workarounds for this vulnerability."
        }
      ],
      "metrics": [
        {
          "cvssV3_1": {
            "attackComplexity": "LOW",
            "attackVector": "NETWORK",
            "availabilityImpact": "NONE",
            "baseScore": 4.3,
            "baseSeverity": "MEDIUM",
            "confidentialityImpact": "NONE",
            "integrityImpact": "LOW",
            "privilegesRequired": "NONE",
            "scope": "UNCHANGED",
            "userInteraction": "REQUIRED",
            "vectorString": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:N/I:L/A:N",
            "version": "3.1"
          }
        }
      ],
      "problemTypes": [
        {
          "descriptions": [
            {
              "cweId": "CWE-79",
              "description": "CWE-79: Improper Neutralization of Input During Web Page Generation (\u0027Cross-site Scripting\u0027)",
              "lang": "en",
              "type": "CWE"
            }
          ]
        }
      ],
      "providerMetadata": {
        "dateUpdated": "2024-05-02T13:58:21.939Z",
        "orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
        "shortName": "GitHub_M"
      },
      "references": [
        {
          "name": "https://github.com/dgtlmoon/changedetection.io/security/advisories/GHSA-pwgc-w4x9-gw67",
          "tags": [
            "x_refsource_CONFIRM"
          ],
          "url": "https://github.com/dgtlmoon/changedetection.io/security/advisories/GHSA-pwgc-w4x9-gw67"
        },
        {
          "name": "https://github.com/dgtlmoon/changedetection.io/commit/c0f000b1d1ce03733460805dbbedde445fe2c762",
          "tags": [
            "x_refsource_MISC"
          ],
          "url": "https://github.com/dgtlmoon/changedetection.io/commit/c0f000b1d1ce03733460805dbbedde445fe2c762"
        }
      ],
      "source": {
        "advisory": "GHSA-pwgc-w4x9-gw67",
        "discovery": "UNKNOWN"
      },
      "title": "Reflected cross site scripting in changedetection.io"
    }
  },
  "cveMetadata": {
    "assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
    "assignerShortName": "GitHub_M",
    "cveId": "CVE-2024-34061",
    "datePublished": "2024-05-02T13:58:21.939Z",
    "dateReserved": "2024-04-30T06:56:33.380Z",
    "dateUpdated": "2024-08-02T02:42:59.927Z",
    "state": "PUBLISHED"
  },
  "dataType": "CVE_RECORD",
  "dataVersion": "5.1"
}
PYSEC-2026-1243
Vulnerability from pysec - Published: 2026-07-07 11:45 - Updated: 2026-07-07 17:23Summary
Input in parameter notification_urls is not processed resulting in javascript execution in the application
Details
changedetection.io version: v0.45.21
https://github.com/dgtlmoon/changedetection.io/blob/0.45.21/changedetectionio/forms.py#L226
        for server_url in field.data:
            if not apobj.add(server_url):
                message = field.gettext('\'%s\' is not a valid AppRise URL.' % (server_url))
                raise ValidationError(message)
PoC
Setting > ADD Notification URL List
"><img src=x onerror=alert(document.domain)>
Requests
Impact
A reflected XSS vulnerability happens when the user input from a URL or POST data is reflected on the page without being stored, thus allowing the attacker to inject malicious content
| Name | purl | changedetection-io | pkg:pypi/changedetection-io |
|---|
{
"affected": [
{
"package": {
"ecosystem": "PyPI",
"name": "changedetection-io",
"purl": "pkg:pypi/changedetection-io"
},
"ranges": [
{
"events": [
{
"introduced": "0"
},
{
"fixed": "0.45.22"
}
],
"type": "ECOSYSTEM"
}
],
"versions": [
"0.38.2",
"0.39",
"0.39.1",
"0.39.10",
"0.39.10.post1",
"0.39.10.post2",
"0.39.11",
"0.39.12",
"0.39.13",
"0.39.13.1",
"0.39.14",
"0.39.14.1",
"0.39.15",
"0.39.16",
"0.39.17",
"0.39.17.1",
"0.39.17.2",
"0.39.18",
"0.39.19",
"0.39.19.1",
"0.39.2",
"0.39.20",
"0.39.20.1",
"0.39.20.2",
"0.39.20.3",
"0.39.20.4",
"0.39.21",
"0.39.21.1",
"0.39.22",
"0.39.22.1",
"0.39.3",
"0.39.4",
"0.39.5",
"0.39.6",
"0.39.7",
"0.39.8",
"0.39.9",
"0.40.0",
"0.40.0.1",
"0.40.0.2",
"0.40.0.3",
"0.40.0.4",
"0.40.1.0",
"0.40.1.1",
"0.40.2",
"0.40.3",
"0.41",
"0.41.1",
"0.42",
"0.42.1",
"0.42.2",
"0.42.3",
"0.43.1",
"0.43.2",
"0.44",
"0.44.1",
"0.45",
"0.45.1",
"0.45.11",
"0.45.12",
"0.45.13",
"0.45.14",
"0.45.15",
"0.45.16",
"0.45.17",
"0.45.18",
"0.45.19",
"0.45.2",
"0.45.20",
"0.45.21",
"0.45.3",
"0.45.4",
"0.45.5",
"0.45.6",
"0.45.7",
"0.45.7.1",
"0.45.7.2",
"0.45.7.3",
"0.45.8",
"0.45.8.1",
"0.45.9"
]
}
],
"aliases": [
"CVE-2024-34061",
"GHSA-pwgc-w4x9-gw67"
],
"details": "### Summary\n\nInput in parameter notification_urls is not processed resulting in javascript execution in the application\n\n### Details\nchangedetection.io version: v0.45.21\n\nhttps://github.com/dgtlmoon/changedetection.io/blob/0.45.21/changedetectionio/forms.py#L226\n\n```\n for server_url in field.data:\n if not apobj.add(server_url):\n message = field.gettext(\u0027\\\u0027%s\\\u0027 is not a valid AppRise URL.\u0027 % (server_url))\n raise ValidationError(message)\n```\n\n### PoC\n\nSetting \u003e ADD Notification URL List\n\n\n\n\n```\n\"\u003e\u003cimg src=x onerror=alert(document.domain)\u003e\n```\n\n\nRequests\n\n\n\n\n### Impact\nA reflected XSS vulnerability happens when the user input from a URL or POST data is reflected on the page without being stored, thus allowing the attacker to inject malicious content\n",
"id": "PYSEC-2026-1243",
"modified": "2026-07-07T17:23:53.990009Z",
"published": "2026-07-07T11:45:40.964806Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/dgtlmoon/changedetection.io/security/advisories/GHSA-pwgc-w4x9-gw67"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2024-34061"
},
{
"type": "WEB",
"url": "https://github.com/dgtlmoon/changedetection.io/commit/c0f000b1d1ce03733460805dbbedde445fe2c762"
},
{
"type": "PACKAGE",
"url": "https://github.com/dgtlmoon/changedetection.io"
},
{
"type": "WEB",
"url": "https://github.com/dgtlmoon/changedetection.io/blob/0.45.21/changedetectionio/forms.py#L226"
},
{
"type": "PACKAGE",
"url": "https://pypi.org/project/changedetection-io"
},
{
"type": "ADVISORY",
"url": "https://github.com/advisories/GHSA-pwgc-w4x9-gw67"
}
],
"severity": [
{
"score": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:N/I:L/A:N",
"type": "CVSS_V3"
}
],
"summary": "changedetection.io Cross-site Scripting vulnerability"
}
Sightings
| Author | Source | Type | Date | Other |
|---|
Nomenclature
- Seen: The vulnerability was mentioned, discussed, or observed by the user.
- Confirmed: The vulnerability has been validated from an analyst's perspective.
- Published Proof of Concept: A public proof of concept is available for this vulnerability.
- Exploited: The vulnerability was observed as exploited by the user who reported the sighting.
- Patched: The vulnerability was observed as successfully patched by the user who reported the sighting.
- Not exploited: The vulnerability was not observed as exploited by the user who reported the sighting.
- Not confirmed: The user expressed doubt about the validity of the vulnerability.
- Not patched: The vulnerability was not observed as successfully patched by the user who reported the sighting.
The approach is described in our paper Mapping CVEs to MITRE ATT&CK Techniques: A Curated Gold-Set Classifier and the Limits of LLM-Assisted Label Expansion.
Browse all ATT&CK techniques and the vulnerabilities related to each.
Related by attack behaviour
Vulnerabilities whose description is nearest to this one in the vector space of the CIRCL/vulnerability-attack-technique-biencoder model. This is a similarity search over the bi-encoder space (plain cosine), not a classification, and it has no measured accuracy.