CVE-2025-32963 (GCVE-0-2025-32963)
Vulnerability from cvelistv5 – Published: 2025-04-22 17:14 – Updated: 2026-01-23 17:16- CWE-522 - Insufficiently Protected Credentials
| URL | Tags |
|---|---|
| https://github.com/minio/operator/security/adviso… | x_refsource_CONFIRM |
| https://github.com/minio/operator/commit/d586294d… | x_refsource_MISC |
| https://github.com/minio/operator/releases/tag/v7.1.0 | x_refsource_MISC |
{
  "containers": {
    "adp": [
      {
        "metrics": [
          {
            "other": {
              "content": {
                "id": "CVE-2025-32963",
                "options": [
                  {
                    "Exploitation": "none"
                  },
                  {
                    "Automatable": "yes"
                  },
                  {
                    "Technical Impact": "partial"
                  }
                ],
                "role": "CISA Coordinator",
                "timestamp": "2025-04-24T19:56:29.253678Z",
                "version": "2.0.3"
              },
              "type": "ssvc"
            }
          }
        ],
        "providerMetadata": {
          "dateUpdated": "2025-04-25T16:03:14.020Z",
          "orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
          "shortName": "CISA-ADP"
        },
        "title": "CISA ADP Vulnrichment"
      }
    ],
    "cna": {
      "affected": [
        {
          "product": "operator",
          "vendor": "minio",
          "versions": [
            {
              "status": "affected",
              "version": "\u003c 7.1.0"
            }
          ]
        }
      ],
      "descriptions": [
        {
          "lang": "en",
          "value": "MinIO Operator STS is a native IAM Authentication for Kubernetes. Prior to version 7.1.0, if no audiences are provided for the `spec.audiences` field, the default will be of the Kubernetes apiserver. Without scoping, it can be replayed to other internal systems, which may unintentionally trust it. This issue has been patched in version 7.1.0."
        }
      ],
      "metrics": [
        {
          "cvssV4_0": {
            "attackComplexity": "LOW",
            "attackRequirements": "NONE",
            "attackVector": "NETWORK",
            "baseScore": 6.9,
            "baseSeverity": "MEDIUM",
            "privilegesRequired": "NONE",
            "subAvailabilityImpact": "NONE",
            "subConfidentialityImpact": "NONE",
            "subIntegrityImpact": "NONE",
            "userInteraction": "NONE",
            "vectorString": "CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:N/VA:N/SC:N/SI:N/SA:N",
            "version": "4.0",
            "vulnAvailabilityImpact": "NONE",
            "vulnConfidentialityImpact": "LOW",
            "vulnIntegrityImpact": "NONE"
          }
        }
      ],
      "problemTypes": [
        {
          "descriptions": [
            {
              "cweId": "CWE-522",
              "description": "CWE-522: Insufficiently Protected Credentials",
              "lang": "en",
              "type": "CWE"
            }
          ]
        }
      ],
      "providerMetadata": {
        "dateUpdated": "2026-01-23T17:16:16.416Z",
        "orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
        "shortName": "GitHub_M"
      },
      "references": [
        {
          "name": "https://github.com/minio/operator/security/advisories/GHSA-7m6v-q233-q9j9",
          "tags": [
            "x_refsource_CONFIRM"
          ],
          "url": "https://github.com/minio/operator/security/advisories/GHSA-7m6v-q233-q9j9"
        },
        {
          "name": "https://github.com/minio/operator/commit/d586294d526bf0d8e6097225114655f68b0adcc5",
          "tags": [
            "x_refsource_MISC"
          ],
          "url": "https://github.com/minio/operator/commit/d586294d526bf0d8e6097225114655f68b0adcc5"
        },
        {
          "name": "https://github.com/minio/operator/releases/tag/v7.1.0",
          "tags": [
            "x_refsource_MISC"
          ],
          "url": "https://github.com/minio/operator/releases/tag/v7.1.0"
        }
      ],
      "source": {
        "advisory": "GHSA-7m6v-q233-q9j9",
        "discovery": "UNKNOWN"
      },
      "title": "Minio Operator uses Kubernetes apiserver audience for AssumeRoleWithWebIdentity STS"
    }
  },
  "cveMetadata": {
    "assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
    "assignerShortName": "GitHub_M",
    "cveId": "CVE-2025-32963",
    "datePublished": "2025-04-22T17:14:56.958Z",
    "dateReserved": "2025-04-14T21:47:11.453Z",
    "dateUpdated": "2026-01-23T17:16:16.416Z",
    "state": "PUBLISHED"
  },
  "dataType": "CVE_RECORD",
  "dataVersion": "5.2",
  "vulnerability-lookup:meta": {
    "epss": {
      "cve": "CVE-2025-32963",
      "date": "2026-09-13",
      "epss": "0.00593",
      "percentile": "0.4651"
    },
    "nvd": "{\"cve\":{\"id\":\"CVE-2025-32963\",\"sourceIdentifier\":\"security-advisories@github.com\",\"published\":\"2025-04-22T18:16:00.710\",\"lastModified\":\"2026-06-17T09:12:52.397\",\"vulnStatus\":\"Deferred\",\"cveTags\":[],\"descriptions\":[{\"lang\":\"en\",\"value\":\"MinIO Operator STS is a native IAM Authentication for Kubernetes. Prior to version 7.1.0, if no audiences are provided for the `spec.audiences` field, the default will be of the Kubernetes apiserver. Without scoping, it can be replayed to other internal systems, which may unintentionally trust it. This issue has been patched in version 7.1.0.\"},{\"lang\":\"es\",\"value\":\"MinIO Operator STS es una autenticaci\u00f3n IAM nativa para Kubernetes. Antes de la versi\u00f3n 7.1.0, si no se proporcionaban audiencias para el campo `spec.audiences`, el valor predeterminado era el del servidor de API de Kubernetes. Sin \u00e1mbito, se puede reproducir en otros sistemas internos, que podr\u00edan confiar en \u00e9l involuntariamente. Este problema se ha corregido en la versi\u00f3n 7.1.0.\"}],\"affected\":[{\"source\":\"security-advisories@github.com\",\"affectedData\":[{\"vendor\":\"minio\",\"product\":\"operator\",\"versions\":[{\"version\":\"\u003c 7.1.0\",\"status\":\"affected\"}]}]}],\"metrics\":{\"cvssMetricV40\":[{\"source\":\"security-advisories@github.com\",\"type\":\"Secondary\",\"cvssData\":{\"version\":\"4.0\",\"vectorString\":\"CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:N/VA:N/SC:N/SI:N/SA:N/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X\",\"baseScore\":6.9,\"baseSeverity\":\"MEDIUM\",\"attackVector\":\"NETWORK\",\"attackComplexity\":\"LOW\",\"attackRequirements\":\"NONE\",\"privilegesRequired\":\"NONE\",\"userInteraction\":\"NONE\",\"vulnConfidentialityImpact\":\"LOW\",\"vulnIntegrityImpact\":\"NONE\",\"vulnAvailabilityImpact\":\"NONE\",\"subConfidentialityImpact\":\"NONE\",\"subIntegrityImpact\":\"NONE\",\"subAvailabilityImpact\":\"NONE\",\"exploitMaturity\":\"NOT_DEFINED\",\"confidentialityRequirement\":\"NOT_DEFINED\",\"integrityRequirement\":\"NOT_DEFINED\",\"availabilityRequirement\":\"NOT_DEFINED\",\"modifiedAttackVector\":\"NOT_DEFINED\",\"modifiedAttackComplexity\":\"NOT_DEFINED\",\"modifiedAttackRequirements\":\"NOT_DEFINED\",\"modifiedPrivilegesRequired\":\"NOT_DEFINED\",\"modifiedUserInteraction\":\"NOT_DEFINED\",\"modifiedVulnConfidentialityImpact\":\"NOT_DEFINED\",\"modifiedVulnIntegrityImpact\":\"NOT_DEFINED\",\"modifiedVulnAvailabilityImpact\":\"NOT_DEFINED\",\"modifiedSubConfidentialityImpact\":\"NOT_DEFINED\",\"modifiedSubIntegrityImpact\":\"NOT_DEFINED\",\"modifiedSubAvailabilityImpact\":\"NOT_DEFINED\",\"Safety\":\"NOT_DEFINED\",\"Automatable\":\"NOT_DEFINED\",\"Recovery\":\"NOT_DEFINED\",\"valueDensity\":\"NOT_DEFINED\",\"vulnerabilityResponseEffort\":\"NOT_DEFINED\",\"providerUrgency\":\"NOT_DEFINED\"}}],\"ssvcV203\":[{\"source\":\"134c704f-9b21-4f2e-91b3-4a467353bcc0\",\"ssvcData\":{\"timestamp\":\"2025-04-24T19:56:29.253678Z\",\"id\":\"CVE-2025-32963\",\"options\":[{\"exploitation\":\"none\"},{\"automatable\":\"yes\"},{\"technicalImpact\":\"partial\"}],\"role\":\"CISA Coordinator\",\"version\":\"2.0.3\"}}]},\"weaknesses\":[{\"source\":\"security-advisories@github.com\",\"type\":\"Secondary\",\"description\":[{\"lang\":\"en\",\"value\":\"CWE-522\"}]}],\"references\":[{\"url\":\"https://github.com/minio/operator/commit/d586294d526bf0d8e6097225114655f68b0adcc5\",\"source\":\"security-advisories@github.com\"},{\"url\":\"https://github.com/minio/operator/releases/tag/v7.1.0\",\"source\":\"security-advisories@github.com\"},{\"url\":\"https://github.com/minio/operator/security/advisories/GHSA-7m6v-q233-q9j9\",\"source\":\"security-advisories@github.com\"}]}}",
    "redhat_vex": {
      "current_release_date": "2026-01-23T21:14:58+00:00",
      "cve": "CVE-2025-32963",
      "id": "CVE-2025-32963",
      "initial_release_date": "2025-01-01T00:00:00+00:00",
      "product_status:known_not_affected": "1",
      "source": "Red Hat CSAF VEX",
      "status": "final",
      "title": "Minio Operator uses Kubernetes apiserver audience for AssumeRoleWithWebIdentity STS",
      "url": "https://security.access.redhat.com/data/csaf/v2/vex/2025/cve-2025-32963.json",
      "version": "3"
    },
    "suse_vex": {
      "aggregate_severity": "moderate",
      "current_release_date": "2026-08-25T01:58:42Z",
      "cve": "CVE-2025-32963",
      "id": "CVE-2025-32963",
      "initial_release_date": "2025-04-24T03:24:12Z",
      "product_status:recommended": "4",
      "source": "SUSE CSAF VEX",
      "status": "interim",
      "title": "SUSE CVE CVE-2025-32963",
      "url": "https://ftp.suse.com/pub/projects/security/csaf-vex/cve-2025-32963.json",
      "version": "6"
    },
    "vulnrichment": {
      "containers": "{\"adp\": [{\"title\": \"CISA ADP Vulnrichment\", \"metrics\": [{\"other\": {\"type\": \"ssvc\", \"content\": {\"id\": \"CVE-2025-32963\", \"role\": \"CISA Coordinator\", \"options\": [{\"Exploitation\": \"none\"}, {\"Automatable\": \"yes\"}, {\"Technical Impact\": \"partial\"}], \"version\": \"2.0.3\", \"timestamp\": \"2025-04-24T19:56:29.253678Z\"}}}], \"providerMetadata\": {\"orgId\": \"134c704f-9b21-4f2e-91b3-4a467353bcc0\", \"shortName\": \"CISA-ADP\", \"dateUpdated\": \"2025-04-24T19:56:30.819Z\"}}], \"cna\": {\"title\": \"Minio Operator uses Kubernetes apiserver audience for AssumeRoleWithWebIdentity STS\", \"source\": {\"advisory\": \"GHSA-7m6v-q233-q9j9\", \"discovery\": \"UNKNOWN\"}, \"metrics\": [{\"cvssV4_0\": {\"version\": \"4.0\", \"baseScore\": 6.9, \"attackVector\": \"NETWORK\", \"baseSeverity\": \"MEDIUM\", \"vectorString\": \"CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:N/VA:N/SC:N/SI:N/SA:N\", \"userInteraction\": \"NONE\", \"attackComplexity\": \"LOW\", \"attackRequirements\": \"NONE\", \"privilegesRequired\": \"NONE\", \"subIntegrityImpact\": \"NONE\", \"vulnIntegrityImpact\": \"NONE\", \"subAvailabilityImpact\": \"NONE\", \"vulnAvailabilityImpact\": \"NONE\", \"subConfidentialityImpact\": \"NONE\", \"vulnConfidentialityImpact\": \"LOW\"}}], \"affected\": [{\"vendor\": \"minio\", \"product\": \"operator\", \"versions\": [{\"status\": \"affected\", \"version\": \"\u003c 7.1.0\"}]}], \"references\": [{\"url\": \"https://github.com/minio/operator/security/advisories/GHSA-7m6v-q233-q9j9\", \"name\": \"https://github.com/minio/operator/security/advisories/GHSA-7m6v-q233-q9j9\", \"tags\": [\"x_refsource_CONFIRM\"]}, {\"url\": \"https://github.com/minio/operator/commit/d586294d526bf0d8e6097225114655f68b0adcc5\", \"name\": \"https://github.com/minio/operator/commit/d586294d526bf0d8e6097225114655f68b0adcc5\", \"tags\": [\"x_refsource_MISC\"]}, {\"url\": \"https://github.com/minio/operator/releases/tag/v7.1.0\", \"name\": \"https://github.com/minio/operator/releases/tag/v7.1.0\", \"tags\": [\"x_refsource_MISC\"]}], \"descriptions\": [{\"lang\": \"en\", \"value\": \"MinIO Operator STS is a native IAM Authentication for Kubernetes. Prior to version 7.1.0, if no audiences are provided for the `spec.audiences` field, the default will be of the Kubernetes apiserver. Without scoping, it can be replayed to other internal systems, which may unintentionally trust it. This issue has been patched in version 7.1.0.\"}], \"problemTypes\": [{\"descriptions\": [{\"lang\": \"en\", \"type\": \"CWE\", \"cweId\": \"CWE-522\", \"description\": \"CWE-522: Insufficiently Protected Credentials\"}]}], \"providerMetadata\": {\"orgId\": \"a0819718-46f1-4df5-94e2-005712e83aaa\", \"shortName\": \"GitHub_M\", \"dateUpdated\": \"2026-01-23T17:16:16.416Z\"}}}",
      "cveMetadata": "{\"cveId\": \"CVE-2025-32963\", \"state\": \"PUBLISHED\", \"dateUpdated\": \"2026-01-23T17:16:16.416Z\", \"dateReserved\": \"2025-04-14T21:47:11.453Z\", \"assignerOrgId\": \"a0819718-46f1-4df5-94e2-005712e83aaa\", \"datePublished\": \"2025-04-22T17:14:56.958Z\", \"assignerShortName\": \"GitHub_M\"}",
      "dataType": "CVE_RECORD",
      "dataVersion": "5.2"
    }
  }
}
FKIE_CVE-2025-32963
Vulnerability from fkie_nvd - Published: 2025-04-22 18:16 - Updated: 2026-06-17 09:12| Vendor | Product | Version |
|---|
{
  "affected": [
    {
      "affectedData": [
        {
          "product": "operator",
          "vendor": "minio",
          "versions": [
            {
              "status": "affected",
              "version": "\u003c 7.1.0"
            }
          ]
        }
      ],
      "source": "security-advisories@github.com"
    }
  ],
  "cveTags": [],
  "descriptions": [
    {
      "lang": "en",
      "value": "MinIO Operator STS is a native IAM Authentication for Kubernetes. Prior to version 7.1.0, if no audiences are provided for the `spec.audiences` field, the default will be of the Kubernetes apiserver. Without scoping, it can be replayed to other internal systems, which may unintentionally trust it. This issue has been patched in version 7.1.0."
    },
    {
      "lang": "es",
      "value": "MinIO Operator STS es una autenticaci\u00f3n IAM nativa para Kubernetes. Antes de la versi\u00f3n 7.1.0, si no se proporcionaban audiencias para el campo `spec.audiences`, el valor predeterminado era el del servidor de API de Kubernetes. Sin \u00e1mbito, se puede reproducir en otros sistemas internos, que podr\u00edan confiar en \u00e9l involuntariamente. Este problema se ha corregido en la versi\u00f3n 7.1.0."
    }
  ],
  "id": "CVE-2025-32963",
  "lastModified": "2026-06-17T09:12:52.397",
  "metrics": {
    "cvssMetricV40": [
      {
        "cvssData": {
          "Automatable": "NOT_DEFINED",
          "Recovery": "NOT_DEFINED",
          "Safety": "NOT_DEFINED",
          "attackComplexity": "LOW",
          "attackRequirements": "NONE",
          "attackVector": "NETWORK",
          "availabilityRequirement": "NOT_DEFINED",
          "baseScore": 6.9,
          "baseSeverity": "MEDIUM",
          "confidentialityRequirement": "NOT_DEFINED",
          "exploitMaturity": "NOT_DEFINED",
          "integrityRequirement": "NOT_DEFINED",
          "modifiedAttackComplexity": "NOT_DEFINED",
          "modifiedAttackRequirements": "NOT_DEFINED",
          "modifiedAttackVector": "NOT_DEFINED",
          "modifiedPrivilegesRequired": "NOT_DEFINED",
          "modifiedSubAvailabilityImpact": "NOT_DEFINED",
          "modifiedSubConfidentialityImpact": "NOT_DEFINED",
          "modifiedSubIntegrityImpact": "NOT_DEFINED",
          "modifiedUserInteraction": "NOT_DEFINED",
          "modifiedVulnAvailabilityImpact": "NOT_DEFINED",
          "modifiedVulnConfidentialityImpact": "NOT_DEFINED",
          "modifiedVulnIntegrityImpact": "NOT_DEFINED",
          "privilegesRequired": "NONE",
          "providerUrgency": "NOT_DEFINED",
          "subAvailabilityImpact": "NONE",
          "subConfidentialityImpact": "NONE",
          "subIntegrityImpact": "NONE",
          "userInteraction": "NONE",
          "valueDensity": "NOT_DEFINED",
          "vectorString": "CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:N/VA:N/SC:N/SI:N/SA:N/E:X/CR:X/IR:X/AR:X/MAV:X/MAC:X/MAT:X/MPR:X/MUI:X/MVC:X/MVI:X/MVA:X/MSC:X/MSI:X/MSA:X/S:X/AU:X/R:X/V:X/RE:X/U:X",
          "version": "4.0",
          "vulnAvailabilityImpact": "NONE",
          "vulnConfidentialityImpact": "LOW",
          "vulnIntegrityImpact": "NONE",
          "vulnerabilityResponseEffort": "NOT_DEFINED"
        },
        "source": "security-advisories@github.com",
        "type": "Secondary"
      }
    ],
    "ssvcV203": [
      {
        "source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
        "ssvcData": {
          "id": "CVE-2025-32963",
          "options": [
            {
              "exploitation": "none"
            },
            {
              "automatable": "yes"
            },
            {
              "technicalImpact": "partial"
            }
          ],
          "role": "CISA Coordinator",
          "timestamp": "2025-04-24T19:56:29.253678Z",
          "version": "2.0.3"
        }
      }
    ]
  },
  "published": "2025-04-22T18:16:00.710",
  "references": [
    {
      "source": "security-advisories@github.com",
      "url": "https://github.com/minio/operator/commit/d586294d526bf0d8e6097225114655f68b0adcc5"
    },
    {
      "source": "security-advisories@github.com",
      "url": "https://github.com/minio/operator/releases/tag/v7.1.0"
    },
    {
      "source": "security-advisories@github.com",
      "url": "https://github.com/minio/operator/security/advisories/GHSA-7m6v-q233-q9j9"
    }
  ],
  "sourceIdentifier": "security-advisories@github.com",
  "vulnStatus": "Deferred",
  "weaknesses": [
    {
      "description": [
        {
          "lang": "en",
          "value": "CWE-522"
        }
      ],
      "source": "security-advisories@github.com",
      "type": "Secondary"
    }
  ]
}
GHSA-7M6V-Q233-Q9J9
Vulnerability from github – Published: 2025-04-21 22:51 – Updated: 2026-01-23 17:16Prevent token leakage / privilege escalation
MinIO Operator STS: A Quick Overview
MinIO Operator STS is a native IAM Authentication for Kubernetes. MinIO Operator offers support for Secure Tokens (a.k.a. STS) which are a form of temporary access credentials for your MinIO Tenant. In essence, this allows you to control access to your MinIO tenant from your applications without having to explicitly create credentials for each application.
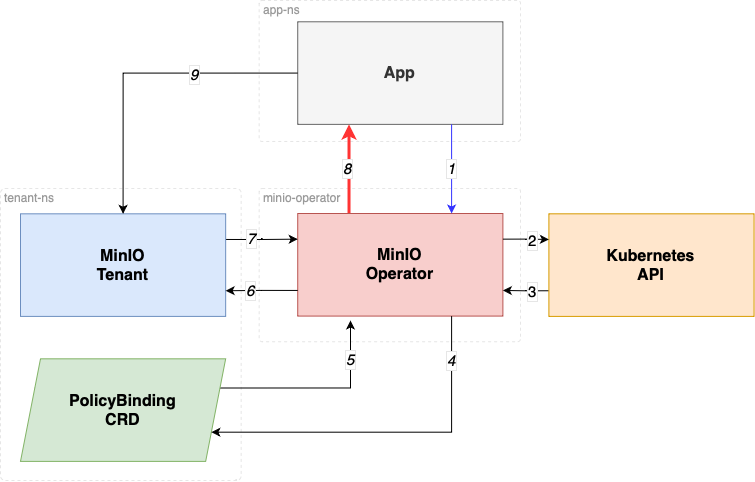
For an application to gain access into a MinIO Tenant, a PolicyBinding resource is required, granting explicit access to the applications by validating the kubernetes Service Account authorization token.
The service account token is validated as follows:
- The application calls
AssumeRoleWithWebIdentityAPI MinIO Operator provides. - MinIO Operator verifies the Service Account token agains the kubernetes API using the TokenReview API
- MinIO Operator reviews the TokenReviewResult confirms if the token is a valid token and the user is authenticated.
- MinIO Operator validates the service account has
PolicyBindingin the Tenant namespace. - MinIO Operator gets the PolicyBinding
- MinIO Operator calls the AssumeRole API in the MinIO Tenant
- MinIO Operator obtains temporary credentials (STS).
- MinIO Operator return temporary Credentials to the requester application.
- The applicaiton consumes Object Storage using the temporary credentials.
Understanding Audiences in Kubernetes TokenReview
In step 2 the TokenReview API call attempts to authenticate a token to a known user, TokenReviewStatus is the result of the TokenReview request.
Audiences are audience identifiers chosen by the authenticator that are compatible with both the TokenReview and token.
An identifier is any identifier in the intersection of the TokenReviewSpec audiences and the token's audiences.
A client of the TokenReview API that sets the spec.audiences field should validate that a compatible audience identifier is returned in the status.audiences field to ensure that the TokenReview server is audience aware.
If no audiences are provided, the audience will default to the audience of the Kubernetes apiserver.
Solution: Properly Issuing and Using Audience-Specific ServiceAccount Tokens
This PR ensures the Operator STS service request the Service Account JWT to belong to the audiencests.min.io in the TokenReviewRequest.
This PR ensures the examples and documentation provided guides in how to create Service accounts with "disabled auto mount services tokens", by doing this the pods where the service account is used no longer mounts the service account automatically in the path /var/run/secrets/kubernetes.io/serviceaccount.
For illustrative purposes, here is how you disable auto mount of service account tokens at the service account level.
apiVersion: v1
kind: ServiceAccount
metadata:
  namespace: namespace-name
  name: service-account name
automountServiceAccountToken: false
Additionally documentation and examples show how to request an audience-specific token with audience sts.min.io, by asking for an ServiceAccount Token to be audience specific.
For illustrative purposes, here is how you request an audience specific service account token in a pod:
apiVersion: batch/v1
kind: Job
metadata:
  name: job-name
  namespace: job-namespace
spec:
  template:
    spec:
      serviceAccountName: service-account-name
      volumes:
        - name: sa-token
          projected:
            sources:
              - serviceAccountToken:
                  audience: "sts.min.io"
                  expirationSeconds: 86400
                  path: token
      containers:
        - name: mc
...
          volumeMounts:
            - name: sa-token
              mountPath: /var/run/secrets/sts.min.io/serviceaccount
              readOnly: true
How this prevent a token leakage or possible privilege escalation?.
This setup prevents privilege escalation and token leakage by combining multiple defense-in-depth mechanisms that ensure service account tokens are only usable by their intended audience, short-lived, and not exposed unnecessarily.
Audience restriction (aud: sts.min.io)
Problem: A ServiceAccount token is often valid for multiple audiences (e.g., the default Kubernetes API server). Without scoping, it can be replayed to other internal systems, which may unintentionally trust it.
Mitigation: Now we enforce that tokens are explicitly created for the sts.min.io audience using the Kubernetes TokenRequest API, and the MinIO Operator:
Sends audiences: ["sts.min.io"] in the TokenReview.
Verifies that the token was issued with this audience via status.audiences.
Effect: Even if a token is stolen or misused, it will fail validation if used outside the sts.min.io STS endpoint (e.g., reused at the API server or another service).
Token Leakage Mitigation
Disabling auto-mounted service account tokens
Problem: By default, Kubernetes mounts long-lived service account tokens into all pods at /var/run/secrets/kubernetes.io/serviceaccount, making them vulnerable to theft if the container is compromised.
Mitigation: No we guide users to set automountServiceAccountToken: false in their ServiceAccount definitions.
Effect: Prevents automatic token injection into all pods, reducing the attack surface.
Requesting short-lived, audience-specific tokens via serviceAccountToken projection
Problem: Long-lived tokens can be reused indefinitely if leaked. Mitigation: You use projected service account tokens with: - audience: "sts.min.io" - A short expirationSeconds (e.g., 86400 = 24 hours, or even shorter)
Effect: Even if the token is leaked, it is:
- Only usable for sts.min.io
- Short-lived and expires soon
- Revocable by disabling the SA or STS access
Affected Versions and Risk Assessment
The issue affects MinIO Operator versions v5.0.x and above, when the STS feature was first introduced.
- In v5.0.x, STS was introduced as v1alpha1 and disabled by default. It required explicit API calls to be used.
- In v6.0.x, STS graduated to v1beta1 and was enabled by default, but still requires explicit calls to the STS API for token usage.
The risk is minimal, as:
- The Operator does not persist the token (neither in memory nor on disk).
- The Operator only uses the token for a single validation and does not reuse it for any other purpose.
Release
Fix released in v7.1.0
{
"affected": [
{
"package": {
"ecosystem": "Go",
"name": "github.com/minio/operator"
},
"ranges": [
{
"events": [
{
"introduced": "0"
},
{
"fixed": "7.1.0"
}
],
"type": "ECOSYSTEM"
}
]
}
],
"aliases": [
"CVE-2025-32963"
],
"database_specific": {
"cwe_ids": [
"CWE-522"
],
"github_reviewed": true,
"github_reviewed_at": "2025-04-21T22:51:11Z",
"nvd_published_at": "2025-04-22T18:16:00Z",
"severity": "MODERATE"
},
"details": "# Prevent token leakage / privilege escalation\n\n## MinIO Operator STS: A Quick Overview\n\nMinIO Operator STS is a native IAM Authentication for Kubernetes. MinIO Operator offers support for [Secure Tokens](https://min.io/docs/minio/linux/developers/security-token-service.html?ref=op-gh) (a.k.a. STS) which are a form of temporary access credentials for your MinIO Tenant. In essence, this allows you to control access to your MinIO tenant from your applications without having to explicitly create credentials for each application.\n\nFor an application to gain access into a MinIO Tenant, a `PolicyBinding` resource is required, granting explicit access to the applications by validating the kubernetes [Service Account](https://kubernetes.io/docs/concepts/security/service-accounts/) authorization token. \n\nThe service account token is validated as follows:\n\n1. The application calls `AssumeRoleWithWebIdentity` API MinIO Operator provides.\n2. MinIO Operator verifies the Service Account token agains the kubernetes API using the [TokenReview API](https://kubernetes.io/docs/reference/kubernetes-api/authentication-resources/token-review-v1/)\n3. MinIO Operator reviews the TokenReviewResult confirms if the token is a valid token and the user is authenticated.\n4. MinIO Operator validates the service account has `PolicyBinding` in the Tenant namespace.\n5. MinIO Operator gets the PolicyBinding\n6. MinIO Operator calls the AssumeRole API in the MinIO Tenant\n7. MinIO Operator obtains temporary credentials (STS).\n8. MinIO Operator return temporary Credentials to the requester application.\n9. The applicaiton consumes Object Storage using the temporary credentials.\n\n\n\n## Understanding Audiences in Kubernetes TokenReview\n\nIn step 2 the `TokenReview` API call attempts to authenticate a token to a known user, TokenReviewStatus is the result of the `TokenReview` request.\n\nAudiences are audience identifiers chosen by the authenticator that are compatible with both the TokenReview and token. \n\nAn identifier is any identifier in the intersection of the TokenReviewSpec audiences and the token\u0027s audiences.\n\nA client of the TokenReview API that sets the `spec.audiences` field should validate that a compatible audience identifier is returned in the status.audiences field to ensure that the TokenReview server is audience aware. \n**If no audiences are provided, the audience will default to the audience of the Kubernetes apiserver.**\n\n## Solution: Properly Issuing and Using Audience-Specific ServiceAccount Tokens\n\nThis PR ensures the Operator STS service request the Service Account JWT to belong to the audience`sts.min.io` in the TokenReviewRequest.\n\nThis PR ensures the examples and documentation provided guides in how to create Service accounts with \"disabled auto mount services tokens\", by doing this the pods where the service account is used no longer mounts the service account automatically in the path `/var/run/secrets/kubernetes.io/serviceaccount`.\n\nFor illustrative purposes, here is how you disable auto mount of service account tokens at the service account level.\n\n```yaml\napiVersion: v1\nkind: ServiceAccount\nmetadata:\n namespace: namespace-name\n name: service-account name\nautomountServiceAccountToken: false\n```\n\nAdditionally documentation and examples show how to request an audience-specific token with audience `sts.min.io`, by asking for an ServiceAccount Token to be audience specific.\n\nFor illustrative purposes, here is how you request an audience specific service account token in a pod:\n\n```yaml\napiVersion: batch/v1\nkind: Job\nmetadata:\n name: job-name\n namespace: job-namespace\nspec:\n template:\n spec:\n serviceAccountName: service-account-name\n volumes:\n - name: sa-token\n projected:\n sources:\n - serviceAccountToken:\n audience: \"sts.min.io\"\n expirationSeconds: 86400\n path: token\n containers:\n - name: mc\n...\n volumeMounts:\n - name: sa-token\n mountPath: /var/run/secrets/sts.min.io/serviceaccount\n readOnly: true\n```\n\n### How this prevent a token leakage or possible privilege escalation?.\n\nThis setup prevents privilege escalation and token leakage by combining multiple defense-in-depth mechanisms that ensure service account tokens are only usable by their intended audience, short-lived, and not exposed unnecessarily.\n\n#### Audience restriction (aud: sts.min.io)\n\n**Problem**: A ServiceAccount token is often valid for multiple audiences (e.g., the default Kubernetes API server). Without scoping, it can be replayed to other internal systems, which may unintentionally trust it.\n\n**Mitigation**: Now we enforce that tokens are explicitly created for the sts.min.io audience using the Kubernetes TokenRequest API, and the MinIO Operator:\n\nSends audiences: [\"sts.min.io\"] in the TokenReview.\n\nVerifies that the token was issued with this audience via status.audiences.\n\n**Effect**: Even if a token is stolen or misused, it will fail validation if used outside the sts.min.io STS endpoint (e.g., reused at the API server or another service).\n\n#### Token Leakage Mitigation\n\nDisabling auto-mounted service account tokens\n\n**Problem**: By default, Kubernetes mounts long-lived service account tokens into all pods at `/var/run/secrets/kubernetes.io/serviceaccount`, making them vulnerable to theft if the container is compromised.\n\n**Mitigation**: No we guide users to set `automountServiceAccountToken: false` in their ServiceAccount definitions.\n\n**Effect**: Prevents automatic token injection into all pods, reducing the attack surface.\n\n#### Requesting short-lived, audience-specific tokens via serviceAccountToken projection\n\n**Problem**: Long-lived tokens can be reused indefinitely if leaked.\n**Mitigation**: You use projected service account tokens with: \n- audience: \"sts.min.io\"\n- A short expirationSeconds (e.g., 86400 = 24 hours, or even shorter)\n\n**Effect**: Even if the token is leaked, it is:\n\n- Only usable for sts.min.io\n- Short-lived and expires soon\n- Revocable by disabling the SA or STS access\n\n## Affected Versions and Risk Assessment\nThe issue affects MinIO Operator versions v5.0.x and above, when the STS feature was first introduced.\n\n* In v5.0.x, STS was introduced as v1alpha1 and disabled by default. It required explicit API calls to be used.\n* In v6.0.x, STS graduated to v1beta1 and was enabled by default, but still requires explicit calls to the STS API for token usage.\n\nThe risk is minimal, as:\n\n* The Operator does not persist the token (neither in memory nor on disk).\n* The Operator only uses the token for a single validation and does not reuse it for any other purpose.\n\n# Release\nFix released in [v7.1.0](https://github.com/minio/operator/releases/tag/v7.1.0)",
"id": "GHSA-7m6v-q233-q9j9",
"modified": "2026-01-23T17:16:26Z",
"published": "2025-04-21T22:51:11Z",
"references": [
{
"type": "WEB",
"url": "https://github.com/minio/operator/security/advisories/GHSA-7m6v-q233-q9j9"
},
{
"type": "ADVISORY",
"url": "https://nvd.nist.gov/vuln/detail/CVE-2025-32963"
},
{
"type": "WEB",
"url": "https://github.com/minio/operator/commit/d586294d526bf0d8e6097225114655f68b0adcc5"
},
{
"type": "PACKAGE",
"url": "https://github.com/minio/operator"
},
{
"type": "WEB",
"url": "https://github.com/minio/operator/releases/tag/v7.1.0"
}
],
"schema_version": "1.4.0",
"severity": [
{
"score": "CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:N/VA:N/SC:N/SI:N/SA:N",
"type": "CVSS_V4"
}
],
"summary": "Minio Operator uses Kubernetes apiserver audience for AssumeRoleWithWebIdentity STS"
}
OPENSUSE-SU-2025:15017-1
Vulnerability from csaf_opensuse - Published: 2025-04-23 00:00 - Updated: 2025-04-23 00:00Sightings
| Author | Source | Type | Date | Other |
|---|
Nomenclature
- Seen: The vulnerability was mentioned, discussed, or observed by the user.
- Confirmed: The vulnerability has been validated from an analyst's perspective.
- Published Proof of Concept: A public proof of concept is available for this vulnerability.
- Exploited: The vulnerability was observed as exploited by the user who reported the sighting.
- Patched: The vulnerability was observed as successfully patched by the user who reported the sighting.
- Not exploited: The vulnerability was not observed as exploited by the user who reported the sighting.
- Not confirmed: The user expressed doubt about the validity of the vulnerability.
- Not patched: The vulnerability was not observed as successfully patched by the user who reported the sighting.
The approach is described in our paper Mapping CVEs to MITRE ATT&CK Techniques: A Curated Gold-Set Classifier and the Limits of LLM-Assisted Label Expansion.